Enhancing Office 365’s detection and antispam
Credit to Author: Nikolay Pankov| Date: Thu, 19 Jul 2018 15:33:13 +0000
To be safe, augment the service’s default protection.
Read MoreRSS Reader for Computer Security Articles
Credit to Author: Nikolay Pankov| Date: Thu, 19 Jul 2018 15:33:13 +0000
To be safe, augment the service’s default protection.
Read More
Credit to Author: Jonny Evans| Date: Mon, 23 Jul 2018 06:51:00 -0700
You may have missed an all-new enterprise-focused feature woven inside of Apple’s all-new MacBook Pro – its new T2 chip which fundamentally enhances the security of these computers.
The successor to the T1, Apple’s T2 chip enables secure boot and encrypted storage on the machine. It first appeared on the iMac Pro.
The most widely-reported task handled by the T2 chip is the provision of “Hey Siri” support for the first time on a Mac.
Credit to Author: Rajiv Singha| Date: Mon, 23 Jul 2018 14:13:28 +0000
Quick Heal Total Security (Windows) has achieved a 99.5% protection rate in the Real-World Protection Test conducted by world’s leading security software testers AV-Comparatives. Real-World Protection Test February-June 2018 Experts at AV-Comparatives create a real-world environment to test security software. In this environment, malware (malicious software) behave in the same…
Read More
Credit to Author: Woody Leonhard| Date: Mon, 23 Jul 2018 05:15:00 -0700
Microsoft’s July 2018 series of patching missteps, with .Net security patches in particular, have left many admins in the lurch. Less than two weeks after they were first unleashed, poorly documented versions of the patches now appear to be available, but are not being actively pushed. There’s no indication from Microsoft if and/or when they’ll be fixed.
These patches, originally released on Patch Tuesday, July 10, are baring their FAANGs:
The patches had been out for less than a day when we started seeing error reports on AskWoody. As I noted on July 12:
Credit to Author: BrianKrebs| Date: Mon, 23 Jul 2018 11:34:38 +0000
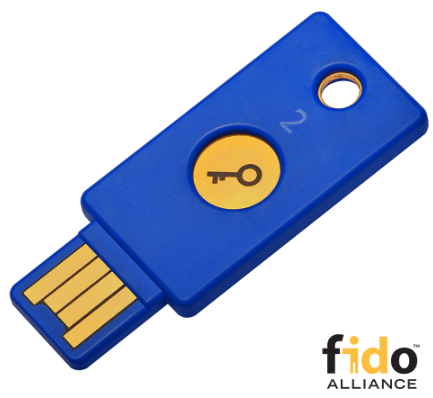
Google has not had any of its 85,000+ employees successfully phished on their work-related accounts since early 2017, when it began requiring all employees to use physical Security Keys in place of passwords and one-time codes, the company told KrebsOnSecurity.
Read MoreCredit to Author: Sharky| Date: Mon, 23 Jul 2018 03:00:00 -0700
This company is the target of a spear-phishing attack, but it doesn’t actually get very far, according to an IT pilot fish working there.
“It was the typical ‘CEO is out of the office and needs a wire transfer done right away’ message,” fish says.
“Our people are pretty good at spotting phishing attempts, and our administrative assistant was immediately suspicious because we do wire transfers approximately never. She strung the guy along over multiple emails and got all the transfer information — amount, routing number, account number and so on.
In this episode, Michael Feiertag, CEO and co-founder of tCell, joins host Steve Ragan to talk about why application security is more critical than ever and why it's just now getting more attention from security teams.
Credit to Author: Brian Barrett| Date: Sun, 22 Jul 2018 11:00:00 +0000
Two-factor authentication is a must, but don’t settle for the SMS version. Use a more secure authenticator app instead.
Read More