Author: admin

ComputerWorldIndependent

Third party antivirus programs interfere with Windows Defender critical patch

Credit to Author: Michael Horowitz| Date: Wed, 10 May 2017 15:37:00 -0700

Like others running Windows, I have been dutifully updating Window Defender the last few days with a fix for a critical bug. The update procedure is simple. Open the Control Panel, click on Windows Defender, and then check for updates.

The only thing out of the ordinary, on Windows 7, is that the update check is hidden behind a downward pointing triangle just to the right of a white question mark (this is not true in Windows 8 or 10). The “about” panel is also here. If the Engine Version is less than 1.1.13704.0 then it needs to be updated immediately.

To read this article in full or to leave a comment, please click here

Read More
SecuritySophos

How you helped give Sophos its security heartbeat

Credit to Author: Bill Brenner| Date: Wed, 10 May 2017 21:49:42 +0000

You said antivirus itself was no longer enough – and we brought you Sophos Synchronized Security in a heartbeat<img alt=”” border=”0″ src=”https://pixel.wp.com/b.gif?host=news.sophos.com&#038;blog=834173&#038;post=33566&#038;subd=sophos&#038;ref=&#038;feed=1″ width=”1″ height=”1″ /><img src=”http://feeds.feedburner.com/~r/sophos/dgdY/~4/qsKX3Zb2ym0″ height=”1″ width=”1″ alt=””/>

Read More
IndependentSecuriteam

SSD Advisory – Cisco DPC3928 Router Arbitrary File Disclosure

Credit to Author: SSD / Maor Schwartz| Date: Wed, 10 May 2017 07:43:17 +0000

Vulnerability Summary The following advisory describes an arbitrary file disclosure vulnerability found in Cisco DPC3928AD DOCSIS 3.0 2-PORT Voice Gateway. The Cisco DPC3928AD DOCSIS is a home wireless router that is currently "Out of support" but is provided by ISPs world wide. Credit An independent security researcher has reported this vulnerability to Beyond Security’s SecuriTeam … Continue reading SSD Advisory – Cisco DPC3928 Router Arbitrary File Disclosure

Read More
ComputerWorldIndependent

Schools in Alabama warn parents about Blue Whale ‘suicide game’ app

Credit to Author: Darlene Storm| Date: Wed, 10 May 2017 10:44:00 -0700

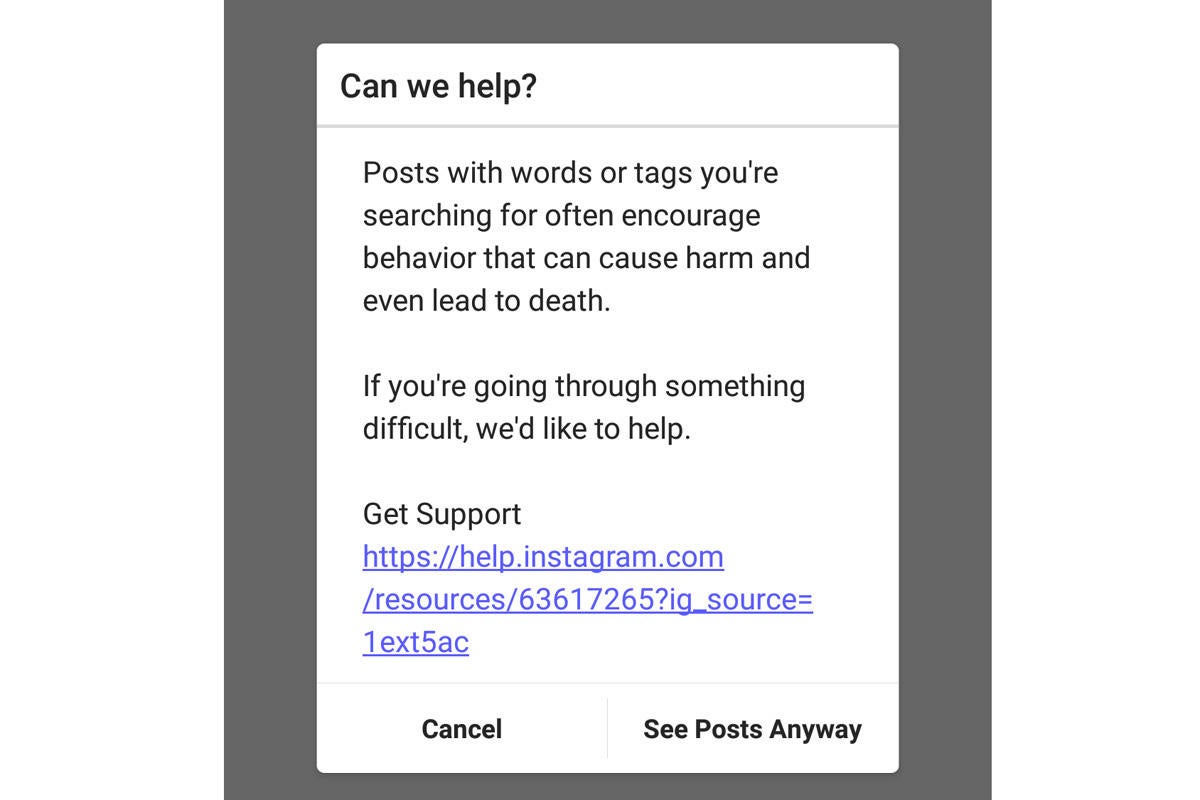
A “suicide game” presented in an app sounds like an urban legend or something from a horror flick, but unfortunately the “Blue Whale Challenge” is real. In fact, police and school districts have issued warnings about the app and even Instagram serves up a warning after searching for the #bluewhalechallenge.

blue whale challenge instagram message IDG

Vulnerable young people are the targets for Blue Whale. Once the app is downloaded onto a phone, it reportedly hacks the phone and harvests the user’s information. In the Blue Whale Challenge, a group administrator – also referenced as a mentor or master – gives a young person a task to complete each day for 50 days. If a person balks at the daily task, then the personal information which was stolen is used as a form of blackmail as in do this or else your private information will be released or your family threatened. The task on the last day is to commit suicide. This is supposedly winning the game.

To read this article in full or to leave a comment, please click here
Read More
FortinetSecurity

Security Research News in Brief – April 2017 Edition

Credit to Author: Axelle Apvrille| Date: Wed, 10 May 2017 09:08:47 -0700

Welcome back to our monthly review of some of the most interesting security research publications. Previous edition: March 2017   What happened to your home? IoT Hacking and Forensic with 0-day from TROOPERS 17, by Park and Jin Figure 1: Hacking a vacuum cleaner The authors hacked a vacuum cleaner, which, besides cleaning, also includes an embedded camera and microphone. The hack wasn’t easy because the vacuum wasn’t too badly secured. The authors however found 2 vectors: 1. They connected on the…

Read More
ComputerWorldIndependent

Microsoft finally bans SHA-1 certs in IE and Edge

Credit to Author: Lucian Constantin| Date: Wed, 10 May 2017 09:08:00 -0700

The Tuesday updates for Internet Explorer and Microsoft Edge force those browsers to flag SSL/TLS certificates signed with the aging SHA-1 hashing function as insecure. The move follows similar actions by Google Chrome and Mozilla Firefox earlier this year.

Browser vendors and certificate authorities have been engaged in a coordinated effort to phase out the use of SHA-1 certificates on the web for the past few years, because the hashing function no longer provides sufficient security against spoofing.

SHA-1 (Secure Hash Algorithm 1) dates back to 1995 and has been known to be vulnerable to theoretical attacks since 2005. The U.S. National Institute of Standards and Technology has banned the use of SHA-1 by U.S. federal agencies since 2010, and digital certificate authorities have not been allowed to issue SHA-1-signed certificates since Jan. 1, 2016, although some exemptions have been made — for example, for outdated payment terminals.

To read this article in full or to leave a comment, please click here

Read More
IndependentKrebs

SSA.GOV To Require Stronger Authentication

Credit to Author: BrianKrebs| Date: Wed, 10 May 2017 13:01:13 +0000

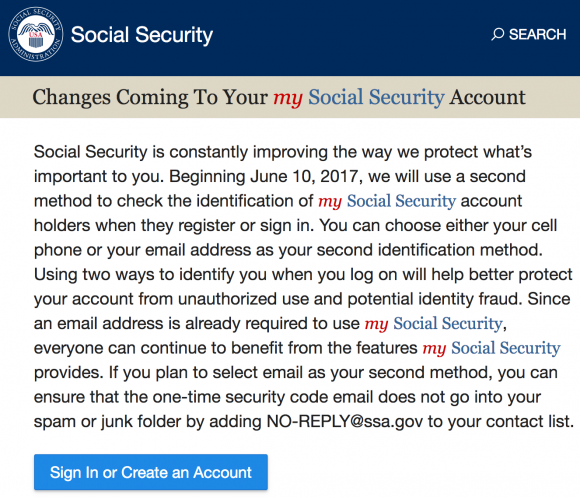
The U.S. Social Security Administration will soon require Americans to use stronger authentication when accessing their accounts at ssa.gov. As part of the change, SSA will require all users to enter a username and password in addition to a one-time security code sent their email or phone. In this post, we’ll parse this a bit more and look at some additional security options for SSA users.

Read More