Author: admin

MalwareBytesSecurity

Do I have Malwarebytes or a tech support scam?

Credit to Author: William Tsing| Date: Tue, 25 Apr 2017 15:00:49 +0000

A lot of companies don’t make it all too clear who their tech support is. Given the wide variety in how legitimate companies handle their support, how can you tell the difference between tech support and a tech support scam? We point out how to differentiate us from a tech support scammer.

Categories:

Tags:

(Read more…)

The post Do I have Malwarebytes or a tech support scam? appeared first on Malwarebytes Labs.

Read More
IndependentKrebs

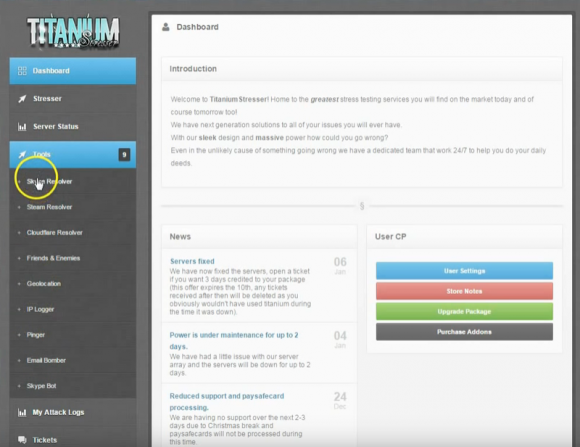
UK Man Gets Two Years in Jail for Running ‘Titanium Stresser’ Attack-for-Hire Service

Credit to Author: BrianKrebs| Date: Tue, 25 Apr 2017 15:06:34 +0000

A 20-year-old man from the United Kingdom was sentenced to two years in prison today after admitting to operating and selling access to “Titanium Stresser,” a simple-to-use service that let paying customers launch crippling online attacks against Web sites and individual Internet users. Adam Mudd of Herfordshire, U.K. admitted to three counts of computer misuse connected with his creating and operating the attack service, also known as a “stresser” or “booter” tool. Services like Titanium Stresser coordinate so-called “distributed denial-of-service” or DDoS attacks that hurl huge barrages of junk data at a site in a bid to make it crash or become otherwise unreachable to legitimate visitors.

Read More
MalwareBytesSecurity

How to fight security fatigue

Credit to Author: Wendy Zamora| Date: Tue, 25 Apr 2017 14:00:55 +0000

We live in the age of the 24-hour news cycle. Each day, whether it’s from TV news, phone notifications, online browsing, social media, or even the good old fashioned paper, we hear stories of the increasing dangers of cybercrime. Cyberthreats are growing more serious! Russian hacker starts his own ransomware service! Experts say tech support…

Categories:

Tags:

(Read more…)

The post How to fight security fatigue appeared first on Malwarebytes Labs.

Read More
SecurityTrendMicro

A Storm’s a Coming: How businesses can defend against threat actor groups like Pawn Storm

Credit to Author: Ed Cabrera (Chief Cybersecurity Officer)| Date: Tue, 25 Apr 2017 14:00:47 +0000

It's critical to hire a CISO that has experience and can lead a team.Pawn Storm (aka Sednit5, Fancy Bear, APT28, Sofacy and STRONTIUM8) might sound like Instagram accounts, top-secret spy programs or recently passed legislation, but in reality they are all different names for the same successful cyber espionage group (or threat actor group). These actors often use multi-angle bombardment attacks on the same target, implementing multiple methods…

Read More
FortinetSecurity

The Critical Need for MSSPs

Credit to Author: Steven Yurkunas| Date: Tue, 25 Apr 2017 07:23:06 -0700

Congratulations, you built a company worth breaking into! Seriously – there are, right now, Criminal Enterprises that are executing deliberate and methodical plans of attack in order to breach your company and strip it of its most valuable assets. Cybercrime is a multi-billion dollar business, and cybercriminals capitalize on finding new ways to exploit increasingly complex network environments like yours. To stay ahead of detection technologies, cybercriminals are continually developing new techniques and resources to bypass security and…

Read More
SecurityTrendMicro

Pawn Storm: The Power of Social Engineering

Credit to Author: Ed Cabrera (Chief Cybersecurity Officer)| Date: Tue, 25 Apr 2017 12:00:02 +0000

Anyone familiar with Pawn Storm (a.k.a. APT28, Fancy Bear, Strontium, etc.) is likely to associate the group with highly sophisticated targeted attacks that compromise government and media agencies around the world. In our latest report, researchers expose the true nature and scope of the cyber espionage group’s attacks and methodologies. Pawn Storm has managed to…

Read More
QuickHealSecurity

Anatomy of Flash Exploit (CVE-2015-8651) integrated into Rig Exploit Kit

Credit to Author: Pavankumar Chaudhari| Date: Tue, 25 Apr 2017 08:58:48 +0000

We all know how the infamous RIG Exploit Kit have been used to infect the end users. We are seeing a constant spike in the usage of the RIG Exploit Kit by malware actors to spread malware. Its use has been noticed in different campaigns such as EITest, pseudoDarkleech, and…

The post Anatomy of Flash Exploit (CVE-2015-8651) integrated into Rig Exploit Kit appeared first on Quick Heal Technologies Security Blog | Latest computer security news, tips, and advice.

Read More