Author: admin

SecurityTrendMicro

Deep Security 10: Customer Driven Development with TRC

Credit to Author: Justin Foster| Date: Wed, 08 Mar 2017 13:00:53 +0000

At least that used to be the standard software development process. Customers were involved in feedback quite late in the development process, often after the release has been mostly formed. We recently shared how Deep Security 10 is an example of server security standing the test of time but it was also the first release…

Read More
ComputerWorldIndependent

CIA-made malware? Now antivirus vendors can find out

Credit to Author: Michael Kan| Date: Wed, 08 Mar 2017 04:29:00 -0800

Thanks to WikiLeaks, antivirus vendors will soon be able to figure out if you have been hacked by the CIA.

On Tuesday, WikiLeaks dumped a trove of 8,700 documents that allegedly detail the CIA’s secret hacking operations, including spying tools designed for mobile phones, PCs and smart TVs.

WikiLeaks has redacted the source code from the files to prevent the distribution of cyber weapons, it said. Nevertheless, the document dump — if real — still exposes some of the techniques that the CIA has allegedly been using.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Senate resolution aims to roll back privacy rules for ISPs

Credit to Author: John Ribeiro| Date: Wed, 08 Mar 2017 03:57:00 -0800

A resolution introduced in the U.S. Senate on Tuesday aims to roll back privacy rules for broadband service providers that were approved by the Federal Communications Commission in October.

The rules include the requirement that internet service providers like Comcast, AT&T, and Verizon obtain “opt-in” consent from consumers to use and share sensitive personal information such as geolocation and web browsing history and also give customers the choice to opt out from the sharing of non-sensitive information such as email addresses or service tier information.

The rules have been opposed by ISPs that argue that they are being treated differently from other Internet entities like search engines and social networking companies.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Apple says it has already patched ‘many’ (not all) leaked CIA exploits

Credit to Author: Jonny Evans| Date: Wed, 08 Mar 2017 03:51:00 -0800

Details concerning multiple iOS, Mac, and AirPort exploits allegedly used by the CIA were published by Wikileaks late last night.

The documents reveal an extensive quantity of exploits used against Apple devices, thought WikiLeaks has not published any of the technical details or computer code that was also leaked to prevent these hacks disseminating any further. (Though we don’t know who else got the data).

Post-privacy

The documents offer the deepest look yet into how intelligence services (including the CIA, GCHQ, and others) have worked together to undermine the security of products from multiple vendors, including Apple.

To read this article in full or to leave a comment, please click here

Read More
IndependentKrebs

Payments Giant Verifone Investigating Breach

Credit to Author: BrianKrebs| Date: Tue, 07 Mar 2017 18:02:30 +0000

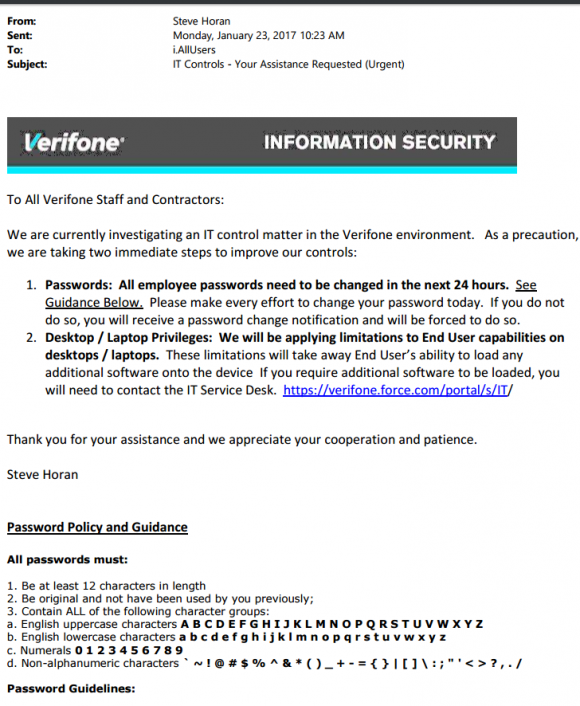
Credit and debit card payments giant Verifone [NYSE: PAY] is investigating a breach of its corporate computer networks that could impact companies running its point-of-sale solutions, according to multiple sources. Verifone says the extent of the breach was “limited” and that its payment services network was not impacted. San Jose, Calif.-based Verifone is the largest maker of credit card terminals used in the United States. It sells point-of-sale terminals and services to support the swiping and processing of credit and debit card payments at a variety of businesses, including retailers, taxis, and fuel stations. On Jan. 23, 2017, Verifone sent an “urgent” email to all company staff and contractors, telling them that they had 24 hours to change all company passwords.

Read More