Security Benefits of Cloud Automation
Credit to Author: Andrew Stevens| Date: Tue, 18 Apr 2023 00:00:00 +0000
Learn more about how cloud automation can simplify security controls, policies, and scans.
Read MoreRSS Reader for Computer Security Articles
Credit to Author: Andrew Stevens| Date: Tue, 18 Apr 2023 00:00:00 +0000
Learn more about how cloud automation can simplify security controls, policies, and scans.
Read More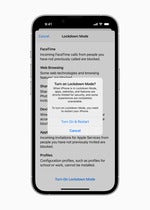
No matter what US President Joseph R. Biden Jr. said, NSO Group is still around; the privatized spying service produced zero-click exploits against iOS 15 and iOS 16 last year, according to the latest report from Citizen Lab.
It also suggests Lockdown Mode is effective against such attacks.
The report reflects what Citizen Lab learned from investigating attacks against Mexican human rights defenders. The researchers conclude that NSO Group, called “mercenary hackers” by Apple, has made wide use of at least three zero-click exploits in Apple’s iPhone operating systems against civil society targets worldwide. NSO Group is the infamous firm that created the Pegasus tool used to spy on people.
Credit to Author: Microsoft Security Threat Intelligence – Editor| Date: Tue, 18 Apr 2023 15:00:00 +0000
Microsoft is excited to announce that we are shifting to a new threat actor naming taxonomy aligned to the theme of weather. The complexity, scale, and volume of threats is increasing, driving the need to reimagine not only how Microsoft talks about threats but also how we enable customers to understand those threats quickly and with clarity.
The post Microsoft shifts to a new threat actor naming taxonomy appeared first on Microsoft Security Blog.
Read MoreCredit to Author: Microsoft Security Threat Intelligence| Date: Tue, 18 Apr 2023 15:00:00 +0000
Today, Microsoft is reporting on a distinct subset of Mint Sandstorm (formerly known as PHOSPHORUS), an Iranian threat actor that specializes in hacking into and stealing sensitive information from high-value targets. This subset is technically and operationally mature, capable of developing bespoke tooling and quickly weaponizing recently disclosed vulnerabilities.
The post Nation-state threat actor Mint Sandstorm refines tradecraft to attack high-value targets appeared first on Microsoft Security Blog.
Read More
Credit to Author: Alanna Titterington| Date: Tue, 18 Apr 2023 12:44:25 +0000
A newly discovered serious vulnerability means Google Chrome, Microsoft Edge, Opera, Yandex Browser, Vivaldi and other Chromium-based browsers should be updated immediately
Read MoreCredit to Author: Don Ovid Ladores| Date: Tue, 18 Apr 2023 00:00:00 +0000
This blog post analyzes a stealthy and expeditious ransomware called BabLock (aka Rorschach), which shares many characteristics with LockBit.
Read MoreCategories: Business Good tools gone bad. |
The post Living Off the Land (LOTL) attacks: Detecting ransomware gangs hiding in plain sight appeared first on Malwarebytes Labs.
Read MoreCategories: News In the last 12 months, Germany was one of the most attacked countries in the world, the most attacked in the EU, and a favourite target of the notorious Black Basta group. |
The post Ransomware in Germany, April 2022 – March 2023 appeared first on Malwarebytes Labs.
Read More