Most popular tech stories of 2019
Credit to Author: Dan Muse| Date: Mon, 30 Dec 2019 11:51:00 -0800
Insider Pro subscribers pick the Top 10 articles published in our debut year.
Read MoreRSS Reader for Computer Security Articles
Credit to Author: Dan Muse| Date: Mon, 30 Dec 2019 11:51:00 -0800
Insider Pro subscribers pick the Top 10 articles published in our debut year.
Read More
Credit to Author: BrianKrebs| Date: Mon, 30 Dec 2019 00:49:22 +0000
Today marks the 10th anniversary of KrebsOnSecurity.com! Over the past decade, the site has featured more than 1,800 stories focusing mainly on cybercrime, computer security and user privacy concerns. And what a decade it has been. Stories here have exposed countless scams, data breaches, cybercrooks and corporate stumbles. In the ten years since its inception, […]
Read More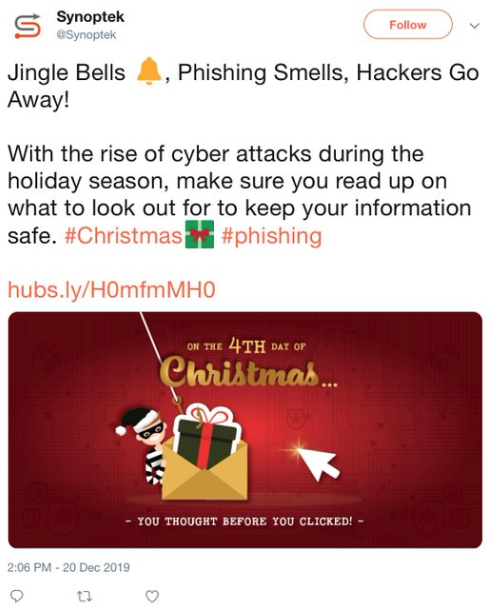
Credit to Author: BrianKrebs| Date: Sat, 28 Dec 2019 01:49:05 +0000
Synoptek, a California business that provides cloud hosting and IT management services to more than a thousand customer nationwide, suffered a ransomware attack this week that has disrupted operations for many of its clients, according to sources. The company has reportedly paid a ransom demand in a bid to restore operations as quickly as possible. Irvine, Calif.-based Synoptek is a managed service provider that maintains a variety of cloud-based services for more than 1,100 customers across a broad spectrum of industries, including state and local governments, financial services, healthcare, manufacturing, media, retail and software. The company employs nearly a thousand employees and brought in more than $100 million in revenue in the past year.
Read More
The new Apple Card, the battle for cryptocurrency dominance, cybersecurity skills shortage – just a few of the stories that made headlines in 2019. Watch as IDG TECH(talk) hosts Ken Mingis and Juliet Beauchamp discuss the top tech stories of the year.

This new Microsoft 365 feature can help you stay in compliance with regulations like GDPR and better protect data.
Credit to Author: Woody Leonhard| Date: Wed, 18 Dec 2019 05:57:00 -0800
Late last week, I talked about a discrepancy in Microsoft’s promised handling of Microsoft Security Essentials as Windows 7 reaches end of support. An internally inconsistent official announcement seemed to say that MSE signature file updates would stop — even for those who have paid for Extended Security Updates.
Which is absurd. Why would Microsoft stop updating its antivirus program even for people who are paying to continue receiving Monthly Rollup patches?
Credit to Author: Evan Schuman| Date: Wed, 18 Dec 2019 05:46:00 -0800
There is nothing more quintessentially mobile than text messages, the most commonly used communication method today. That’s why it was very unsettling that a security research house found — and the vendor at issue essentially confirmed — that a massive number of text messages were stored in plaintext, with no security at all. In short, the texts from what the security research firm estimated were “hundreds of millions of people” were open to any thief or stalker who wanted to look.
The company involved, an Austin-based business called TrueDialog, would likely be unknown to almost all of those users. TrueDialog is a marketing firm offering SMS products and services to other companies — a lot of companies. That will make it hard for consumers to even know if their texts were victimized. Text message users were able to text back, giving the impression of having two-way conversations with businesses.
Attackers often take advantage of the holidays to launch attacks. Use these Microsoft settings to deter them.