Independent

ComputerWorldIndependent

Microsoft starts releasing fixes for Access bugs introduced in Office security patches this month
Credit to Author: Woody Leonhard| Date: Tue, 19 Nov 2019 06:09:00 -0800

Although we’ve been promised no “C” or “D” week second cumulative updates for the rest of the year — at least for Windows — Microsoft has acknowledged a bug it created in last week’s Patch Tuesday Office patches, and now promises that it’ll update the bad fixes on most machines this week or next. Those are “C” week and “D” week, respectively.

The cause du jour: a bug in all of this month’s Office security patches that throws an error in Access saying, “Query xxxx is corrupt,” when in fact the query in question is just fine. Microsoft describes the erroneous error message on its Office Support site:
To read this article in full, please click here

Read More
IndependentKrebs

Why Were the Russians So Set Against This Hacker Being Extradited?

Credit to Author: BrianKrebs| Date: Mon, 18 Nov 2019 21:19:10 +0000

The Russian government has for the past four years been fighting to keep 29-year-old alleged cybercriminal Alexei Burkov from being extradited by Israel to the United States. When Israeli authorities turned down requests to send him back to Russia — supposedly to face separate hacking charges there — the Russians then imprisoned an Israeli woman for seven years on trumped-up drug charges in a bid to trade prisoners. That effort failed as well, and Burkov had his first appearance in a U.S. court last week. What follows are some clues that might explain why the Russians are so eager to reclaim this young man.

Read More
ComputerWorldIndependent

Mobile security perceptions don't approach reality. And that's a problem.

Credit to Author: Evan Schuman| Date: Mon, 18 Nov 2019 07:44:00 -0800

In general, security vendors love consumer surveys where consumers say that they would never, ever, ever do business with a retailer or a bank with poor security practices. But consumers have historically been terrible predictors of their own behavior, and they also tend to tell retailers and banks what they want to hear, rather than the truth.

And the truth, based on the public financial filings of plenty of companies that have suffered public data breaches, is that consumers — partially thanks to zero liability programs from the payment card companies — tend to not change retailers or banks when such data breaches happen. Why? Quite a few reasons. First, zero liability sees to it that they don’t lose any money (it actually limits losses to $50, but almost no business enforces that, and they tend to simply eat all of the consumer losses). If consumers lost large amounts of money from breached retailers or banks, yes, they’d flee, but that doesn’t happen.

To read this article in full, please click here

Read More
ComputerWorldIndependent

Balancing patient security with healthcare innovation | TECH(talk)


Healthcare organizations are one of the most targeted verticals when it comes to cyberattacks. While those organizations must work to secure patients' sensitive data, it can also be helpful to analyze that data to improve patient outcomes. Jason James, CIO of Net Health, joins Juliet to discuss why attackers target healthcare organizations, Google's Project Nightingale and what it means for a tech giant to have access to the medical data of millions of people.

Read More
IndependentKrebs

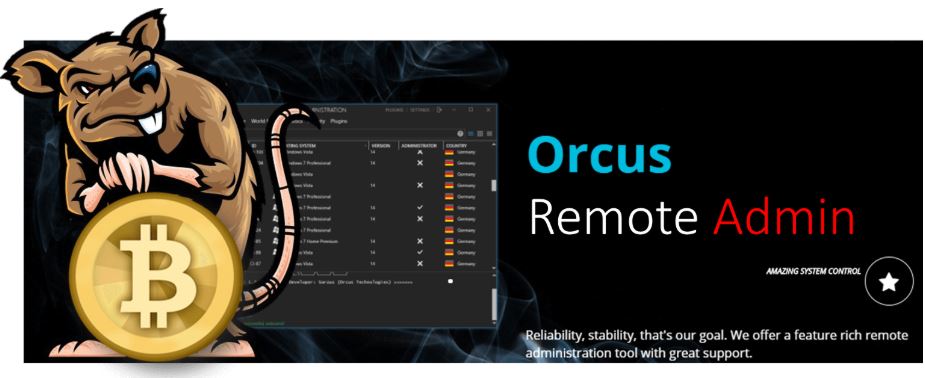
Orcus RAT Author Charged in Malware Scheme

Credit to Author: BrianKrebs| Date: Wed, 13 Nov 2019 15:41:17 +0000

In July 2016, KrebsOnSecurity published a story identifying a Toronto man as the author of the Orcus RAT, a software product that’s been marketed on underground forums and used in countless malware attacks since its creation in 2015. This week, Canadian authorities criminally charged him with orchestrating an international malware scheme.

Read More
ComputerWorldIndependent

Patch Tuesday arrives with Access error, 1909 in tow, and a promise of no more 'optional' patches this year

Credit to Author: Woody Leonhard| Date: Wed, 13 Nov 2019 07:59:00 -0800

The patches haven’t yet been out for 24 hours and already we’re seeing a lot of activity. Here’s where we stand with the initial wave of problems.

Malicious Software Removal Tool installation error 800B0109 

Many early patchers found that the MSRT, KB 890830, kept installing itself over and over again. Poster IndyPilot80 says:

It sits at “Installing: 0%” for a couple minutes then goes away. When I hit “Check for Updates” it shows up again and does the same thing.

To read this article in full, please click here

Read More