Independent

ComputerWorldIndependent

Cheers!

Credit to Author: Sharky| Date: Fri, 27 Sep 2019 03:00:00 -0700

Pilot fish has a sweet deal with one of the owners of a local drinking establishment he frequents. The bar owner is in the habit of using the main office computer for what fish calls “nonstandard business activity.” What does that mean? Suffice to say that that computer gets infected by viruses a couple of times a year. Bar owner would then call fish and ask for expedited service.

Fish stops by on his way home, grabs the tower, and disinfects the hard drive at home. He usually returns the system to the bar late that night or on his way to work the next morning.

Either way, the next time he stops by for an adult beverage, he receives a gift card that usually covers several rounds.
To read this article in full, please click here

Read More
IndependentKrebs

Interview With the Guy Who Tried to Frame Me for Heroin Possession

Credit to Author: BrianKrebs| Date: Thu, 26 Sep 2019 00:28:36 +0000

In April 2013, I received via U.S. mail more than a gram of pure heroin as part of a scheme to get me arrested for drug possession. But the plan failed and the Ukrainian mastermind behind it soon after was imprisoned for unrelated cybercrime offenses. That individual recently gave his first interview since finishing his jail time here in the states, and he’s shared some select (if often abrasive and coarse) details on how he got into cybercrime and why. Below are a few translated excerpts.

Read More
ComputerWorldIndependent

What do we know about the big, scary, exploited, emergency-patched IE security hole CVE-2019-1367?

Credit to Author: Woody Leonhard| Date: Wed, 25 Sep 2019 07:29:00 -0700

Read More
ComputerWorldIndependent

Apple just made Safari a better fit for the enterprise

Credit to Author: Jonny Evans| Date: Wed, 25 Sep 2019 07:15:00 -0700

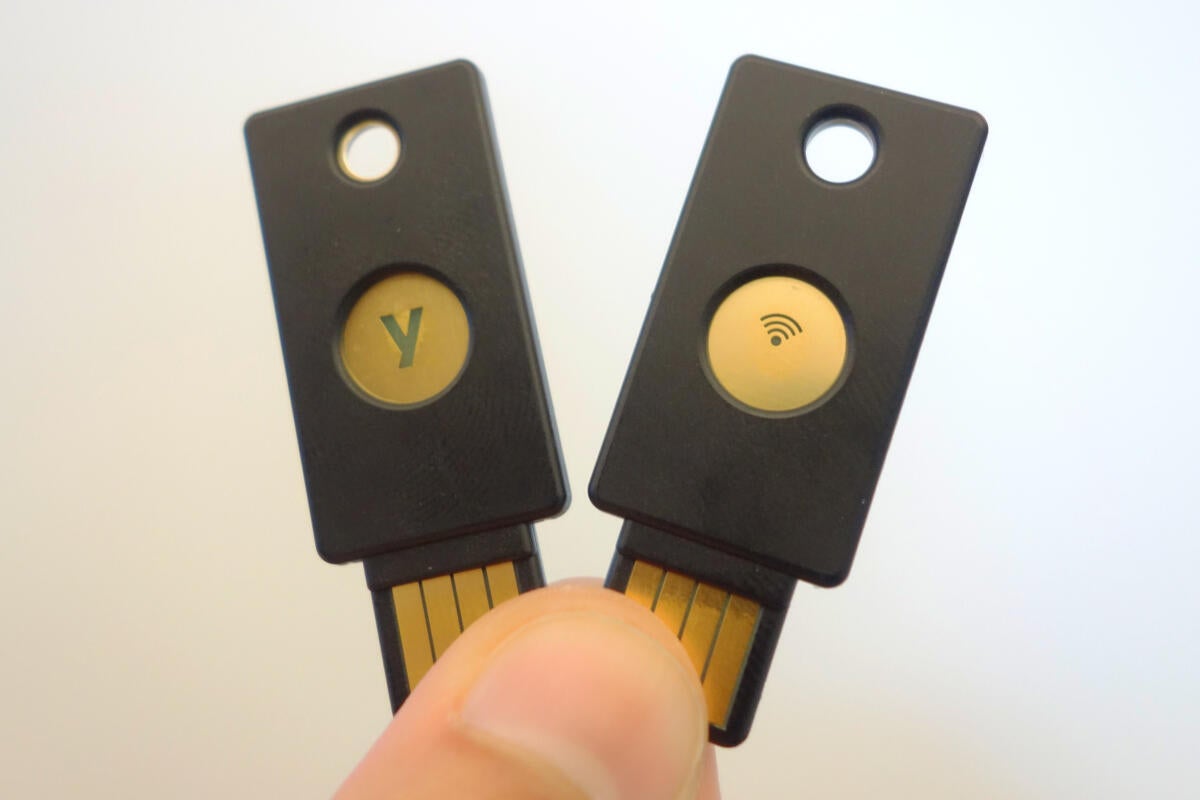
Enterprise users can now wrap a new layer of security around their web services, thanks to Apple’s introduction of support for USB security keys in Safari 13.0.1.

Enterprise class security

Dongles aren’t a terribly convenient security protection for most people, but government, military and regulated industries are always searching out new ways to secure themselves, and their data.

FIDO2-compliant USB security keys – such as those made by Yubico – add a layer of security to the verification process:

To read this article in full, please click here

Read More
ComputerWorldIndependent

Microsoft releases emergency IE patches inside 'optional, non-security' cumulative updates

Credit to Author: Woody Leonhard| Date: Tue, 24 Sep 2019 12:13:00 -0700

I’ve seen a lot of confusion about the security hole known as CVE-2019-1367 and what normal Windows customers should do about it. Part of the reason for the confusion is the way the fix was distributed – the patching files were released on Monday, Sept. 23, but only via manual download from the Microsoft Update Catalog.

On a Monday.

In the past few hours, Microsoft released a hodge-podge of patches that seem to tackle the problem. They’re “optional non-security” and “Monthly Rollup preview” patches, so you won’t get them unless you specifically go looking for them.

To read this article in full, please click here

Read More
ComputerWorldIndependent

Microsoft delivers emergency security update for antiquated IE

Credit to Author: Gregg Keizer| Date: Tue, 24 Sep 2019 03:00:00 -0700

Microsoft on Monday released an emergency security update to patch a vulnerability in Internet Explorer (IE), the legacy browser predominantly used by commercial customers.

The flaw, which was reported to Microsoft by Clement Lecigne, a security engineer with Google’s Threat Analysis Group (TAG), has already been exploited by attackers, making it a classic “zero-day,” a vulnerability actively in use before a patch is in place.

In the security bulletin that accompanied the release of the IE patch, Microsoft labeled the bug a remote code vulnerability, meaning that a hacker could, by exploiting the bug, introduce malicious code into the browser. Remote code vulnerabilities, also called remote code execution, or RCE, flaws, are among the most serious. That seriousness, as well as the fact that criminals are already leveraging the vulnerability, was reflected in Microsoft’s decision to go “out of band,” or off the usual patching cycle, to plug the hole.

To read this article in full, please click here

Read More
ComputerWorldIndependent

iOS 13: Apple's big BYOD improvements help enterprise pros

Credit to Author: Jonny Evans| Date: Mon, 23 Sep 2019 07:56:00 -0700

Apple may place much of its focus on Apple Arcade and consumer-friendly iPad/iPhone features, but there are numerous enterprise-focused enhancements wrapped up inside iOS 13.

The BYOD enterprise

The company’s latest operating systems introduce a host of productivity-enhancing upgrades, particularly for the iPad.

Yet the biggest improvements specifically for enterprise users aim to make a more robust division between personal and enterprise data for Bring Your Own Device (BYOD) deployments, solving one of the big challenges in the space.

To read this article in full, please click here

Read More