Independent

ComputerWorldIndependent

Mingis on Tech: Lessons from RSA 2018
Credit to Author: Ken Mingis| Date: Wed, 09 May 2018 03:30:00 -0700

This year’s RSA Conference in San Francisco had a lot of ground to cover. Cybersecurity, of course. Fending off ransomware attacks. Building security best practices into employee training.

But, according to CSO’s Steve Ragan, the hottest topics at the 2018 conference were this month’s looming GDPR deadline and blockchain, blockchain, blockchain. (In fact, the two are often part of the same conversation.)

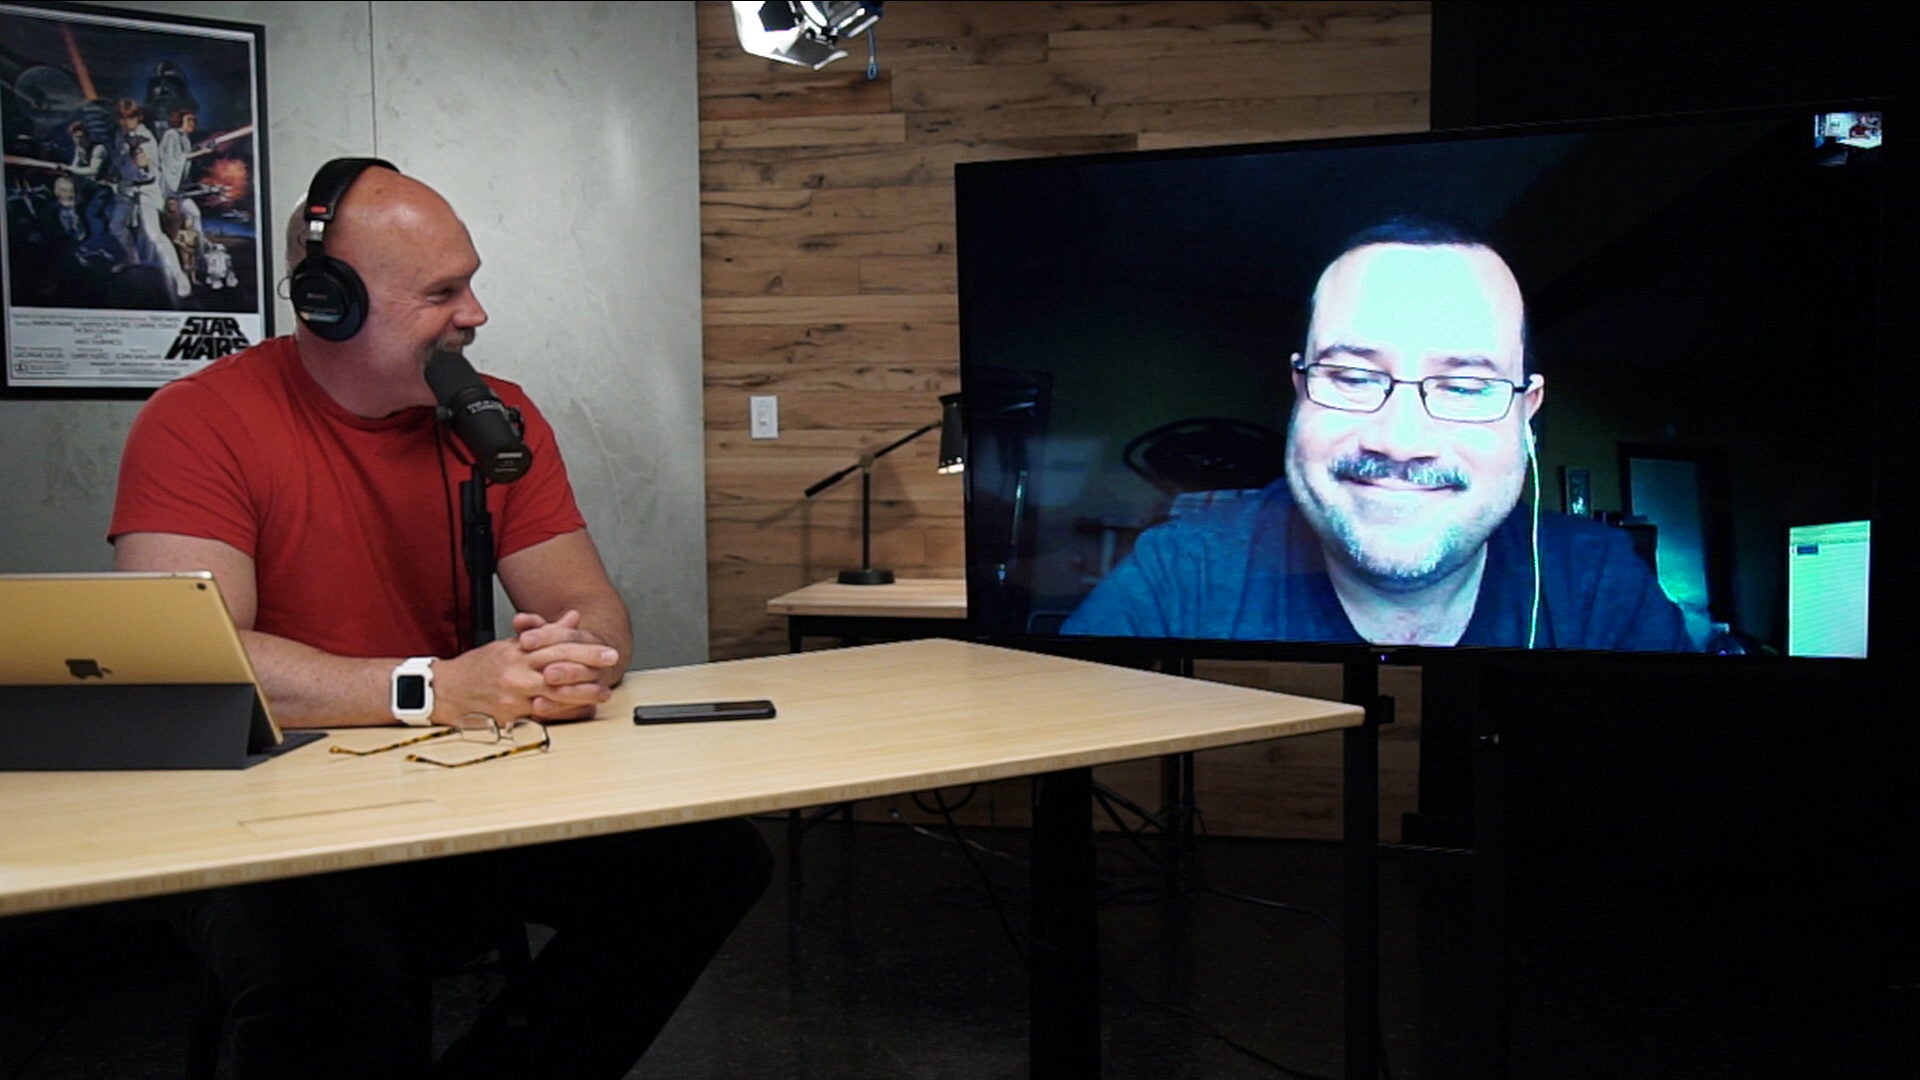
Ragan, who attended RSA, spoke with Computerworld Executive Editor Ken Mingis about what he learned, with a special focus on the May 25 GDPR deadline and what companies are scrambling to do to protect their data.
To read this article in full, please click here

Read More
IndependentKrebs

Microsoft Patch Tuesday, May 2018 Edition

Credit to Author: BrianKrebs| Date: Tue, 08 May 2018 20:38:16 +0000

Microsoft today released a bundle of security updates to fix at least 67 holes in its various Windows operating systems and related software, including one dangerous flaw that Microsoft warns is actively being exploited. Meanwhile, as it usually does on Microsoft’s Patch Tuesday — the second Tuesday of each month — Adobe has a new Flash Player update that addresses a single but critical security weakness. First, the Flash Tuesday update, which brings Flash Player to v. 29.0.0.171. Some (present company included) would argue that Flash Player is in itself “a single but critical security weakness.” Nevertheless, Google Chrome and Internet Explorer/Edge ship with their own versions of Flash, which get updated automatically when new versions of these browsers are made available.

Read More
IndependentKrebs

Study: Attack on KrebsOnSecurity Cost IoT Device Owners $323K

Credit to Author: BrianKrebs| Date: Mon, 07 May 2018 16:47:20 +0000

A monster distributed denial-of-service attack (DDoS) against KrebsOnSecurity.com in 2016 knocked this site offline for nearly four days. The attack was executed through a network of hacked “Internet of Things” (IoT) devices such as Internet routers, security cameras and digital video recorders. A new study that tries to measure the direct cost of that one attack for IoT device users whose machines were swept up in the assault found that it may have cost device owners a total of $323,973.75 in excess power and added bandwidth consumption. My bad.

Read More
ComputerWorldIndependent

Will blockchain run afoul of GDPR? (Yes and no)

Credit to Author: Lucas Mearian| Date: Mon, 07 May 2018 03:02:00 -0700

As the EU prepares to roll out new data protection regulations this month, concerns are emerging that they could dissuade businesses from rolling out blockchain-based projects because the online transaction technology might innately break the new rules.

The EU’s General Data Protection Regulation (GDPR) targets citizens’ personally identifiable information (PII), providing transparency around its use and giving people the right to restrict its use or request it be deleted all together.

While GDPR never mentions PII, the new rules describing “personal data” are synonymous with it: “Any information that relates to an identified or identifiable living individual. Different pieces of information, which collected together can lead to the identification of a particular person, also constitute personal data.” In short, it means any data that can be tied back to person’s identity.

To read this article in full, please click here

Read More
IndependentKrebs

Twitter to All Users: Change Your Password Now!

Credit to Author: BrianKrebs| Date: Thu, 03 May 2018 22:40:48 +0000

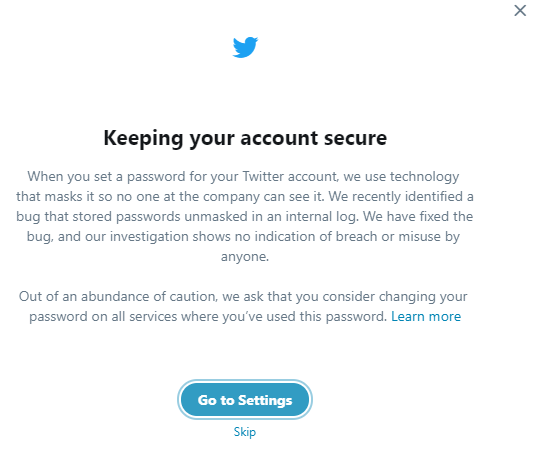
Twitter just asked all 300+ million users to reset their passwords, citing the exposure of user passwords via a bug that stored passwords in plain text — without protecting them with any sort of encryption technology that would mask a Twitter user’s true password. The social media giant says it has fixed the bug and that so far its investigation hasn’t turned up any signs of a breach or that anyone misused the information. But if you have a Twitter account, please change your account password now.

Read More
IndependentKrebs

When Your Employees Post Passwords Online

Credit to Author: BrianKrebs| Date: Wed, 02 May 2018 19:26:47 +0000

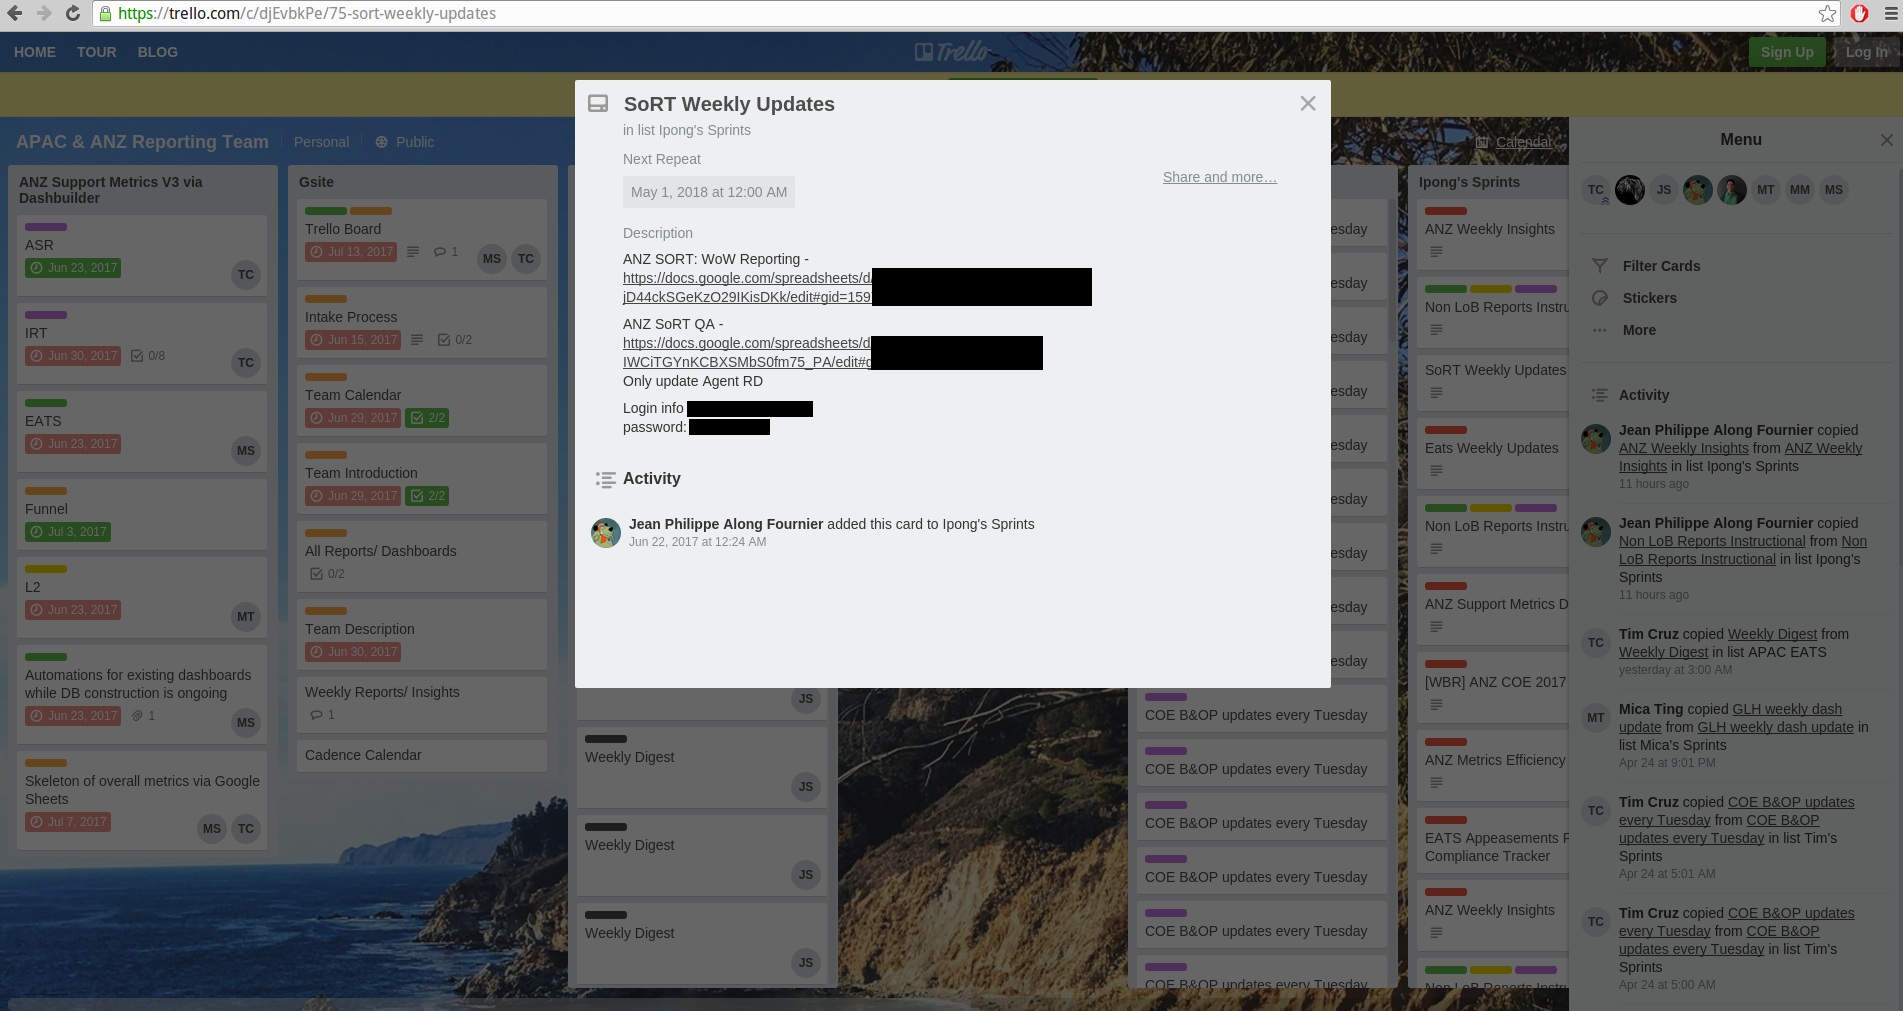
Storing passwords in plaintext online is never a good idea, but it’s remarkable how many companies have employees who are doing just that using online collaboration tools like Trello.com. Last week, KrebsOnSecurity notified a host of companies that employees were using Trello to share passwords for sensitive internal resources. Among those put at risk by such activity included an insurance firm, a state government agency and ride-hailing service Uber.com.

Read More