Independent

IndependentSecuriteam

SSD Advisory – TrustPort Management Unauthenticated Remote Code Execution
Credit to Author: SSD / Noam Rathaus| Date: Wed, 25 Apr 2018 08:36:14 +0000

Vulnerability Summary Multiple vulnerabilities in TrustPort’s management product allow remote unauthenticated attackers to cause the product to execute arbitrary code. TrustPort Management “offers you an effective and practical way to install centrally, configure and update antivirus software in your network and it enables mass administration of TrustPort products. Central administration from TrustPort brings you simple … Continue reading SSD Advisory – TrustPort Management Unauthenticated Remote Code Execution

Read More
ComputerWorldIndependent

Microsoft Patch Alert: April patches infested with bugs, but most are finally contained

Credit to Author: Woody Leonhard| Date: Wed, 25 Apr 2018 12:06:00 -0700

People think I’m joking when I refer to bug fixing as Microsoft’s next billion-dollar business. I’m not. This month woefully demonstrated why patching Windows has become much bigger – and more critical – than developing new versions. Microsoft’s hell-bent move to bring out new versions of Windows twice a year “as a service” makes things worse, but quality control problems dog patches to every version of Windows. Except, arguably, Windows 8.1.

In April, we’ve seen a return to two massive cumulative updates per month for all supported versions of Windows 10. The second cumulative update, with luck, fixes the bugs in the first cumulative update. Windows 7 turned into a fiery pit when it was discovered in late March that every patch to Win7 (and Server 2008R2) pushed out this year enables the Total Meltdown bug. Fortunately, by April 23, we finally saw some stability return to the process.

To read this article in full, please click here

Read More
IndependentKrebs

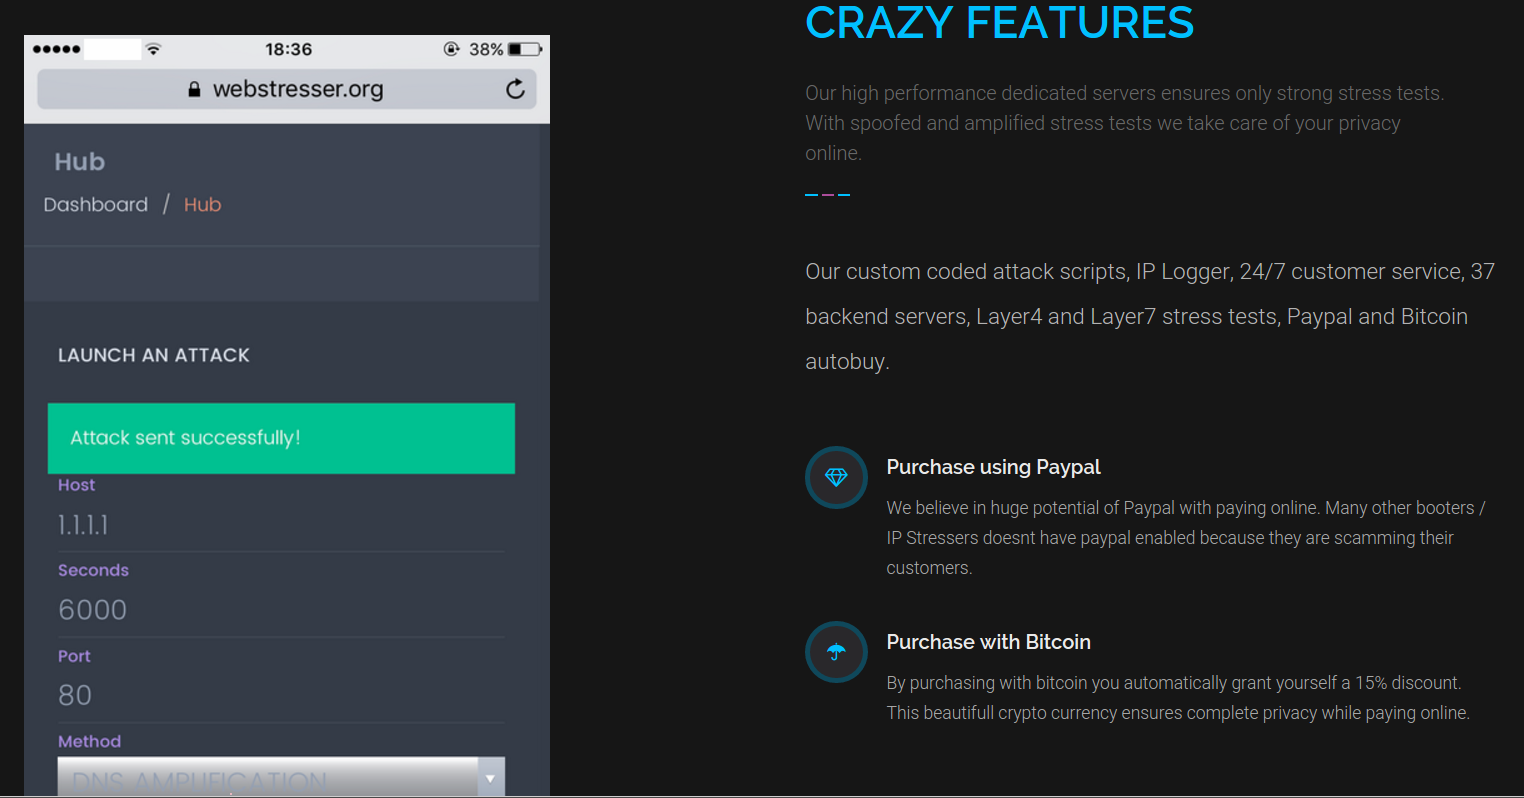
DDoS-for-Hire Service Webstresser Dismantled

Credit to Author: BrianKrebs| Date: Wed, 25 Apr 2018 17:41:37 +0000

Authorities in the U.S., U.K. and the Netherlands on Tuesday took down popular online attack-for-hire service WebStresser.org and arrested its alleged administrators. Investigators say that prior to the takedown, the service had more than 136,000 registered users and was responsible for launching somewhere between four and six million attacks over the past three years.

Read More
ComputerWorldIndependent

Why we love lawyers (well, OUR lawyers, anyway)

Credit to Author: Sharky| Date: Wed, 25 Apr 2018 03:00:00 -0700

This IT pilot fish has spent the past year and a half helping his company’s clients prepare for the European Union’s upcoming General Data Protection Regulation, and with a month to go, it’s been smooth sailing — mostly.

“Over the last 18 months I’ve been asking my customers time and again about their readiness to implement the GDPR rules,” says fish. “We have mostly small companies as our customers, family businesses and one-to-ten-person outfits, and most of them had need of our services one way or another.

“But one customer, a lawyer, told me every time that this particular set of rules does not apply to him, because everything he does is governed by an obligation to confidentiality. Ten weeks before the final date, he still thought it had nothing to do with him.”

To read this article in full, please click here

Read More
ComputerWorldIndependent

Heads up: Total Meltdown exploit code now available on GitHub

Credit to Author: Woody Leonhard| Date: Tue, 24 Apr 2018 13:33:00 -0700

Remember the Total Meltdown security hole? Microsoft spread the vulnerability in every 64-bit Win7 and Server 2008 R2 patch released this year, prior to March 29. Specifically, if you installed any of these patches:

  • KB 4056894 Win7/Server 2008 R2 January Monthly Rollup
  • KB 4056897 Win7/Server 2008 R2 January Security-only patch
  • KB 4073578 Hotfix for “Unbootable state for AMD devices in Windows 7 SP1 and Windows Server 2008 R2 SP1” bug installed in the January Monthly Rollup and Security-only patches
  • KB 4057400 Win7/Server 2008 R2 Preview of the February Monthly Rollup
  • KB 4074598 Win7/Server 2008 R2 February Monthly Rollup
  • KB 4074587 Win7/Server 2008 R2 February Security-only patch
  • KB 4075211 Win7/Server 2008 R2 Preview of the March Monthly Rollup
  • KB 4091290 Hotfix for “smart card based operations fail with error with SCARD_E_NO_SERVICE” bug installed in the February Monthly Rollup
  • KB 4088875 Win7/Server 2008 R2 March Monthly Rollup
  • KB 4088878 Win7/Server 2008 R2 March Security-only patch
  • KB 4088881 Win7/Server 2008 R2 Preview of April Monthly Rollup

… your machine was left in an exposed state. Microsoft made changes to your PC that makes it easy for a running to program to look at, or modify, any data on your computer.

To read this article in full, please click here

Read More
ComputerWorldIndependent

The missing cumulative update for Win10 1709 appeared overnight — KB 4093105

Credit to Author: Woody Leonhard| Date: Tue, 24 Apr 2018 07:20:00 -0700

Late last night — on a Monday, mind you — Microsoft released its second big cumulative update for Win10 version 1709. This completes the triumvirate of second cumulative updates, since last week, on the third Tuesday of the month, Microsoft released second cumulative updates for Win10 1703 and 1607. 

There’s a pattern emerging. Microsoft is now showering Win10 customers with two (sometimes more) cumulative updates a month, and they’re big. The first cumulative update contains security patches and a big hodgepodge of additional bug fixes. The first one is (usually) released on the second Tuesday of the month. The second cumulative update arrives, uh, whenever, and it contains massive amounts of bug fixes in addition to those in the first — including, if we’re lucky, fixes for the bugs introduced by the month’s first cumulative update.

To read this article in full, please click here

Read More
ComputerWorldIndependent

Mingis on Tech: All about Android security

Credit to Author: Ken Mingis| Date: Tue, 24 Apr 2018 03:30:00 -0700

One of the many topics techies like to debate is whether Google’s Android or Apple’s iOS is more inherently secure. Sure, Apple has a closed system that makes it harder for iPhone users to get into trouble. But the frequent headlines about Android malware usually miss the point.

As Computerworld‘s JR Raphael explains, an Android user would really have to work at picking up malware. Android has multiple layers of defense; malware doesn’t install itself without user intervention; and the chances of actually coming across damaging malware is really, really small.

To read this article in full, please click here

Read More
ComputerWorldIndependent

The best privacy and security apps for Android

Credit to Author: JR Raphael| Date: Tue, 24 Apr 2018 03:00:00 -0700

Let’s get one thing out of the way right off the bat: If you’re looking for recommendations about Android security suites or other malware-scanning software, you’ve come to the wrong place.

Why? Because, like most people who closely study Android, I don’t recommend using those types of apps at all. Android malware isn’t the massive real-world threat it’s frequently made out to be, and Google Play Protect and other native Android features are more than enough to keep most devices safe.

To read this article in full, please click here

Read More