Independent

IndependentKrebs

Adrian Lamo, ‘Homeless Hacker’ Who Turned in Chelsea Manning, Dead at 37
Credit to Author: BrianKrebs| Date: Mon, 19 Mar 2018 03:53:12 +0000

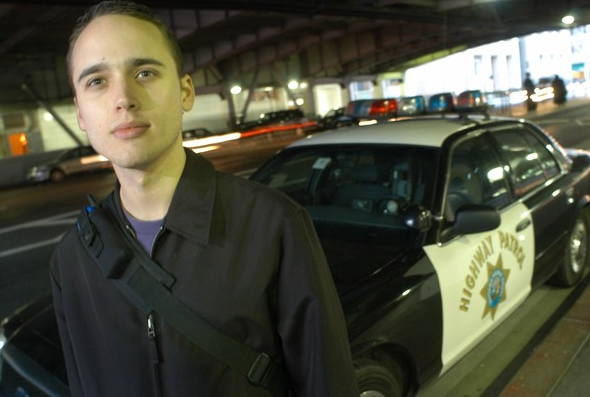
Adrian Lamo, the hacker probably best known for breaking into The New York Times’s network and for reporting Chelsea Manning’s theft of classified documents to the FBI, was found dead in a Kansas apartment on Wednesday. Lamo was widely reviled and criticized for turning in Manning, but that chapter of his life eclipsed the profile of a complex individual who taught me quite a bit about security over the years. Adrian Lamo, in 2006. Source: Wikipedia. I first met Lamo in 2001 when I was a correspondent for Newsbytes.com, a now-defunct tech publication that was owned by The Washington Post at the time. A mutual friend introduced us over AOL Instant Messenger, explaining that Lamo had worked out a simple method allowing him to waltz into the networks of some of the world’s largest media companies using nothing more than a Web browser.

Read More
IndependentSecuriteam

SSD Advisory – AppWeb Authentication Bypass (Digest, and Basic)

Credit to Author: SSD / Noam Rathaus| Date: Wed, 14 Mar 2018 19:01:53 +0000

Vulnerability Summary A critical vulnerability in the EmbedThis HTTP library, and Appweb versions 5.5.x, 6.x, and 7.x including the latest version present in the git repository. In detail, due to a logic flaw, with a forged HTTP request it is possible to bypass the authentication for HTTP basic and HTTP digest login types. Confirmed Vulnerable … Continue reading SSD Advisory – AppWeb Authentication Bypass (Digest, and Basic)

Read More
ComputerWorldIndependent

Microsoft lifts update embargo on Windows 10

Credit to Author: Gregg Keizer| Date: Fri, 16 Mar 2018 07:51:00 -0700

Microsoft this week lifted the security update blockade on Windows 10 PCs that do not have approved antivirus software, but kept the no-patches-for-you rule in place for the more popular Windows 7.

The update roadblock was assembled in early January, when Microsoft issued mitigations against the Spectre and Meltdown vulnerabilities. Those vulnerabilities stemmed from design flaws in virtually all modern processors made by Intel, AMD and ARM. According to Microsoft, the security updates could brick PCs equipped with antivirus (AV) software that had improperly tapped into kernel memory.

To read this article in full, please click here

Read More
IndependentKrebs

Who Is Afraid of More Spams and Scams?

Credit to Author: BrianKrebs| Date: Fri, 16 Mar 2018 13:55:45 +0000

Security researchers who rely on data included in Web site domain name records to combat spammers and scammers will likely lose access to that information for at least six months starting at the end of May 2018, under a new proposal that seeks to bring the system in line with new European privacy laws. The result, some experts warn, will likely mean more spams and scams landing in your inbox.

Read More
ComputerWorldIndependent

Massive March Patch Tuesday relaxes antivirus restrictions, but there are problems

Credit to Author: Woody Leonhard| Date: Wed, 14 Mar 2018 06:55:00 -0700

On a scale from 1 to 10, Microsoft in March has ratcheted the patching pace up to 11. The good news is that there are no known exploits for any of the “Critical” rated security holes. (Worth repeating: There are still no known exploits for Meltdown or Spectre.) The bad news? Reports of another forced upgrade to Win10 Fall Creators Update. Still waiting for confirmation on that one.

By the numbers

As usual, Martin Binkmann on ghacks.net, has the best summary:

To read this article in full, please click here

Read More
IndependentSecuriteam

SSD Advisory – AppWeb Authentication Bypass (Digest, Basic and Forms)

Credit to Author: SSD / Noam Rathaus| Date: Wed, 14 Mar 2018 19:01:53 +0000

Vulnerability Summary A critical vulnerability in the EmbedThis HTTP library, and Appweb versions 5.5.x, 6.x, and 7.x including the latest version present in the git repository. In detail, due to a logic flaw, with a forged HTTP request it is possible to bypass the authentication for form and digest login types. Confirmed Vulnerable Appweb version … Continue reading SSD Advisory – AppWeb Authentication Bypass (Digest, Basic and Forms)

Read More
IndependentSecuriteam

SSD Advisory – VK Messenger (VKontakte) vk:// URI Handler Commands Execution

Credit to Author: SSD / Noam Rathaus| Date: Sun, 11 Mar 2018 10:51:34 +0000

Vulnerability Summary The following describes a vulnerability in VK Messenger that is triggered via the exploitation of improperly handled URI. VK (VKontakte; [..], meaning InContact) is “an online social media and social networking service. It is available in several languages. VK allows users to message each other publicly or privately, to create groups, public pages … Continue reading SSD Advisory – VK Messenger (VKontakte) vk:// URI Handler Commands Execution

Read More
IndependentKrebs

Flash, Windows Users: It’s Time to Patch

Credit to Author: BrianKrebs| Date: Tue, 13 Mar 2018 19:36:28 +0000

Adobe and Microsoft each pushed critical security updates to their products today. Adobe’s got a new version of Flash Player available, and Microsoft released 14 updates covering more than 75 vulnerabilities, two of which were publicly disclosed prior to today’s patch release. The Microsoft updates affect all supported Windows operating systems, as well as all supported versions of Internet Explorer/Edge, Office, Sharepoint and Exchange Server. All of the critical vulnerabilities from Microsoft are in browsers and browser-related technologies, according to a post from security firm Qualys.

Read More