Credit to Author: BrianKrebs| Date: Tue, 20 Feb 2018 11:51:12 +0000
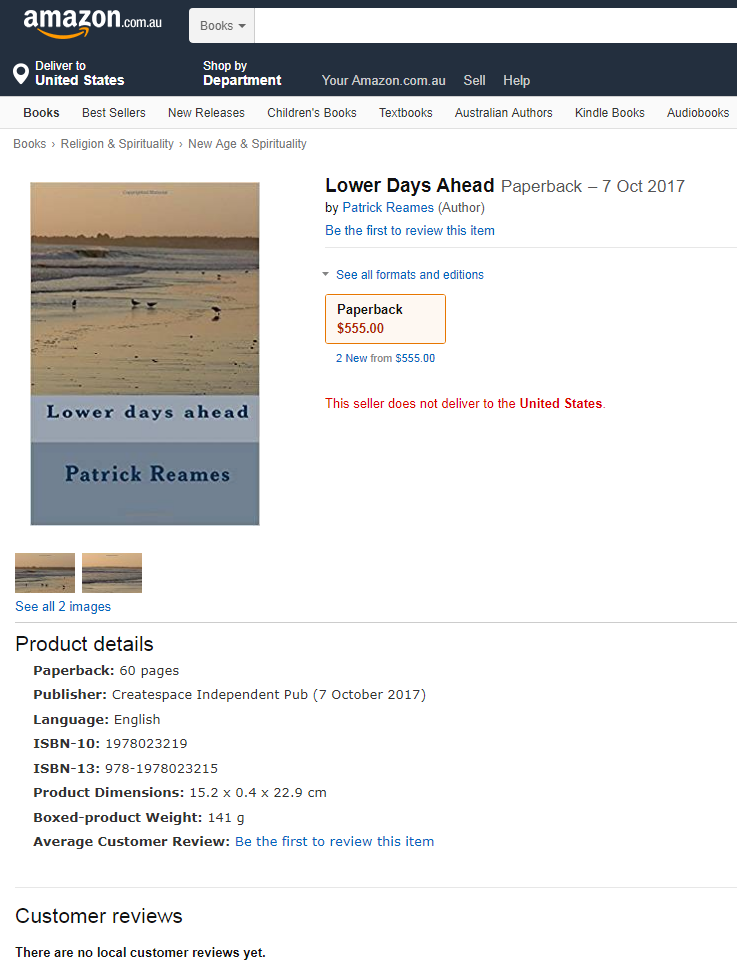
Patrick Reames had no idea why Amazon.com sent him a 1099 form saying he’d made almost $24,000 selling books via Createspace, the company’s on-demand publishing arm. That is, until he searched the site for his name and discovered someone has been using it to peddle a $555 book that’s full of nothing but gibberish.
Credit to Author: BrianKrebs| Date: Mon, 19 Feb 2018 14:44:49 +0000
Identity thieves who specialize in tax refund fraud have been busy of late hacking online accounts at multiple tax preparation firms, using them to file phony refund requests. Once the Internal Revenue Service processes the return and deposits money into bank accounts of the hacked firms’ clients, the crooks contact those clients posing as a collection agency and demand that the money be “returned.” In one version of the scam, criminals are pretending to be debt collection agency officials acting on behalf of the IRS. They’ll call taxpayers who’ve had fraudulent tax refunds deposited into their bank accounts, claim the refund was deposited in error, and threaten recipients with criminal charges if they fail to forward the money to the collection agency. This is exactly what happened to a number of customers at a half dozen banks in Oklahoma earlier this month. Elaine Dodd, executive vice president of the fraud division at the Oklahoma Bankers Association, said many financial institutions in the Oklahoma City area had “a good number of customers” who had large sums deposited into their bank accounts at the same time.
Robert Gibbons, CTO at Datta, joins host Steve Ragan to talk about why companies pay out ransoms, the role of incident response plans and continuity strategies, and how companies weigh the risks.
Credit to Author: Woody Leonhard| Date: Fri, 16 Feb 2018 09:12:00 -0800
The Microsoft Update Catalog uses insecure HTTP links – not HTTPS links – on the download buttons, so patches you download from the Update Catalog are subject to all of the security problems that dog HTTP links, including man-in-the-middle attacks.
Security researcher Stefan Kanthak, writing on Seclist’s Bugtraq mailing list, elaborates:
Even if you browse the “Microsoft Update Catalog” via the HTTPS link, ALL download links published there use HTTP, not HTTPS!
That’s trustworthy computing … the Microsoft way!
Despite numerous mails sent to <secure () microsoft com> in the last years, and numerous replies “we’ll forward this to the product groups,” nothing happens at all.
Credit to Author: Gregg Keizer| Date: Thu, 15 Feb 2018 12:11:00 -0800
Microsoft’s free Windows Analytics service now scans enterprise Windows 7, Windows 8.1 and Windows 10 PCs, and reports whether they’ve been updated to defend against potential attacks exploiting the Meltdown and Spectre processor vulnerabilities.
The new capabilities of Windows Analytics’ “Upgrade Readiness” were announced Tuesday by Terry Myerson, the top Windows executive at the company. Myerson called the vulnerabilities – found by Google security researchers and reported to vendors in mid-2017 – “a new challenge for all of us” because they were in the silicon, not in software.
“We have added new capabilities to our free Windows Analytics service to report the status for all the Windows devices that [IT professionals] manage,” Myerson wrote in a post to a company blog.
Credit to Author: BrianKrebs| Date: Thu, 15 Feb 2018 17:11:30 +0000
Companies around the globe are scrambling to comply with new European privacy regulations that take effect a little more than three months from now. But many security experts are worried that the changes being ushered in by the rush to adhere to the law may make it more difficult to track down cybercriminals and less likely that organizations will be willing to share data about new online threats. On May 25, 2018, the General Data Protection Regulation (GDPR) takes effect. The law, enacted by the European Parliament, requires technology companies to get affirmative consent for any information they collect on people within the European Union. Organizations that violate the GDPR could face fines of up to four percent of global annual revenues.
Credit to Author: SSD / Maor Schwartz| Date: Wed, 14 Feb 2018 08:58:11 +0000
Vulnerability Summary The following advisory describes an information disclosure found in the following TrendNet routers: TEW-751DR – v1.03B03 TEW-752DRU – v1.03B01 TEW733GR – v1.03B01 TRENDnet’s “N600 Dual Band Wireless Router, model TEW-751DR, offers proven concurrent Dual Band 300 Mbps Wireless N networking. Embedded GREENnet technology reduces power consumption by up to 50%. For your convenience … Continue reading SSD Advisory – TrendNet AUTHORIZED_GROUP Information Disclosure
Credit to Author: Woody Leonhard| Date: Wed, 14 Feb 2018 10:44:00 -0800
The very early reports are in, and it looks like this month’s monstrous panoply of patches isn’t as destructive as last month’s – so far, at least. Aside from a few reported incompatibilities, the big news involves two Outlook security holes that kick in when you download email, or preview a message. There are no known exploits, but if you use Outlook, you need to understand the dangers – and should seriously consider patching sooner rather than later.
First, the blast. Yesterday, Microsoft released its usual Patch Tuesday security updates, which include 50 separately identified security holes (CVEs). Those 50 are in addition to the one Adobe Flash Player security hole, CVE 4074595, that was plugged on Feb. 6. Of the 50, 14 are rated Critical, 34 rated Important (which means they aren’t) and two are Moderate.