Independent

ComputerWorldIndependent

It's time: Make sure Windows Auto Update is turned off
Credit to Author: Woody Leonhard| Date: Mon, 11 Dec 2017 03:44:00 -0800

It’s time to make sure your computer is locked down. If history is any indication, we’re going to be in for a rocky ride over the next week or two.

In September, folks who were set to update Windows automatically were greeted by Word docs and Excel spreadsheets that wouldn’t display merged cells, switched languages and intentionally broke one-click printing on custom forms. In October, admins who let patches go through automatically were greeted by oceans of blue screens and failures in Microsoft’s own Dynamics CRM. Last month, every version of Windows was hit with a patching bug that blocked Epson dot matrix printers — and those who had told Win10 Creators Update to wait to upgrade found themselves “accidentally” upgraded to Win10 Fall Creators Update, version 1709.
To read this article in full, please click here

Read More
ComputerWorldIndependent

Microsoft quietly repairs Windows Defender security hole CVE-2017-11937

Credit to Author: Woody Leonhard| Date: Fri, 08 Dec 2017 07:23:00 -0800

Many malware researchers were surprised to find an unexpected patch on their machines yesterday. It didn’t arrive through the front door — Windows Update wasn’t involved. Instead, the new version of mpengine.dll arrived automatically, around the back, even if you have Windows Update turned off.

This vulnerability is particularly nasty. If the Malware Protection Engine scans a jimmied file, the file can take over your computer and run whatever it wants. Since the MPE routinely runs all the time, in the background, that means a bad file could infect your computer in myriad ways. To quote Microsoft’s Security Vulnerability notice:

To read this article in full, please click here

Read More
ComputerWorldIndependent

Apple’s HomeKit security blunder exposes the risk of smart homes

Credit to Author: Jonny Evans| Date: Fri, 08 Dec 2017 06:42:00 -0800

The expression “safe as houses” will become a thing of the past if tech firms don’t get connected home security right, and the need to be incredibly watchful was visible in Apple’s latest security blunder this week.

Not so ideal home

The latest iOS 11.2 update held a zero-day vulnerability attackers could exploit to control smart home devices, including connected locks, 9to5Mac explains. While the vulnerability was difficult to exploit, and Apple has acted very swiftly to close this security gap, its existence exposes the risk of smart homes.

To read this article in full, please click here

Read More
IndependentKrebs

Phishers Are Upping Their Game. So Should You.

Credit to Author: BrianKrebs| Date: Fri, 08 Dec 2017 00:35:24 +0000

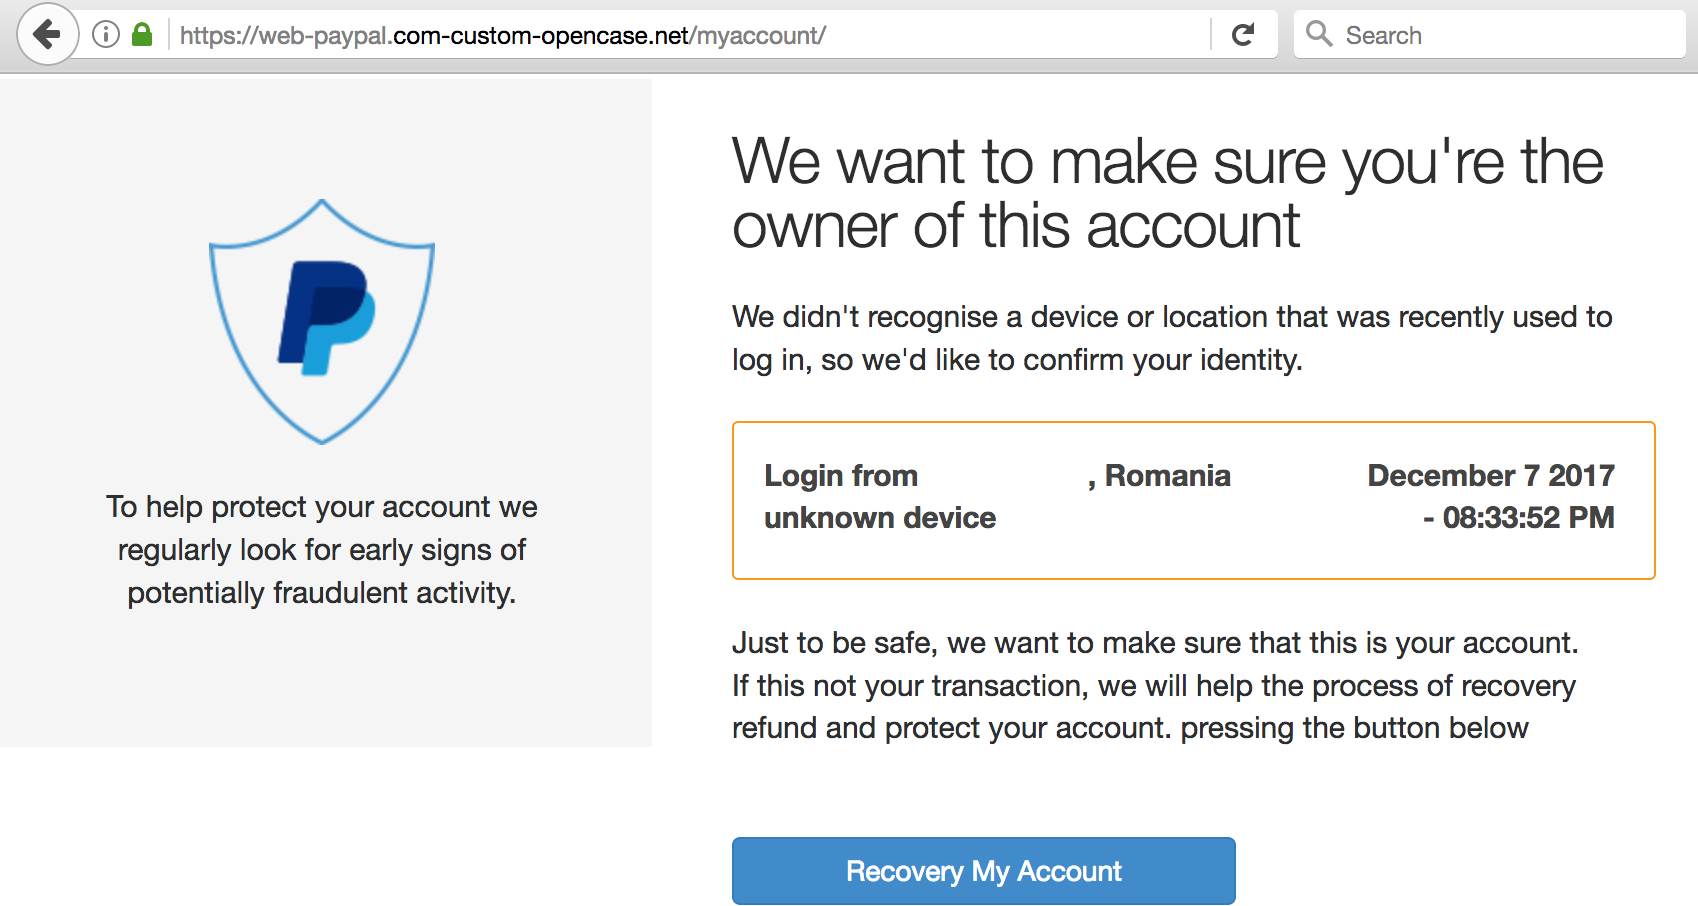
Not long ago, phishing attacks were fairly easy for the average Internet user to spot: Full of grammatical and spelling errors, and linking to phony bank or email logins at unencrypted (http:// vs. https://) Web pages. Increasingly, however, phishers are upping their game, polishing their copy and hosting scam pages over https:// connections — complete with the green lock icon in the browser address bar to make the fake sites appear more legitimate.

Read More
ComputerWorldIndependent

How blockchain will underpin the new trust economy

Credit to Author: Lucas Mearian| Date: Thu, 07 Dec 2017 03:20:00 -0800

Over the next two years, enterprises are expected to ramp up their efforts to test blockchain technology as part of a new method of establishing trust in a digital economy.

New research from consultancy Deloitte LLP shows a “trust economy” is now developing around person-to-person (P2P) transactions enabled by blockchain technology and not dependent on more traditional methods such as credit ratings or guaranteed cashier’s checks.

“Rather, it relies on each transacting party’s reputation and digital identity – the elements of which may soon be stored and managed in a blockchain,” Deloitte analysts said in a report.

To read this article in full, please click here

Read More
IndependentSecuriteam

SSD Advisory – Dasan Unauthenticated Remote Code Execution

Credit to Author: SSD / Maor Schwartz| Date: Wed, 06 Dec 2017 06:42:29 +0000

Vulnerability Summary The following advisory describes a buffer overflow that leads to remote code execution found in Dasan Networks GPON ONT WiFi Router H640X versions 12.02-01121 / 2.77p1-1124 / 3.03p2-1146 Dasan Networks GPON ONT WiFi Router “is indoor type ONT dedicated for FTTH (Fibre to the Home) or FTTP (Fiber to the Premises) deployments. That … Continue reading SSD Advisory – Dasan Unauthenticated Remote Code Execution

Read More
IndependentSecuriteam

SSD Advisory – Monstra CMS RCE

Credit to Author: SSD / Noam Rathaus| Date: Wed, 06 Dec 2017 06:35:44 +0000

Vulnerabilities Summary The following advisory describes a vulnerability found in Monstra CMS. Monstra is “a modern and lightweight Content Management System. It is Easy to install, upgrade and use.” The vulnerability found is a remote code execution vulnerability through an arbitrary file upload mechanism. Credit An independent security researcher, Ishaq Mohammed, has reported this vulnerability … Continue reading SSD Advisory – Monstra CMS RCE

Read More
IndependentKrebs

Anti-Skimmer Detector for Skimmer Scammers

Credit to Author: BrianKrebs| Date: Tue, 05 Dec 2017 20:37:22 +0000

Crooks who make and deploy ATM skimmers are constantly engaged in a cat-and-mouse game with financial institutions, which deploy a variety of technological measures designed to defeat skimming devices. The latest innovation aimed at tipping the scales in favor of skimmer thieves is a small, battery powered device that provides crooks a digital readout indicating whether an ATM likely includes digital anti-skimming technology.

Read More