Independent

IndependentKrebs

Gas Pump Skimmer Sends Card Data Via Text
Credit to Author: BrianKrebs| Date: Thu, 27 Jul 2017 11:08:59 +0000

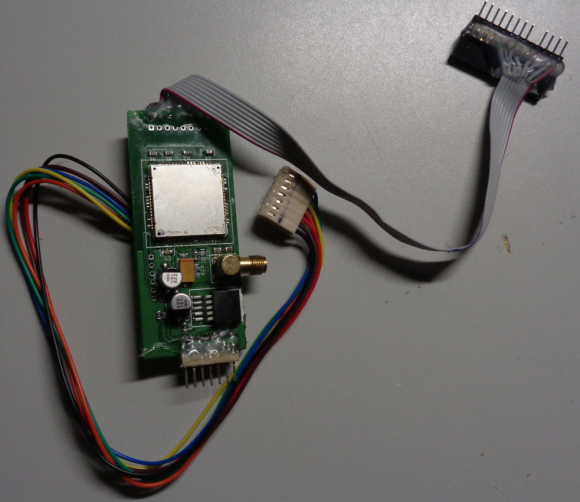
Skimming devices that crooks install inside fuel station gas pumps frequently rely on an embedded Bluetooth component allowing thieves to collect stolen credit card data from the pumps wirelessly with any mobile device. The downside of this approach is that Bluetooth-based skimmers can be detected by anyone else with a mobile device. Now, investigators in the New York say they are starting to see pump skimmers that use cannibalized cell phone components to send stolen card data via text message.

Read More
IndependentSecuriteam

SSD Advisory – Supervisor Authenticated Remote Code Execution

Credit to Author: SSD / Maor Schwartz| Date: Wed, 26 Jul 2017 10:45:54 +0000

Vulnerability Summary The following advisory describes an authenticated remote code execution vulnerability in Supervisor version 3.1.2 and Supervisor version 3.3.2. Supervisor is a client/server system that allows its users to monitor and control a number of processes on UNIX-like operating systems – used to control processes related to a project or a customer, and is … Continue reading SSD Advisory – Supervisor Authenticated Remote Code Execution

Read More
ComputerWorldIndependent

Tiptoe through the bugs and get Windows and Office updated

Credit to Author: Woody Leonhard| Date: Wed, 26 Jul 2017 09:55:00 -0700

The fourth Tuesday of the month has come and gone, and it now looks reasonably safe to patch Windows and Office. I was expecting two big releases yesterday — one to fix numerous bugs in Win10 Creators Update, version 1703; the other to plug the bugs introduced by June’s Office security patches — but neither trove appeared. Given Microsoft’s past patterns, it’s unlikely that we’ll see any more serious patches until next month’s Patch Tuesday, on Aug. 8.

There’s also a bit of additional impetus right now. On July 17, security researcher Haifei published a proof of concept for running malware scripts directly in Office apps. I haven’t seen any exploits in the wild as yet, but it would be a good idea to install KB 3213640 (Office 2007), KB 3213624 (Office 2010), KB 3213555 (Office 2013) and/or KB 3213545 (Office 2016) in the short term. (Thx to @LeaningTowardsLinux.) Note that none of these patches, as best as I can tell, correct the Office bugs introduced in June.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Wasn't this supposed to speed things up?

Credit to Author: Sharky| Date: Wed, 26 Jul 2017 03:00:00 -0700

IT pilot fish is moving on with his career, but before he changes employers, he comes up with an easier way for users to get on the company intranet.

“I wanted to relieve the staff of the need to memorize yet another username/password combination — or write it on a sticky note to be posted on the wall,” says fish.

“So I set up an interface that used Windows Active Directory for access authorization, with appropriate fallback in case the domain controller couldn’t be accessed. The whole thing worked like a dream.”

Fast forward a couple years: Fish is brought back in to add more capabilities to the Intranet that’s been faithfully chugging along since he left. But as fish starts on the new project, the IT director casually mentions that intranet logins have been running a lot slower. Could fish perhaps check into that too?

To read this article in full or to leave a comment, please click here

Read More
IndependentKrebs

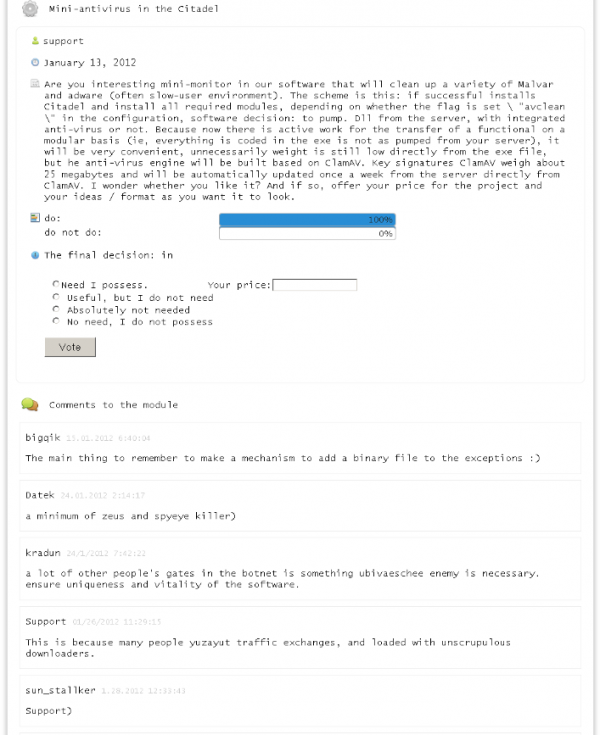
How a Citadel Trojan Developer Got Busted

Credit to Author: BrianKrebs| Date: Tue, 25 Jul 2017 16:11:38 +0000

A U.S. District Court judge in Atlanta last week handed a five year prison sentence to Mark Vartanyan, a Russian hacker who helped develop and sell the once infamous and widespread Citadel banking trojan. This fact has been reported by countless media outlets, but far less well known is the fascinating backstory about how Vartanyan got caught.

Read More
ComputerWorldIndependent

The big secret behind Google Play Protect on Android

Credit to Author: JR Raphael| Date: Tue, 25 Jul 2017 09:04:00 -0700

Have you heard the news? Your Android device is in the midst of being updated to include Google’s comprehensive new security suite, Google Play Protect.

Play Protect, as you may recall, was one of the biggest bullet points to come out of this year’s Google I/O keynote address. It’s a “doubled-down” effort around Android security, as Google explains it, and it’s designed to ensure every Android device is always protected from any form of harm.

To read this article in full or to leave a comment, please click here

Read More