Independent

IndependentKrebs

B&B Theatres Hit in 2-Year Credit Card Breach
Credit to Author: BrianKrebs| Date: Fri, 07 Jul 2017 15:26:07 +0000

B&B Theatres, a company that owns and operates the 7th-largest theater chain in America, says it is investigating a breach of its credit card systems. The acknowledgment comes just days after KrebsOnSecurity reached out to the company for comment on reports from financial industry sources who said they suspected the cinema chain has been leaking customer credit card data to cyber thieves for the past two years.

Read More
IndependentSecuriteam

SSD Advisory – Skype For Business XSS

Credit to Author: SSD / Maor Schwartz| Date: Thu, 06 Jul 2017 05:45:53 +0000

Vulnerability Summary The following advisory describes an XSS vulnerability found in Skype for Business. Credit An independent security researcher has reported this vulnerability to Beyond Security’s SecuriTeam Secure Disclosure program. Vendor response The vendor has released patches to address this vulnerability and has only provided these details in response to our query on the status: … Continue reading SSD Advisory – Skype For Business XSS

Read More
ComputerWorldIndependent

Microsoft releases 15 Office patches for July, but some June bugs still stink

Credit to Author: Woody Leonhard| Date: Thu, 06 Jul 2017 07:23:00 -0700

On Patch Wednesday of this week, Microsoft said it released 14 non-security Office updates, covering such fascinating topics as improved Dutch translations in Word 2013, Danish translations in Access, and Finnish and Swedish translations in Excel. Typical first Tuesday stuff.

Microsoft neglected to mention that it also shipped a fix for the bugs introduced by last month’s patches to Outlook 2010. Dubbed KB 4011042, the neglected fix appears to be a non-security patch that fixes bugs created by a security patch — a red flag for many advanced patchers.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

The ancient Microsoft networking protocol at the core of the latest global malware attack

Credit to Author: Preston Gralla| Date: Thu, 06 Jul 2017 03:20:00 -0700

Another day, another global malware attack made possible by a Microsoft security hole. Once again, attackers used hacking tools developed by the U.S. National Security Agency (NSA), which were stolen and subsequently released by a group called Shadow Brokers.

This time around, though, the late-June attack apparently wasn’t ransomware with which the attackers hoped to make a killing. Instead, as The New York Times noted, it was likely an attack by Russia on Ukraine on the eve of a holiday celebrating the Ukrainian constitution, which was written after Ukraine broke away from Russia. According to the Times, the attack froze “computers in Ukrainian hospitals, supermarkets, and even the systems for radiation monitoring at the old Chernobyl nuclear plant.” After that, it spread worldwide. The rest of the world was nothing more than collateral damage.

To read this article in full or to leave a comment, please click here

Read More
IndependentKrebs

Who is the GovRAT Author and Mirai Botmaster ‘Bestbuy’?

Credit to Author: BrianKrebs| Date: Wed, 05 Jul 2017 11:25:14 +0000

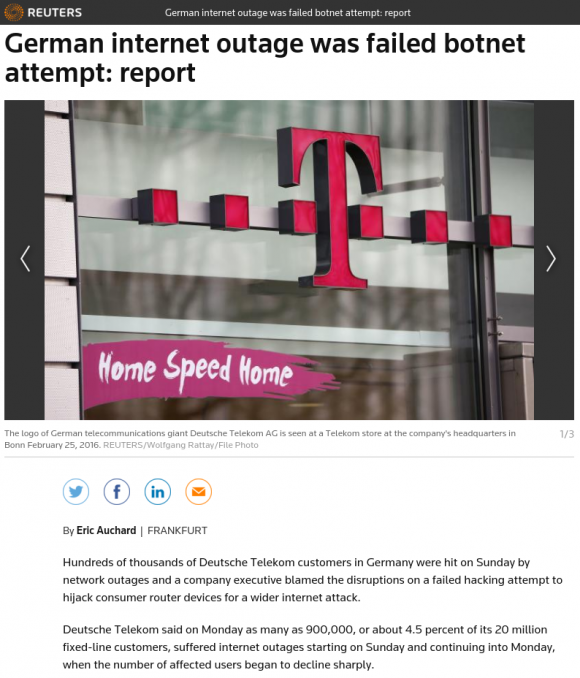
In February 2017, authorities in the United Kingdom arrested a 29-year-old U.K. man on suspicion of knocking more than 900,000 Germans offline in an attack tied to Mirai, a malware strain that enslaves Internet of Things (IoT) devices like security cameras and Internet routers for use in large-scale cyberattacks. Investigators haven’t yet released the man’s name, but news reports suggest he may be better known by the hacker handle “Bestbuy.” This post will follow a trail of clues back to one likely real-life identity of Bestbuy.

Read More
IndependentSecuriteam

SSD Advisory – EMC IsilonSD Edge Command Injection

Credit to Author: SSD / Maor Schwartz| Date: Sun, 02 Jul 2017 08:09:16 +0000

Vulnerability Summary The following advisory describes a Remote Command Injection vulnerability found in EMC IsilonSD Edge version 1.0.1.0005. IsilonSD Edge enables you to deploy industry leading scale-out NAS operating system using industry-standard hardware. Key benefits of IsilonSD Edge: Simple yet powerful and efficient scale-out storage solution for remote and branch offices, Easily extends your enterprise … Continue reading SSD Advisory – EMC IsilonSD Edge Command Injection

Read More
IndependentKrebs

Is it Time to Can the CAN-SPAM Act?

Credit to Author: BrianKrebs| Date: Sun, 02 Jul 2017 16:14:42 +0000

Regulators at the U.S. Federal Trade Commission (FTC) are asking for public comment on the effectiveness of the CAN-SPAM Act, a 14-year-old federal law that seeks to crack down on unsolicited commercial email. Judging from an unscientific survey by this author, the FTC is bound to get an earful.

Read More
IndependentSecuriteam

SSD Advisory – Odoo CRM Code Execution

Credit to Author: SSD / Maor Schwartz| Date: Fri, 30 Jun 2017 18:50:42 +0000

Vulnerability Summary The following advisory describe arbitrary Python code execution found in Odoo CRM version 10.0 Odoo is a suite of open source business apps that cover all your company needs: CRM, eCommerce, accounting, inventory, point of sale, project management, etc. Odoo’s unique value proposition is to be at the same time very easy to … Continue reading SSD Advisory – Odoo CRM Code Execution

Read More