Independent

IndependentKrebs

SSA.GOV To Require Stronger Authentication

Credit to Author: BrianKrebs| Date: Wed, 10 May 2017 13:01:13 +0000

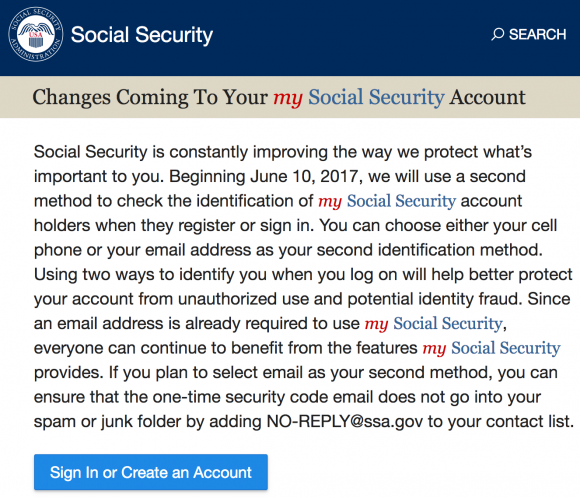
The U.S. Social Security Administration will soon require Americans to use stronger authentication when accessing their accounts at ssa.gov. As part of the change, SSA will require all users to enter a username and password in addition to a one-time security code sent their email or phone. In this post, we’ll parse this a bit more and look at some additional security options for SSA users.

Read More
ComputerWorldIndependent

With security awareness, money talks

Credit to Author: Evan Schuman| Date: Wed, 10 May 2017 04:00:00 -0700

According to a recent report, academics have been analyzing brainwaves of computer users to improve how they are alerted to cybersecurity dangers. I’m sorry, but getting users to pay stricter attention to security isn’t brain surgery: It’s all about money and job security. Come to think of it, job security itself is all about money, which makes money the only carrot and the only stick that IT needs.

That report, courtesy of Bloomberg BNA, said, “Many computer users automatically swat away repetitive dialogue box warnings of impending doom, especially when they are engaged in another activity. Now, engineers are using data analytics based on user tracking to discover what might help users pay attention to warnings. Software engineers are exploring promising techniques, such as changing background colors in warning notifications and switching formats to distinguish substantial security warnings from mundane messages. Tapping people’s brains helps the engineers design more effective user interfaces.”

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Microsoft fixes 55 flaws, 3 of them exploited by Russian cyberspies

Credit to Author: Lucian Constantin| Date: Tue, 09 May 2017 14:39:00 -0700

Microsoft released security patches Tuesday for 55 vulnerabilities across the company’s products, including for three flaws that are already exploited in targeted attacks by cyberespionage groups.

Fifteen of the vulnerabilities fixed in Microsoft’s patch bundle for May are rated as critical and they affect Windows, Microsoft Office, Microsoft Edge, Internet Explorer, and the malware protection engine used in most of the company’s anti-malware products.

System administrators should prioritize the Microsoft Office patches because they address two vulnerabilities that attackers have exploited in targeted attacks over the past two months. Both of these flaws, CVE-2017-0261 and CVE-2017-0262, stem from how Microsoft Office handles Encapsulated PostScript (EPS) image files and can lead to remote code execution on the underlying system.

To read this article in full or to leave a comment, please click here

Read More
IndependentKrebs

Emergency Fix for Windows Anti-Malware Flaw Leads May’s Patch Tuesday

Credit to Author: BrianKrebs| Date: Tue, 09 May 2017 18:14:25 +0000

Adobe and Microsoft both issued updates today to fix critical security vulnerabilities in their software. Microsoft actually issued an emergency update on Monday just hours ahead of today’s regularly scheduled “Patch Tuesday” (the 2nd Tuesday of each month) to fix a dangerous flaw present in most of Microsoft’s anti-malware technology that’s being called the worst Windows bug in recent memory. Separately, Adobe has a new version of its Flash Player software available that squashes at least seven nasty bugs. Last week, Google security researcher Tavis Ormandy reported to Microsoft a flaw in its Malware Protection Engine, a technology that exists in most of Redmond’s malware protection offerings — including Microsoft Forefront, Microsoft Security Essentials and Windows Defender. Rather than worry about their malicious software making it past Microsoft’s anti-malware technology, attackers could simply exploit this flaw to run their malware automatically once their suspicious file is scanned.

Read More
ComputerWorldIndependent

Microsoft fixes remote hacking flaw in Windows Malware Protection Engine

Credit to Author: Lucian Constantin| Date: Tue, 09 May 2017 11:32:00 -0700

Microsoft released an update for the malware scanning engine bundled with most of its Windows security products in order to fix a highly critical vulnerability that could allow attackers to hack computers.

The vulnerability was discovered by Google Project Zero researchers Tavis Ormandy and Natalie Silvanovich on Saturday and was serious enough for Microsoft to create and release a patch by Monday. This was an unusually fast response for the company, which typically releases security updates on the second Tuesday of every month and rarely breaks out of that cycle.

Ormandy announced Saturday on Twitter that he and his colleague found a “crazy bad” vulnerability in Windows and described it as “the worst Windows remote code execution in recent memory.”

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Industrial robots are security weak link

Credit to Author: Sharon Gaudin| Date: Tue, 09 May 2017 03:00:00 -0700

Industrial robots used in factories and warehouses that are connected to the internet are not secure, leaving companies open to cyberattacks and costly damages.

That’s the word coming from a study conducted by global security software company Trend Micro and Polytechnic University of Milan, the largest technical university in Italy.

“The industrial robot – it’s not ready for the world it’s living in,” said Mark Nunnikhoven, vice president of cloud research at Trend Micro. “The reality is these things are being connected in more and more places. There are a lot of attacks that could happen in that environment.”

The study looked at Internet security vulnerabilities that could involve industrial robots used on manufacturing lines in areas such as the automobile and aerospace industries. The robots, which generally look like large mechanical arms, are used to move heavy objects, weld seams and fit pieces together. The machines also can be found moving and stacking crates in warehouses.

To read this article in full or to leave a comment, please click here
Read More
IndependentKrebs

Website Flaw Let True Health Diagnostics Users View All Medical Records

Credit to Author: BrianKrebs| Date: Tue, 09 May 2017 03:13:04 +0000

Over the past two weeks readers have pointed KrebsOnSecurity to no fewer than three different healthcare providers that failed to provide the most basic care to protect their patients’ records online. Only one of the three companies — the subject of today’s story — required users to be logged in order to view all patient records. A week ago I heard from Troy Mursch, an IT consultant based in Las Vegas. A big fan of proactive medical testing, Mursch said he’s been getting his various lab results reviewed annually for the past two years with the help of a company based in Frisco, Texas called True Health Diagnostics.

Read More
ComputerWorldIndependent

Local cost of a Big Mac decides ransom amount for Fatboy ransomware

Credit to Author: Darlene Storm| Date: Mon, 08 May 2017 09:33:00 -0700

Location, location, location … you’ve heard it many times before but not when it comes to a ransomware deciding a ransom amount. Fatboy, a ransomware-as-a-service, is believed to be the first ransomware that automatically adjusts the ransom amount based on a victim’s location.

Just when you think you’ve heard every conceivable ransomware demand – not just ransoms paid in bitcoins or other cryptocurrencies like Monero, or paid in iTunes or Amazon gift cards, ransomware which costs nothing for decryption as long as you infect two other people, or even ransomware that demands a high score on a shooter game before decrypting drives – now there’s a ransomware that charges victims based on the Big Mac Index.

To read this article in full or to leave a comment, please click here

Read More