Independent

ComputerWorldIndependent

Unpatched vulnerability puts Ubiquiti networking products at risk

Credit to Author: Lucian Constantin| Date: Thu, 16 Mar 2017 13:34:00 -0700

An unpatched command injection vulnerability could allow hackers to take over enterprise networking products from Ubiquiti Networks.

The vulnerability was discovered by researchers from SEC Consult and allows authenticated users to inject arbitrary commands into the web-based administration interface of affected devices. These commands would be executed on the underlying operating system as root, the highest privileged account.

Because it requires authentication, the vulnerability’s impact is somewhat reduced, but it can still be exploited remotely through cross-site request forgery (CSRF). This is an attack technique that involves forcing a user’s browser to send unauthorized requests to specifically crafted URLs in the background when they visit attacker-controlled websites.

To read this article in full or to leave a comment, please click here
Read More
ComputerWorldIndependent

Cobol plays major role in U.S. government breaches

Credit to Author: Patrick Thibodeau| Date: Thu, 16 Mar 2017 13:21:00 -0700

New research is turning on its head the idea that legacy systems — such as Cobol and Fortran — are more secure because hackers are unfamiliar with the technology.

New research found that these outdated systems, which may not be encrypted or even documented, were more susceptible to threats.

By analyzing publicly available federal spending and security breach data, the researchers found that a 1% increase in the share of new IT development spending is associated with a 5% decrease in security breaches.

“In other words, federal agencies that spend more in maintenance of legacy systems experience more frequent security incidents, a result that contradicts a widespread notion that legacy systems are more secure,” the paper found. The research paper was written by Min-Seok Pang, an assistant professor of management information systems at Temple University, and Huseyin Tanriverdi, an associate professor in the Information, Risk and Operations Department at the University of Texas at Austin.

To read this article in full or to leave a comment, please click here
Read More
ComputerWorldIndependent

Adobe Reader, Edge, Safari and Ubuntu fall in first day at Pwn2Own

Credit to Author: Lucian Constantin| Date: Thu, 16 Mar 2017 10:37:00 -0700

Bug hunters have gathered again to test their skills against some of the most popular and mature software programs during the Pwn2Own hacking contest. During the first day, they successfully demonstrated exploits against Microsoft Edge, Apple’s Safari, Adobe Reader and Ubuntu Desktop.

The Pwn2Own contest runs every year during the CanSecWest security conference in Vancouver, British Columbia. It’s organized and sponsored by the Zero Day Initiative (ZDI), an exploit acquisition program operated by Trend Micro after its acquisition of TippingPoint.

This year the contest has a prize pool of $1 million for exploits in five categories: virtual machines (VMware Workstation and Microsoft Hyper-V); web browser and plugins (Microsoft Edge, Google Chrome, Mozilla Firefox, Apple Safari and Flash Player running in Edge); local escalation of privilege (Microsoft Windows, macOS and Ubuntu Desktop); enterprise applications (Adobe Reader, Word, Excel and PowerPoint) and server side (Apache Web Server on Ubuntu Server).

To read this article in full or to leave a comment, please click here
Read More
ComputerWorldIndependent

U.S. faces limits in busting Russian agents over Yahoo breach

Credit to Author: Michael Kan| Date: Thu, 16 Mar 2017 03:52:00 -0700

In a rare move, the U.S. has indicted two Russian government agents for their suspected involvement in a massive Yahoo data breach. But what now?

Security experts say Wednesday’s indictment might amount to nothing more than naming and shaming Russia. That’s because no one expects the Kremlin to play along with the U.S. indictment.

“I can’t imagine the Russian government is going to hand over the two FSB officers,” said Jeremiah Grossman, chief of security strategy at SentinelOne.

“Even in the most successful investigations, state hackers are still immune from prosecution or retaliation,” said Kenneth Geers, a research scientist at security firm Comodo.

To read this article in full or to leave a comment, please click here
Read More
IndependentKrebs

Four Men Charged With Hacking 500M Yahoo Accounts

Credit to Author: BrianKrebs| Date: Thu, 16 Mar 2017 00:49:07 +0000

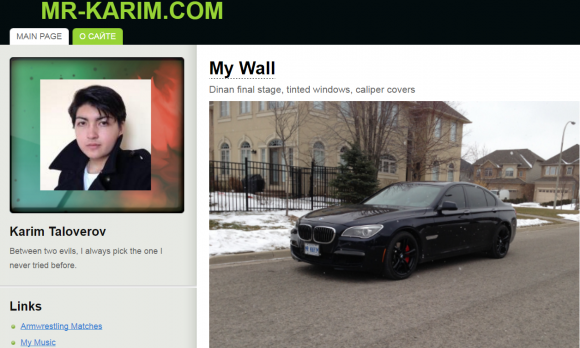
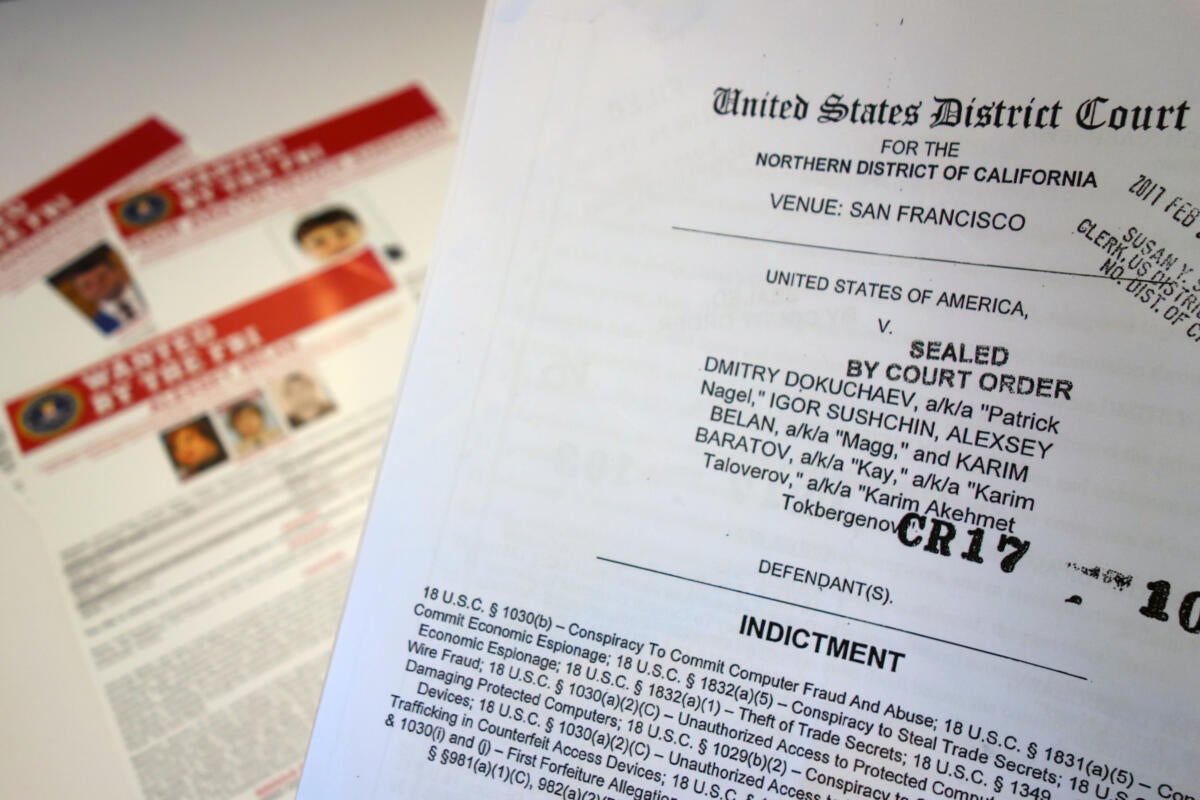
The U.S. Justice Department today unsealed indictments against four men accused of hacking into a half-billion Yahoo email accounts. Two of the men named in the indictments worked for a unit of the Russian Federal Security Service (FSB) that serves as the FBI’s point of contact in Moscow on cybercrime cases. Here’s a look at the accused, starting with a 22-year-old who apparently did not try to hide his tracks. According to a press release put out by the Justice Department, among those indicted was Karim Baratov (a.k.a. Kay, Karim Taloverov), a Canadian and Kazakh national who lives in Canada. Baratov is accused of being hired by the two FSB officer defendants in this case — Dmitry Dokuchaev, 33, and Igor Sushchin, 43 — to hack into the email accounts of thousands of individuals. According to a press release put out by the Justice Department, among those indicted was Karim Baratov (a.k.a. Kay, Karim Taloverov), a Canadian and Kazakh national who lives in Canada. Baratov is accused of being hired by the two FSB officer defendants in this case — Dmitry Dokuchaev, 33, and Igor Sushchin, 43 — to hack into the email accounts of thousands of individuals.

Read More
ComputerWorldIndependent

Inside the Russian Yahoo hack: How they did it

Credit to Author: Martyn Williams| Date: Wed, 15 Mar 2017 15:37:00 -0700

One mistaken click. That’s all it took for hackers aligned with the Russian state security service to gain access to Yahoo’s network and potentially the email messages and private information of as many as 500 million people.

The U.S. Federal Bureau of Investigation has been investigating the intrusion for two years, but it was only in late 2016 that the full scale of the hack became apparent. On Wednesday, the FBI indicted four people for the attack, two of whom are Russian spies.

Here’s how the FBI says they did it:

To read this article in full or to leave a comment, please click here
Read More
ComputerWorldIndependent

Defensive Computing for email attachments

Credit to Author: Michael Horowitz| Date: Wed, 15 Mar 2017 12:12:00 -0700

Email attachments remain an effective way to infect/compromise computers because people trust them too much. Blindly opening them is easy, simple and quick, but, it’s also not secure. What is secure?

Never open email attachments using Microsoft Office or Adobe’s PDF reading software.

Really should go without saying at this point.

Never open attachments on a Windows, Mac or Linux computer you care about or use regularly.

These old desktop systems are simply not as secure as more modern operating systems.

The safest computers for opening suspect files run iOS or Chrome OS.

To read this article in full or to leave a comment, please click here

Read More