Independent

IndependentKrebs

Payments Giant Verifone Investigating Breach
Credit to Author: BrianKrebs| Date: Tue, 07 Mar 2017 18:02:30 +0000

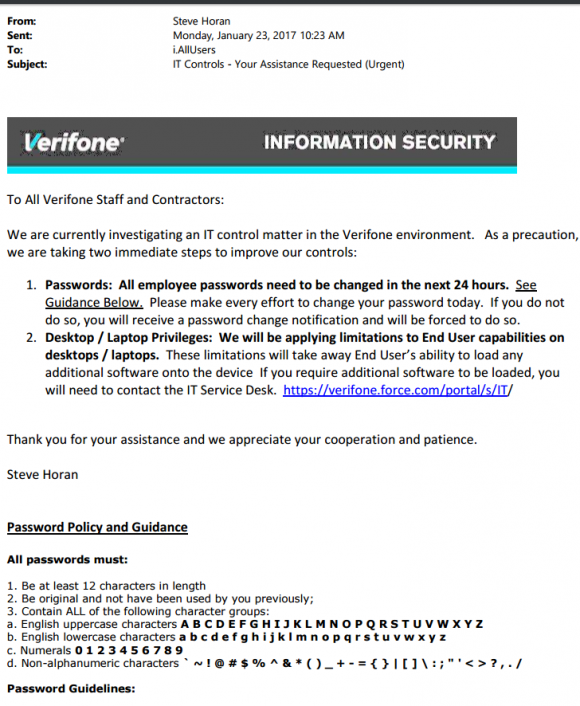
Credit and debit card payments giant Verifone [NYSE: PAY] is investigating a breach of its corporate computer networks that could impact companies running its point-of-sale solutions, according to multiple sources. Verifone says the extent of the breach was “limited” and that its payment services network was not impacted. San Jose, Calif.-based Verifone is the largest maker of credit card terminals used in the United States. It sells point-of-sale terminals and services to support the swiping and processing of credit and debit card payments at a variety of businesses, including retailers, taxis, and fuel stations. On Jan. 23, 2017, Verifone sent an “urgent” email to all company staff and contractors, telling them that they had 24 hours to change all company passwords.

Read More
ComputerWorldIndependent

Android gets patches for critical OpenSSL, media server and kernel driver flaws

Credit to Author: Lucian Constantin| Date: Tue, 07 Mar 2017 08:37:00 -0800

A five-month-old flaw in Android’s SSL cryptographic libraries is among the 35 critical vulnerabilities Google fixed in its March security patches for the mobile OS.

The first set of patches, known as patch level 2017-03-01, is common to all patched phones and contains fixes for 36 vulnerabilities, 11 of which are rated critical and 15 high. Android vulnerabilities rated critical are those that can be exploited to execute malicious code in the context of a privileged process or the kernel, potentially leading to a full device compromise.

One of the patched vulnerabilities is located in the OpenSSL cryptographic library and also affects Google’s newer BoringSSL library, which is based on OpenSSL. What’s interesting is that the flaw, identified as CVE-2016-2182, was patched in OpenSSL back in September. It can be exploited by forcing the library to process an overly large certificate or certificate revocation list from an untrusted source.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

WikiLeaks' CIA document dump shows agency can compromise Android, TVs

Credit to Author: Grant Gross| Date: Tue, 07 Mar 2017 08:22:00 -0800

WikiLeaks has released more than 8,700 documents it says come from the CIA’s Center for Cyber Intelligence, with some of the leaks saying the agency had 24 “weaponized” and previously undisclosed exploits for the Android operating system as of 2016.

Some of the Android exploits were developed by the CIA, while others came from the U.S. National Security Agency, U.K. intelligence agency GCHQ, and cyber arms dealers, according to the trove of documents released Tuesday. 

Some smartphone attacks developed by the CIA allow the agency to bypass the encryption in WhatsApp, Confide, and other apps by collecting audio and message traffic before encryption is applied, according to the WikiLeaks analysis.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

CA to acquire security testing firm Veracode for $614M

Credit to Author: John Ribeiro| Date: Tue, 07 Mar 2017 03:58:00 -0800

CA Technologies is acquiring application security testing company Veracode for $614 million in cash, in a bid to broaden its development and testing offering for enterprises and app developers.

The acquisition is expected to be completed by the second quarter of this year.

Privately held Veracode has offices in Burlington, Mass. and London, and employs over 500 people worldwide. The company has around 1,400 small and large customers.

Offering a software-as-a-service platform, Veracode is focused on technologies that let developers improve the security of applications from inception through production.

“Embedding security into the software development lifecycle and making it an automated part of the continuous delivery process means that developers can write code without the hassles of a manual and fragmented approach to security,” CA president and chief product officer Ayman Sayed wrote in a blog post.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Consumers are wary of smart homes that know too much

Credit to Author: Stephen Lawson| Date: Mon, 06 Mar 2017 18:10:00 -0800

Nearly two-thirds of consumers are worried about home IoT devices listening in on their conversations, according to a Gartner survey released Monday.

Those jitters aren’t too surprising after recent news items about TV announcers inadvertently activating viewers’ Amazon Echos, or about data from digital assistants being used as evidence in criminal trials. But privacy concerns are just one hurdle smart homes still have to overcome, according to the survey.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

A hard learned lesson in VPNs and secure websites

Credit to Author: Michael Horowitz| Date: Mon, 06 Mar 2017 17:00:00 -0800

Being a Defensive Computing kind of guy, I am a frequent flyer when it comes to VPN usage. But VPNs have both an upside and a downside.

Previously, I wrote about an unexpected downside that I ran into while making a purchase while logged into a VPN server in another country. I won’t be doing that again.

This time, a VPN interfered with a charitable donation.

I am a big fan of Libre Office. Yesterday, I tried to make a donation to the organization behind it, The Document Foundation, but my credit card was denied with a “transaction failed” error message.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Consumer Reports to grade tech products on security, privacy

Credit to Author: Michael Kan| Date: Mon, 06 Mar 2017 14:01:00 -0800

Consumer Reports, a major source for gadget and appliance reviews in the U.S., plans to start rating products on data security and privacy.

On Monday, the nonprofit publication unveiled a set of new testing standards it hopes will push the tech industry to create safer products.

“The goal is to help consumers understand which digital products do the most to protect their privacy and security, and give them the most control over their personal data,” the publication said.

Already, cybersecurity  experts are finding new tech products, whether they are cars or smart teddy bears, that are often poorly secured and easy to hack.  

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

U.S. drops child porn case to avoid disclosing Tor exploit

Credit to Author: Lucian Constantin| Date: Mon, 06 Mar 2017 07:04:00 -0800

The U.S. Department of Justice is asking a federal court to dismiss its indictment in a case that involves a child porn site known as Playpen, after a judge asked the government to disclose the hacking technique it used to gather evidence.

“The government must now choose between disclosure of classified information and dismissal of its indictment,” the DOJ said in a court filing Friday. “Disclosure is not currently an option.”

The case involves Jay Michaud, a school administrator from Vancouver, Wash., who was arrested in July 2015 for allegedly viewing child porn images on Playpen. Michaud’s case was one of at least 137 cases brought throughout the U.S. in relation to Playpen, a website that operated on the Tor anonymity network and which the FBI managed to seize in 2015.

To read this article in full or to leave a comment, please click here

Read More