Independent

ComputerWorldIndependent

Now THAT'S secure!

Credit to Author: Sharky| Date: Mon, 27 Feb 2017 03:00:00 -0800

When it comes to website security questions, this pilot fish has a bad attitude — and that’s “bad” spelled P-R-A-C-T-I-C-A-L.

“When they let me write my own questions, I write stuff like ‘Top line of the Spanish text on the control box of the computer speakers,'” says fish.

“It’s easy enough for me to find that answer — just look down and read it — but unless you’re in my house or know exactly what speakers I bought five years ago, you aren’t gonna get it.

“Otherwise, I usually type in nonsense, because I don’t forget my passwords.

“Then sometimes the company has a security breach, locks every affected account and says, ‘You’ll need to reset your password using your security questions.’

To read this article in full or to leave a comment, please click here
Read More
IndependentKrebs

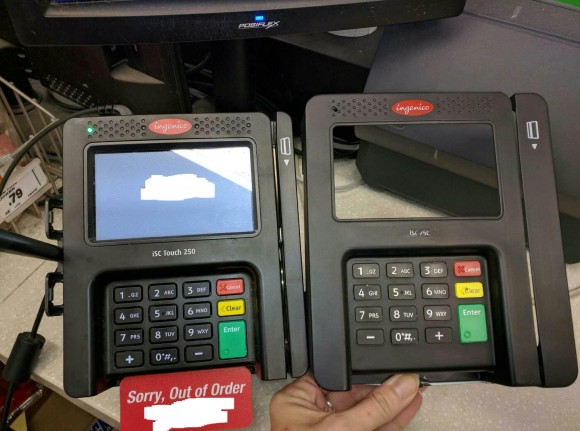
More on Bluetooth Ingenico Overlay Skimmers

Credit to Author: BrianKrebs| Date: Mon, 27 Feb 2017 01:54:58 +0000

This blog has featured several stories about “overlay” card and PIN skimmers made to be placed atop Ingenico-brand card readers at store checkout lanes. I’m revisiting the topic again because a security technician at a U.S.-based retailer recently shared a few photos of several of these devices pulled from compromised card terminals, and the images and his story offer a fair bit more detail than in previous articles on Ingenico overlay skimmers.

Read More
ComputerWorldIndependent

Samsung mulls iris scanners on smartphones to log into Windows PCs

Credit to Author: Agam Shah| Date: Sun, 26 Feb 2017 16:51:00 -0800

Soon, your Samsung phone may be able to recognize your iris and log you into your Windows PC.

Iris-scanning via phone is not yet a feature available for Samsung’s latest Galaxy Book 2-in-1s, which were announced at Mobile World Congress. But the company wants to quickly bridge the gap between its Galaxy smartphones, which run on Android, and its Windows PCs and 2-in-1s.

Software called Samsung Flow links the company’s Android smartphones to Windows PCs. Samsung and Microsoft are looking to collaborate on logins via Windows Hello — designed to use biometric authentication to log into PCs — and one big Flow feature is the ability to use Galaxy smartphones to wirelessly log in to the new Galaxy Book.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

IDG Contributor Network: 94% of Microsoft vulnerabilities can be easily mitigated

Credit to Author: Andy Patrizio| Date: Sat, 25 Feb 2017 21:18:00 -0800

If you want to shut out the overwhelming majority of vulnerabilities in Microsoft products, turn off admin rights on the PC.

That’s the conclusion from global endpoint security firm Avecto, which has issued its annual Microsoft Vulnerabilities report. It found that there were 530 Microsoft vulnerabilities reported in 2016, and of these critical vulnerabilities, 94% were found to be mitigated by removing admin rights, up from 85% reported last year.

This is especially true with the browser, for those who still use Microsoft’s browsers. 100% of vulnerabilities impacting both Internet Explorer and Edge could be mitigated by removing admin rights, Avecto reported. One bit of progress is that 109 vulnerabilities impacting IE 6 through 11 were reported in 2016, way down from 238 in the previous year.

To read this article in full or to leave a comment, please click here
Read More
IndependentKrebs

iPhone Robbers Try to iPhish Victims

Credit to Author: BrianKrebs| Date: Fri, 24 Feb 2017 21:21:24 +0000

In another strange tale from the kinetic-attack-meets-cyberattack department, earlier this week I heard from a loyal reader in Brazil whose wife was recently mugged by three robbers who nabbed her iPhone. Not long after the husband texted the stolen phone — offering to buy back the locked device — he soon began receiving text messages stating the phone had been found. All he had to do to begin the process of retrieving the device was click the texted link and log in to the phishing page mimicking Apple’s site.

Read More
ComputerWorldIndependent

Google discloses unpatched IE flaw after Patch Tuesday delay

Credit to Author: Lucian Constantin| Date: Fri, 24 Feb 2017 10:44:00 -0800

Google’s Project Zero team has disclosed a potential arbitrary code execution vulnerability in Internet Explorer because Microsoft has not acted within Google’s 90-day disclosure deadline.

This is the second flaw in Microsoft products made public by Google Project Zero since the Redmond giant decided to skip this month’s Patch Tuesday and postpone its previously planned security fixes until March.

Microsoft blamed the unprecedented decision to push back scheduled security updates by a month on a “last minute issue” that could have had an impact on customers, but the company hasn’t clarified the nature of the problem.

To read this article in full or to leave a comment, please click here
Read More
ComputerWorldIndependent

FCC puts the brakes on ISP privacy rules it passed in October

Credit to Author: Grant Gross| Date: Fri, 24 Feb 2017 10:43:00 -0800

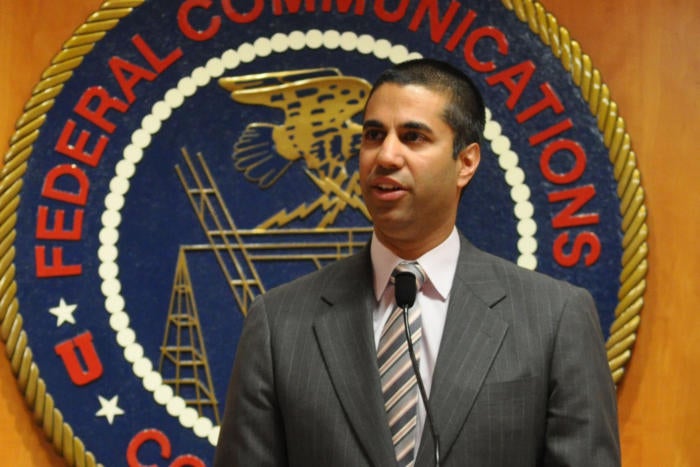
The new chairman of the U.S. Federal Communications Commission will seek a stay on privacy rules for broadband providers that the agency just passed in October.

FCC Chairman Ajit Pai will ask for either a full commission vote on the stay before parts of the rules take effect next Thursday or he will instruct FCC staff to delay part of the rules pending a commission vote, a spokesman said Friday.

The rules, passed when the FCC had a Democratic majority, require broadband providers to receive opt-in customer permission to share sensitive personal information, including web-browsing history, geolocation, and financial details, with third parties. Without the stay, the opt-in requirements were scheduled to take effect next week.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Cloudflare bug exposed passwords, other sensitive website data

Credit to Author: Lucian Constantin| Date: Fri, 24 Feb 2017 08:47:00 -0800

For months, a bug in Cloudflare’s content optimization systems exposed sensitive information sent by users to websites that use the company’s content delivery network. The data included passwords, session cookies, authentication tokens and even private messages.

Cloudflare acts as a reverse proxy for millions of websites, including those of major internet services and Fortune 500 companies, for which it provides security and content optimization services behind the scenes. As part of that process, the company’s systems modify HTML pages as they pass through its servers in order to rewrite HTTP links to HTTPS, hide certain content from bots, obfuscate email addresses, enable Accelerated Mobile Pages (AMP) and more.

To read this article in full or to leave a comment, please click here
Read More