Independent

IndependentSecuriteam

SSD Advisory – Oracle Java FTP Stream Injection

Credit to Author: Maor Schwartz| Date: Tue, 21 Feb 2017 13:51:34 +0000

Vulnerability Summary The following advisory describes a FTP protocol stream injection vulnerability found in Oracle Java. Java is a general-purpose computer programming language that is concurrent, class-based, object-oriented, and specifically designed to have as few implementation dependencies as possible. It is intended to let application developers “write once, run anywhere” (WORA). Credit An independent security … Continue reading SSD Advisory – Oracle Java FTP Stream Injection →

Read More
IndependentSecuriteam

SSD Advisory – HiSilicon multiple vulnerabilities

Credit to Author: Maor Schwartz| Date: Tue, 21 Feb 2017 07:44:16 +0000

Vulnerabilities Summary The following advisory describes 2 vulnerabilities found in HiSilicon application-specific integrated circuit (ASIC) chip set firmware. HiSilicon provides ASICs and solutions for communication network and digital media. These ASICs are widely used in over 100 countries and regions around the world. In the digital media field, HiSilicon has already released the SoC and … Continue reading SSD Advisory – HiSilicon multiple vulnerabilities →

Read More
ComputerWorldIndependent

Java and Python FTP attacks can punch holes through firewalls

Credit to Author: Lucian Constantin| Date: Tue, 21 Feb 2017 10:11:00 -0800

The Java and Python runtimes fail to properly validate FTP URLs, which can potentially allow attackers to punch holes through firewalls to access local networks.

On Saturday, security researcher Alexander Klink disclosed an interesting attack where exploiting an XXE (XML External Entity) vulnerability in a Java application can be used to send emails.

XXE vulnerabilities can be exploited by tricking applications to parse specially crafted XML files that would force the XML parser to disclose sensitive information such as files, directory listings, or even information about processes running on the server.

Klink showed that the same type of vulnerabilities can be used to trick the Java runtime to initiate FTP connections to remote servers by feeding it FTP URLs in the form of ftp://user:password@host:port/file.ext.

To read this article in full or to leave a comment, please click here

Read More
IndependentKrebs

How to Bury a Major Breach Notification

Credit to Author: BrianKrebs| Date: Tue, 21 Feb 2017 17:44:39 +0000

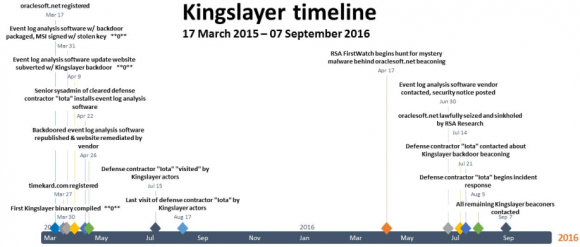
Amid the hustle and bustle of the RSA Security Conference in San Francisco last week, researchers at RSA released a startling report that received very little press coverage relative to its overall importance. The report detailed a malware campaign that piggybacked on a popular piece of software used by system administrators at some of the nation’s largest companies. Incredibly, the report did not name the affected software, and the vendor in question has apparently chosen to bury its breach disclosure. This post is an attempt to remedy that.

Read More
ComputerWorldIndependent

Verizon knocks $350M from Yahoo deal after breaches

Credit to Author: Grant Gross| Date: Tue, 21 Feb 2017 07:23:00 -0800

Verizon Communications will pay $350 million less for Yahoo after two major data breaches reported by the struggling internet pioneer.

Verizon will pay about $4.48 billion for Yahoo’s operating business, and the two companies will share any potential legal and regulatory liabilities arising from two major data breaches announced in late 2016. The companies announced the amended terms of the deal Tuesday.

In October, one news report had Verizon seeking a $1 billion discount after the first breach was announced.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

True privacy online is not viable

Credit to Author: Evan Schuman| Date: Tue, 21 Feb 2017 03:00:00 -0800

Privacy-concerned consumers desperately want a magic bullet, some simple thing they can use that will protect their identities and their web activity. And although there are a plethora of offerings today that make such a claim — VPNs, privacy-focused browsers such as Tor, privacy search engines such as DuckDuckGo, quite a few services that claim to anonymize anyone’s activity — the practical realities of human behavior make such privacy claims bogus.

Let me stress that almost all of these services do indeed help a person remain anonymous from the casual, untrained observer (the typical roommate, spouse, co-worker, boss, etc.). But any consumer who thinks that these tools will thwart a law enforcement agent, motivated cyberthief or identity thief, or anyone who is willing to spend the time to track you down is in for unhappiness.

To read this article in full or to leave a comment, please click here

Read More
IndependentSecuriteam

Know your community – Steven Seeley

Credit to Author: Maor Schwartz| Date: Mon, 20 Feb 2017 06:30:14 +0000

You all know him from Twitter as “mr_me” (@steventseeley) we are proud to interview Steven Seeley! Vulnerability researcher, Ruxcon and HITB speaker, founder of Source Incite and a long time Wing Chun student!! Questions Q: How many years have you been working in the security field? A: I have been working in the industry since … Continue reading Know your community – Steven Seeley →

Read More