Independent

ComputerWorldIndependent

FCC commissioner wants Apple, Google to remove TikTok from App Stores
Credit to Author: Jonny Evans| Date: Wed, 29 Jun 2022 05:34:00 -0700

FCC Commissioner Brendan Carr has written to Apple and Google to request that both companies remove the incredibly popular TikTok app from their stores, citing a threat to national security.

Is your data going TikTok?

Carr warns the app collects huge quantities of data and cited a recent report that claimed the company has accessed sensitive data collected from Americans. He argues that TikTok’s, “pattern of conduct and misrepresentations regarding the unfettered access that persons in Beijing have to sensitive U.S. data…puts it out of compliance,” with App Store security and privacy policies.
To read this article in full, please click here

Read More
IndependentKrebs

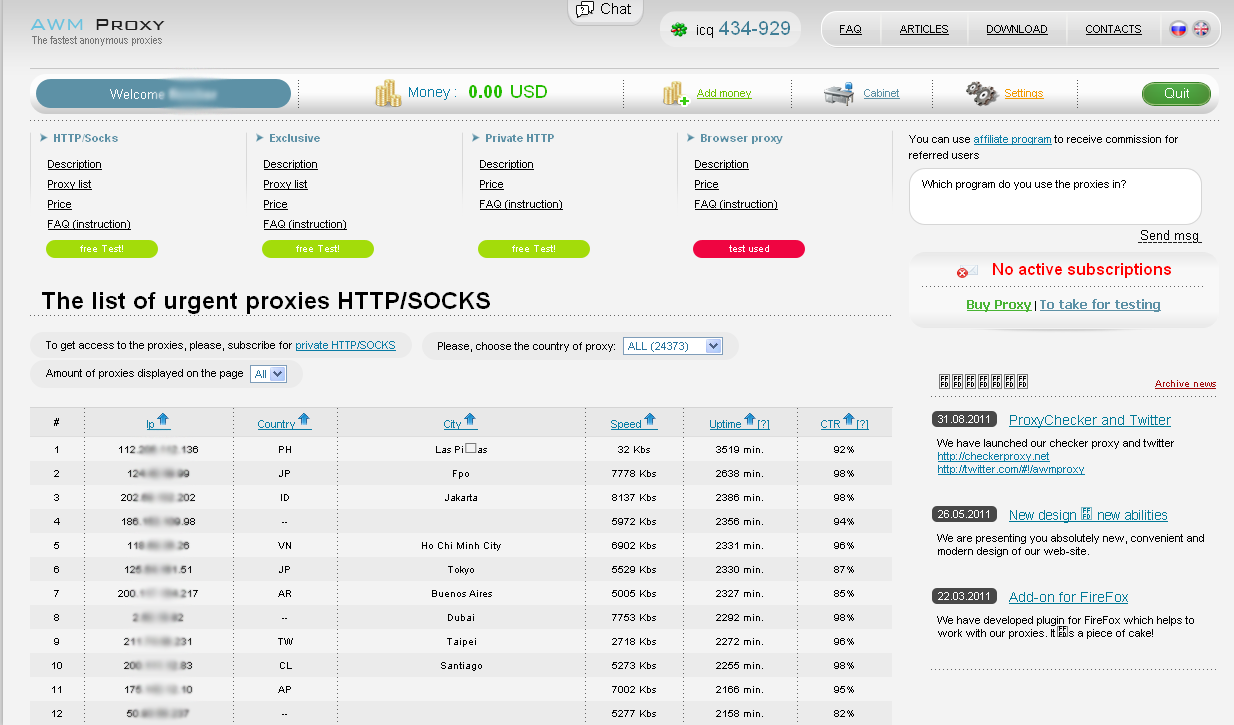
The Link Between AWM Proxy & the Glupteba Botnet

Credit to Author: BrianKrebs| Date: Tue, 28 Jun 2022 18:33:31 +0000

On December 7, 2021, Google announced it had sued two Russian men allegedly responsible for operating the Glupteba botnet, a global malware menace that has infected millions of computers over the past decade. That same day, AWM Proxy — a 14-year-old anonymity service that rents hacked PCs to cybercriminals — suddenly went offline. Security experts had long seen a link between Glupteba and AWM Proxy, but new research shows AWM Proxy’s founder is one of the men being sued by Google.

Read More
ComputerWorldIndependent

How Apple is improving single sign-on

Credit to Author: Jonny Evans| Date: Tue, 28 Jun 2022 07:59:00 -0700

Among a slew of announcements at WWDC this year were some important changes to Apple’s support for single sign-on (SSO). Here’s what’s coming when new updates ship this fall.

SSO + BYOD = iOS 16, iPadOS 16

Apple first introduced SSO support at WWDC 2019 with Sign in with Apple, which also saw the introduction of extensions to enable this kind of authentication. It allowed a user to access a service or website using their Apple ID, and meant support for identity providers, the use of highly secure token-based signatures and the tools service providers required to implement these systems.

To read this article in full, please click here

Read More
ComputerWorldIndependent

Time for a mid-year browser security check

Credit to Author: Susan Bradley| Date: Mon, 27 Jun 2022 09:24:00 -0700

We’ve reached the mid-point of 2022 and when it comes to security, I feel like we’re not making much headway. I still see people report they’re getting scammed, ransomed, and attacked on a regular basis — and for many users the browser is becoming the most important part of whatever platform you use. So now is a good time to review your browsers, and any extensions you’ve installed to beef up security.

Note, I said browsers —plural. While enterprises might want to standardize on only one browser for better control, for small businesses and individual users, I recommend installing more than one. (I often use three different browsers.)

Why is this important? Because attackers (and trackers) go after browsers. In fact, it’s good to think of your browser a separate operating system, and act accordingly to protect it. Though I focus mainly on Windows issues, these guidelines and recommendations apply to Mac OS, Ubunto, Mint, and others.

To read this article in full, please click here

Read More
ComputerWorldIndependent

The surveillance-as-a-service industry needs to be brought to heel

Credit to Author: Jonny Evans| Date: Fri, 24 Jun 2022 09:40:00 -0700

Here we go again: another example of government surveillance involving smartphones from Apple and Google has emerged, and it shows how sophisticated government-backed attacks can become and why there’s justification for keeping mobile platforms utterly locked down.

What has happened?

I don’t intend to focus too much on the news, but in brief it is as follows:

  • Google’s Threat Analysis Group has published information revealing the hack.
  • Italian surveillance firm RCS Labs created the attack.
  • The attack has been used in Italy and Kazakhstan, and possibly elsewhere.
  • Some generations of the attack are wielded with help from ISPs.
  • On iOS, attackers abused Apple’s enterprise certification tools that enable in-house app deployment.
  • Around nine different attacks were used.

The attack works like this: The target is sent a unique link that aims to trick them into downloading and installing a malicious app. In some cases, the spooks worked with an ISP to disable data connectivity to trick targets into downloading the app to recover that connection.

To read this article in full, please click here

Read More
ComputerWorldIndependent

Italian spyware firm is hacking into iOS and Android devices, Google says

Credit to Author: Shweta Sharma| Date: Fri, 24 Jun 2022 08:51:00 -0700

Google’s Threat Analysis Group (TAG) has identified Italian vendor RCS Lab as a spyware offender, developing tools that are being used to exploit zero-day vulnerabilities to effect attacks on iOS and Android mobile users in Italy and Kazakhstan.

According to a Google blog post on Thursday, RCS Lab uses a combination of tactics, including atypical drive-by downloads as initial infection vectors. The company has developed tools to spy on the private data of the targeted devices, the post said.

To read this article in full, please click here

Read More
ComputerWorldIndependent

Apple says it’s time your business ran BIMI

Credit to Author: Jonny Evans| Date: Thu, 23 Jun 2022 06:41:00 -0700

Apple will add another obstacle against successful phishing attacks in iOS 16, iPadOS 16, and macOS Ventura, which will show a company’s official logo to help recipients recognize genuine from fake emails.

Brand Indicators for Message Identification

Apple’s forthcoming operating systems will support Brand Indicators for Message Identification (BIMI). This is a specification to enable the use of brand-controlled logos within emails and will be a way to tell recipients that an email genuinely comes from the company concerned. Google has supported BIMI since 2021.

To read this article in full, please click here

Read More
IndependentKrebs

Meet the Administrators of the RSOCKS Proxy Botnet

Credit to Author: BrianKrebs| Date: Wed, 22 Jun 2022 13:06:34 +0000

Authorities in the United States, Germany, the Netherlands and the U.K. last week said they dismantled the “RSOCKS” botnet, a collection of millions of hacked devices that were sold as “proxies” to cybercriminals looking for ways to route their malicious traffic through someone else’s computer. While the coordinated action did not name the Russian hackers allegedly behind RSOCKS, KrebsOnSecurity has identified its owner as a Russian man living abroad who also runs the world’s top Russian spamming forum.

Read More