Independent

IndependentKrebs

Conti Ransomware Group Diaries, Part II: The Office
Credit to Author: BrianKrebs| Date: Wed, 02 Mar 2022 17:49:52 +0000

Earlier this week, a Ukrainian security researcher leaked almost two years’ worth of internal chat logs from Conti, one of the more rapacious and ruthless ransomware gangs in operation today. Tuesday’s story examined how Conti dealt with its own internal breaches and attacks from private security firms and governments. In Part II of this series we’ll explore what it’s like to work for Conti, as described by the Conti employees themselves.

Read More
IndependentKrebs

Conti Ransomware Group Diaries, Part I: Evasion

Credit to Author: BrianKrebs| Date: Tue, 01 Mar 2022 20:50:30 +0000

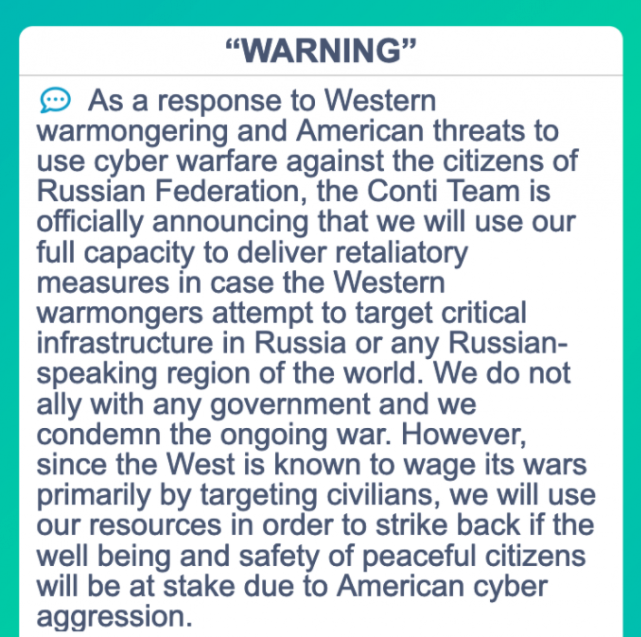
A Ukrainian security researcher this week leaked several years of internal chat logs and other sensitive data tied to Conti, an aggressive and ruthless Russian cybercrime group that focuses on deploying its ransomware to companies with more than $100 million in annual revenue. The chat logs offer a fascinating glimpse into the challenges of running a sprawling criminal enterprise with more than 100 salaried employees. The records also provide insight into how Conti has dealt with its own internal breaches and attacks from private security firms and foreign governments.

Read More
ComputerWorldIndependent

In a time of war, it’s important to stay secure

Credit to Author: Susan Bradley| Date: Mon, 28 Feb 2022 06:09:00 -0800

As Russia invaded Ukraine, seeing the disruption in the world occur in near real time on social media brought poignancy to what was happening. While I don’t know anyone in Ukraine, I know many people who have friends or family members that have been impacted by the war. Ukraine has many technology ties around the world. It’s also been a source of cyberattacks, which is why there’s extra concern about what we can do to protect ourselves in case of attack. (Eastern Europe has often been the source of many of the ransomware attacks that occur around the world.)

So what can tech users do to ensure you protect yourself from possible cyberattacks arising from the conflict?

To read this article in full, please click here

Read More
ComputerWorldIndependent

Behavioral Analytics is getting trickier

Credit to Author: Evan Schuman| Date: Mon, 28 Feb 2022 03:00:00 -0800

Behavioral analytics is one of the best authentication methods around — especially when it’s part of continuous authentication. Authentication as a “one-and-done” is something that simply shouldn’t happen anymore. Then again, I’ve argued the same thing about using unencrypted SMS as a form of multi-factor authentication and I sadly still see that being used by lots of Fortune 1000 firms.

Oh well.

Although most enterprise CISOs are fine with behavioral analytics on paper (on a whiteboard? As a message within Microsoft Teams/GoogleMeet/Zoom?), they’re resistant to rapid widespread deployment because it requires creating a profile for every user — including partners, distributors, suppliers, large customers and anyone else who needs system access. Those profiles can take more than a month to create to get an accurate, consistent picture of each person.

To read this article in full, please click here

Read More
IndependentKrebs

Russia Sanctions May Spark Escalating Cyber Conflict

Credit to Author: BrianKrebs| Date: Fri, 25 Feb 2022 19:10:04 +0000

President Biden joined European leaders this week in enacting economic sanctions against Russia in response its military invasion of Ukraine. The West has promised tougher sanctions are coming, but experts warn these will almost certainly trigger a Russian retaliation against America and its allies, which could escalate into cyber attacks on Western financial institutions and energy infrastructure.

Read More
ComputerWorldIndependent

Windows is in Moscow’s crosshairs, too

Credit to Author: Preston Gralla| Date: Fri, 25 Feb 2022 03:00:00 -0800

Russia telegraphed its intentions to invade Ukraine well ahead of this week’s attack by massing nearly 200,000 soldiers along Ukraine’s borders, and by Vladimir Putin’s increasingly belligerent threats.

Behind the scenes, Russia was doing more than that, including dangerous cyberattacks launched against Ukraine. And as is typically the case in such attacks, Windows was the attack vector.

“We’ve observed destructive malware in systems belonging to several Ukrainian government agencies and organizations that work closely with the Ukrainian government, Tom Burt, Microsoft corporate vice president for customer security and trust, wrote in a blog post in mid-January. “The malware is disguised as ransomware but, if activated by the attacker, would render the infected computer system inoperable.” In a related technical post detailing how the malware works, Microsoft added: “These systems [under cyberattack] span multiple government, non-profit, and information technology organizations, all based in Ukraine.”

To read this article in full, please click here

Read More