Independent

ComputerWorldIndependent

Microsoft beefs up Edge's security against zero-day attacks
Credit to Author: Lucas Mearian| Date: Thu, 20 Jan 2022 13:16:00 -0800

In the latest release of its Edge beta, Microsoft introduced a new way for IT admins to better secure the Chromium-based browser against web-based attacks.

The release notes for Microsoft Edge Beta Channel describe the new security features as employing several techniques to guard against so-called zero-day exploits; Zero-day exploits are software or network vulnerabilities developers are unaware of, and so they’ve not been patched.

Imagine if the keylock mechanism on your home’s backdoor was faulty and jiggling the doorknob released the latch. Burglars could walk door to door looking for that particular vulnerability and jiggle doorknobs until one opened. Zero days are the same concept, but in cyberspace.
To read this article in full, please click here

Read More
IndependentKrebs

Fake Investor John Bernard Sinks Norwegian Green Shipping Dreams

Credit to Author: BrianKrebs| Date: Sat, 29 Jan 2022 18:05:52 +0000

Several articles here have delved into the history of John Bernard, the pseudonym used by a fake billionaire technology investor who’s tricked dozens of start-ups into giving him tens of millions of dollars. Bernard’s latest victim — a Norwegian startup hoping to build a fleet of environmentally friendly shipping vessels — is now embroiled in a lawsuit over a deal gone bad, in which Bernard falsely claimed to have secured $100 million from six other wealthy investors, including the founder of Uber and the artist Abel Makkonen Tesfaye, better known as The Weeknd.

Read More
ComputerWorldIndependent

How to keep your apps up to date in Windows 10 and 11

Credit to Author: Ed Tittel| Date: Wed, 19 Jan 2022 03:00:00 -0800

Look around a typical Windows desktop. Whether it’s running Windows 10 or 11, chances are that it’s running at least a couple of dozen Windows applications (.exe files), and at least four dozen Microsoft Store apps. On my local fleet of 10 PCs, the range for applications is from a low of 24 to a high of 120; for Store apps, it ranges from 49 to 81. Such numbers are quite typical, if my online research is at all accurate.

In general, it’s considered good security practice to keep apps and applications up-to-date. Why? Because many updates involve security patches and fixes that block potential attacks and prevent unauthorized and unwanted access to applications and their data (and sometimes, the host OS and the PCs they run on). In this story, I will offer some tools to help you streamline this process, along with some instructions on how to put them to work to help you keep your apps and applications current and safe.

To read this article in full, please click here

Read More
IndependentKrebs

Who Wrote the ALPHV/BlackCat Ransomware Strain?

Credit to Author: BrianKrebs| Date: Fri, 28 Jan 2022 13:18:36 +0000

In December 2021, researchers discovered a new ransomware-as-a-service named ALPHV (a.k.a. “BlackCat”), considered to be the first professional cybercrime group to create and use a ransomware strain in the Rust programming language. In this post, we’ll explore some of the clues left behind by the developer who was reputedly hired to code the ransomware variant.

Read More
ComputerWorldIndependent

20 years after Gates’ call for trustworthy computing, we’re still not there

Credit to Author: Susan Bradley| Date: Mon, 17 Jan 2022 03:42:00 -0800

Do you feel more secure? Is your computing experience more trustworthy these days?

Seriously — you’re reading this article on a computer or phone, connecting to this site on an internet shared with your Grandma as well as Russian hackers, North Korean attackers, and lots of teenagers  looking at TikTok videos. It’s been 20 years since then-Microsoft CEO Bill Gates wrote his Trustworthy Computing memo where he emphasized security in the company’s products.

So are we actually more secure now?

I’m going to keep in mind the side effects from last week’s Patch Tuesday security updates and consider them in my answer. First, the good news: I don’t see major side effects occurring on PCs not connected to active directory domains (and I haven’t seen any showstoppers in testing my hardware at home). I can still print to my local HP and Brother printers. I can surf and access files. So, while I’m not ready yet to give an all-clear to install the January updates, when I do, I doubt you’ll see side effects.

To read this article in full, please click here

Read More
IndependentKrebs

Scary Fraud Ensues When ID Theft & Usury Collide

Credit to Author: BrianKrebs| Date: Tue, 25 Jan 2022 19:48:40 +0000

What’s worse than finding out that identity thieves took out a 546 percent interest payday loan in your name? How about a 900 percent interest loan? Or how about not learning of the fraudulent loan until it gets handed off to collection agents? One reader’s nightmare experience spotlights what can happen when ID thieves and hackers start targeting online payday lenders.

Read More
IndependentKrebs

Crime Shop Sells Hacked Logins to Other Crime Shops

Credit to Author: BrianKrebs| Date: Fri, 21 Jan 2022 17:11:36 +0000

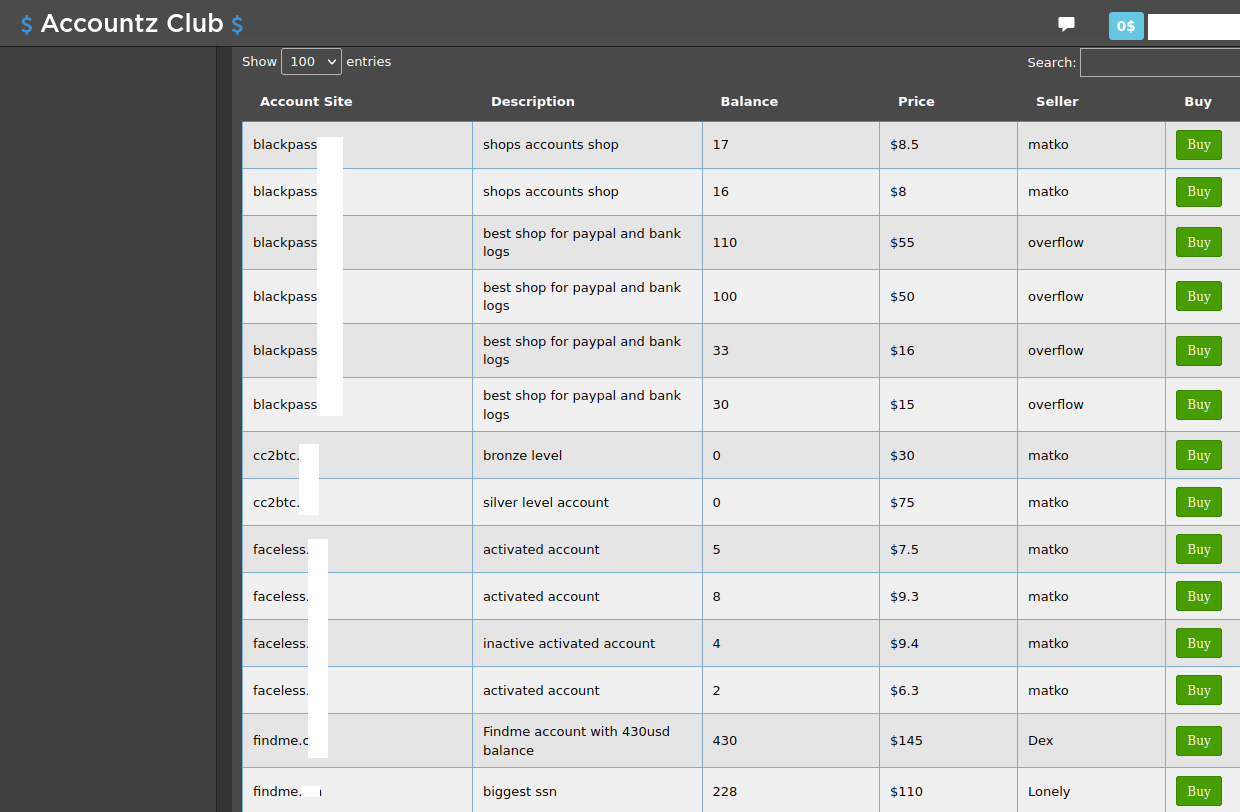
Up for the “Most Meta Cybercrime Offering” award this year is Accountz Club, a new cybercrime store that sells access to purloined accounts at services built for cybercriminals, including shops peddling stolen payment cards and identities, spamming tools, email and phone bombing services, and those selling authentication cookies for a slew of popular websites.

Read More
ComputerWorldIndependent

Patch Tuesday gets off to a busy start for January

Credit to Author: Greg Lambert| Date: Fri, 14 Jan 2022 12:10:00 -0800

For this week’s Patch Tuesday, the first of the year, Microsoft addressed 97 security issues, six of them rated critical. Though six vulnerabilities have been publicly reported, I do not classify them as zero-days. Microsoft has fixed a lot of security related issues and is aware of several known issues that may have inadvertently caused significant server issues including:

  • Hyper-V, which no longer starts with the message, “Virtual machine xxx could not be started because the hypervisor is not running.”
  • ReFS (Resilient) file systems that are no longer accessible (which is kind of ironic).
  • And Windows domain controller boot loops.

There are a variety of known issues this month, and I’m not sure whether we’ll see more issues reported with the January server patches. You can find more information on the risk of deploying these latest updates with our helpful infographic.

To read this article in full, please click here

Read More