Credit to Author: BrianKrebs| Date: Mon, 03 Dec 2018 17:25:58 +0000
The parent firm of bling retailers Jared and Kay Jewelers has fixed a bug in the Web sites of both companies that exposed the order information for all of their online customers.
Credit to Author: BrianKrebs| Date: Sat, 01 Dec 2018 21:16:13 +0000
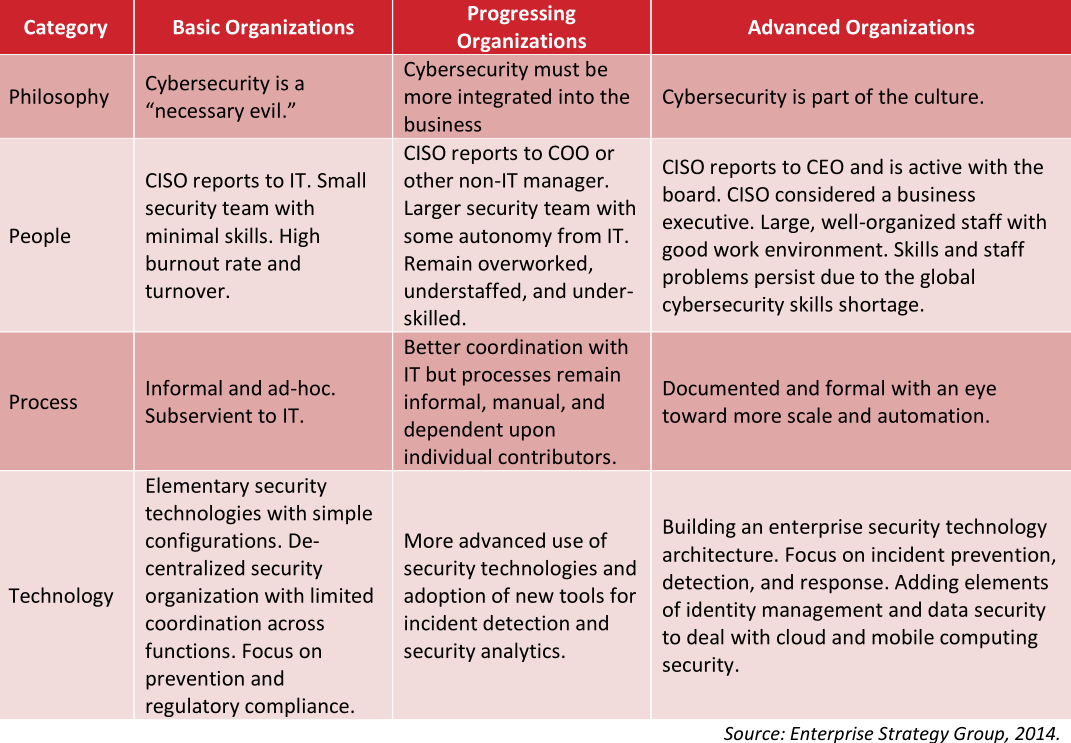
We don’t yet know the root cause(s) that forced Marriott this week to disclose a four-year-long breach involving the personal and financial information of 500 million guests of its Starwood hotel properties. But anytime we see such a colossal intrusion go undetected for so long, the ultimate cause is usually a failure to adopt the most important principle in cybersecurity defense that applies to both corporations and consumers: Assume you are compromised.
Credit to Author: BrianKrebs| Date: Fri, 30 Nov 2018 13:47:51 +0000
Hospitality giant Marriott today disclosed a massive data breach exposing the personal and financial information on as many as a half billion customers who made reservations at any of its Starwood properties over the past four years.
Credit to Author: BrianKrebs| Date: Mon, 26 Nov 2018 14:57:53 +0000
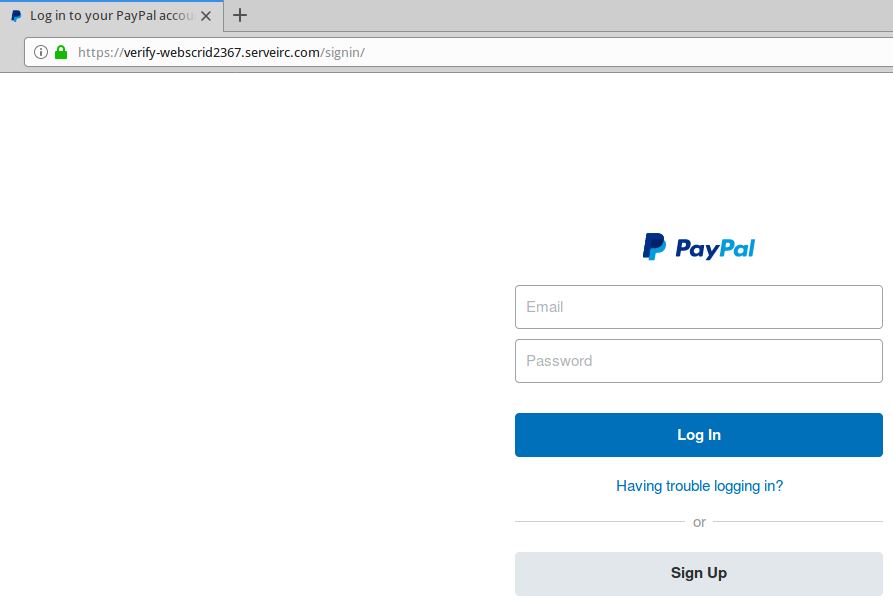
Maybe you were once advised to “look for the padlock” as a means of telling legitimate e-commerce sites from phishing or malware traps. Unfortunately, this has never been more useless advice. New research indicates that half of all phishing scams are now hosted on Web sites whose Internet address includes the padlock and begins with “https://”.
Credit to Author: BrianKrebs| Date: Fri, 23 Nov 2018 23:24:06 +0000
‘Tis the season when even those who know a thing or two about Internet scams tend to let down their guard in the face of an eye-popping discount or the stress of last-minute holiday shopping. So here’s a quick refresher course on how to make it through the next few weeks without getting snookered online.
Credit to Author: BrianKrebs| Date: Wed, 21 Nov 2018 17:10:18 +0000
U.S. Postal Service just fixed a security weakness that allowed anyone who has an account at usps.com to view account details for some 60 million other users, and in some cases to modify account details on their behalf. KrebsOnSecurity was contacted last week by a researcher who discovered the problem, but who asked to remain anonymous. The researcher said he informed the USPS about his finding more than a year ago yet never received a response. After confirming his findings, this author contacted the USPS, which promptly addressed the issue.
Credit to Author: BrianKrebs| Date: Wed, 14 Nov 2018 20:27:01 +0000
A California man who pleaded guilty Tuesday to causing dozens of swatting attacks — including a deadly incident in Kansas last year — now faces 20 or more years in prison.
Credit to Author: BrianKrebs| Date: Wed, 14 Nov 2018 13:25:13 +0000
Microsoft on Tuesday released 16 software updates to fix more than 60 security holes in various flavors of Windows and other Microsoft products. Adobe’s also got security patches available for Flash, Acrobat and Adobe Reader users.