Krebs

IndependentKrebs

The Year Targeted Phishing Went Mainstream
Credit to Author: BrianKrebs| Date: Thu, 02 Aug 2018 15:11:45 +0000

A story published here on July 12 about a new sextortion-based phishing scheme that invokes a real password used by each recipient has become the most-read piece on KrebsOnSecurity since this site launched in 2009. And with good reason — sex sells (the second most-read piece here was my 2015 scoop about the Ashley Madison hack). But beneath the lurid allure of both stories lies a more unsettling reality: It has never been easier for scam artists to launch convincing, targeted phishing and extortion scams that are automated on a global scale. And given the sheer volume of hacked and stolen personal data now available online, it seems almost certain we will soon witness many variations on these phishing campaigns that leverage customized data elements to enhance their effectiveness.

Read More
IndependentKrebs

Reddit Breach Highlights Limits of SMS-Based Authentication

Credit to Author: BrianKrebs| Date: Thu, 02 Aug 2018 00:55:17 +0000

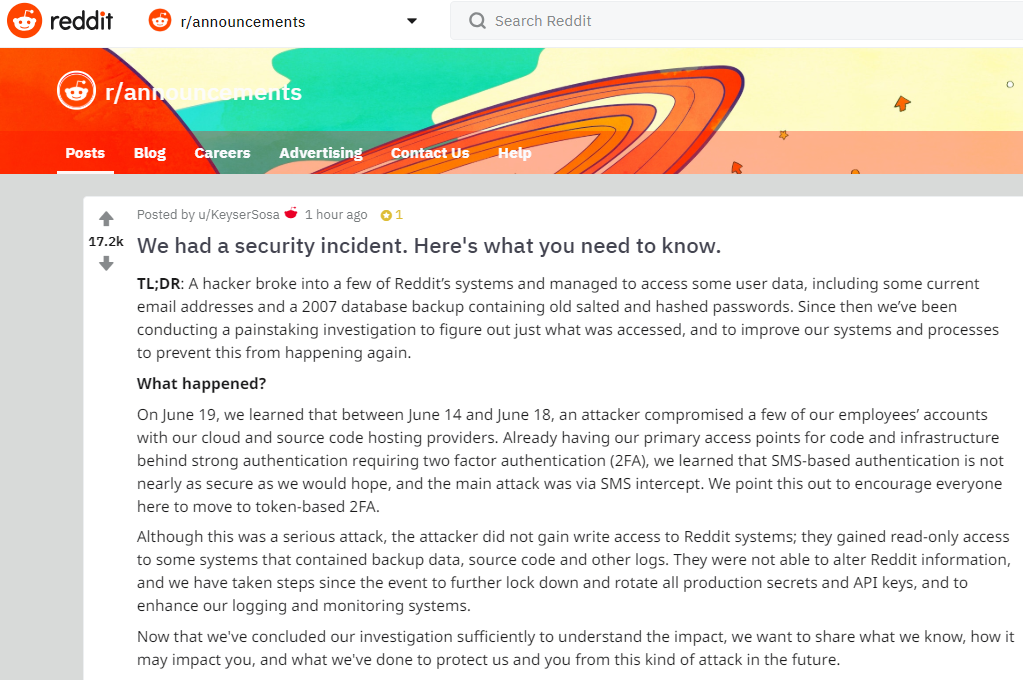
Reddit.com today disclosed that a data breach exposed some internal data, as well as email addresses and passwords for some Reddit users. As Web site breaches go, this one doesn’t seem too severe. What’s interesting about the incident is that it showcases once again why relying on mobile text messages (SMS) for two-factor authentication (2FA) can lull companies and end users into a false sense of security.

Read More
IndependentKrebs

State Govts. Warned of Malware-Laden CD Sent Via Snail Mail from China

Credit to Author: BrianKrebs| Date: Fri, 27 Jul 2018 15:45:09 +0000

Here’s a timely reminder that email isn’t the only vector for phishing attacks: Several U.S. state and local government agencies have reported receiving strange letters via snail mail that include malware-laden compact discs (CDs) apparently sent from China, KrebsOnSecurity has learned. This particular ruse, while crude and simplistic, preys on the curiosity of recipients who may be enticed into popping the CD into a computer. According to a non-public alert sent by the Multi-State Information Sharing and Analysis Center (MS-ISAC), the scam arrives in a Chinese postmarked envelope and includes a “confusingly worded typed letter with occasional Chinese characters.”

Read More
IndependentKrebs

LifeLock Bug Exposed Millions of Customer Email Addresses

Credit to Author: BrianKrebs| Date: Wed, 25 Jul 2018 22:20:46 +0000

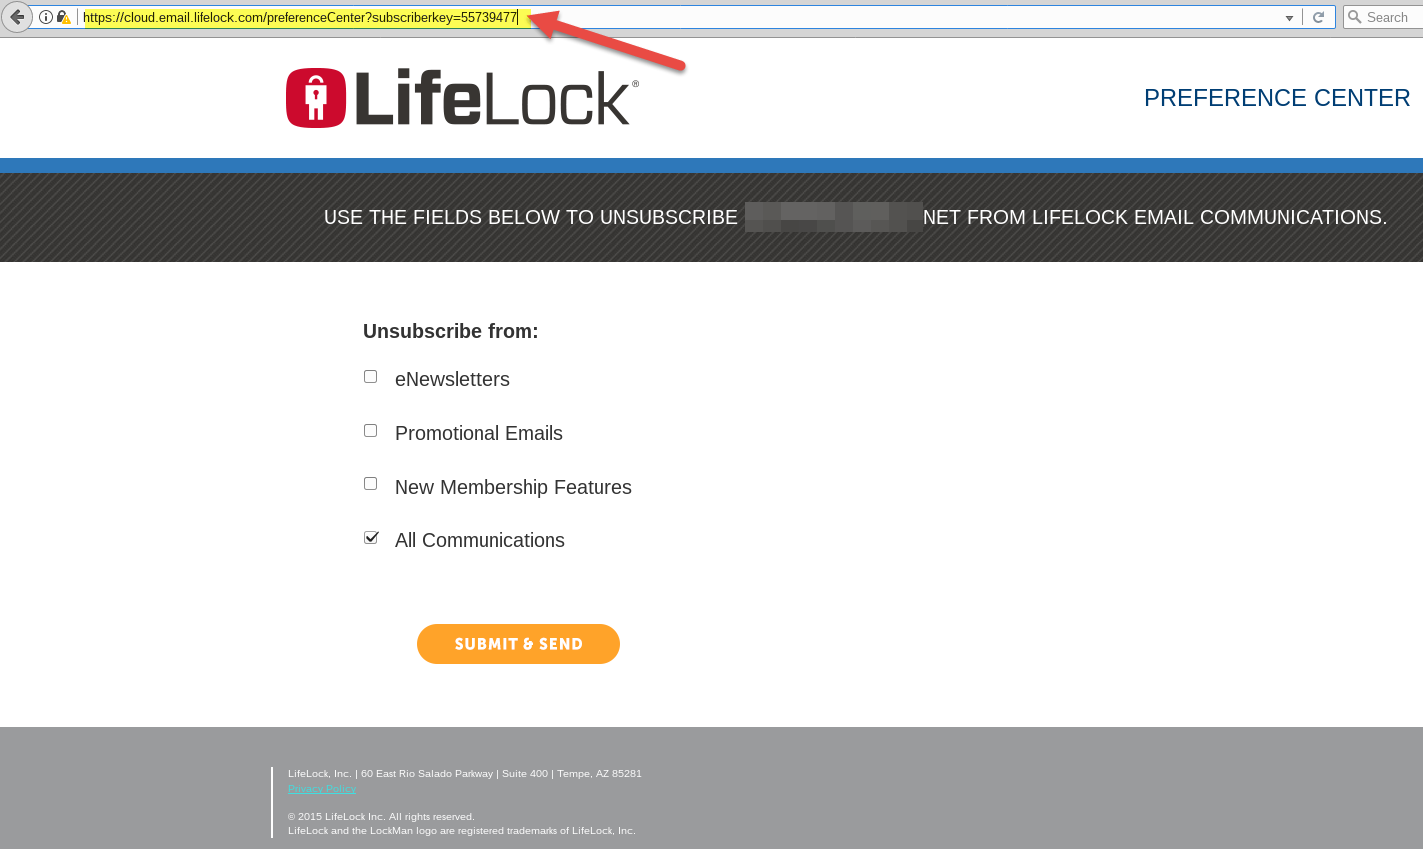
Identity theft protection firm LifeLock — a company that’s built a name for itself based on the promise of helping consumers protect their identities online — may have actually exposed customers to additional attacks from ID thieves and phishers. The company just fixed a vulnerability on its Web site that allowed anyone with a Web browser to index email addresses associated with millions of customer accounts, or to unsubscribe users from all communications from the company. The upshot of this weakness is that cyber criminals could harvest the data and use it in targeted phishing campaigns that spoof LifeLock’s brand. Of course, phishers could spam the entire world looking for LifeLock customers without the aid of this flaw, but nevertheless the design of the company’s site suggests that whoever put it together lacked a basic understanding of Web site authentication and security. The upshot of this weakness is that cyber criminals could harvest the data and use it in targeted phishing campaigns that spoof LifeLock’s brand. Of course, phishers could spam the entire world looking for LifeLock customers without the aid of this flaw, but nevertheless the design of the company’s site suggests that whoever put it together it lacked a basic understanding of authentication and security.

Read More
IndependentKrebs

Human Resources Firm ComplyRight Breached

Credit to Author: BrianKrebs| Date: Thu, 19 Jul 2018 21:08:43 +0000

Cloud-based human resources company ComplyRight said this week that a security breach of its Web site may have jeopardized sensitive consumer information — including names, addresses, phone numbers, email addresses and Social Security numbers — from tax forms submitted by the company’s thousands of clients on behalf of employees. Cloud-based human resources company ComplyRight said this week that a security breach of its Web site may have jeopardized sensitive consumer information — including names, addresses, phone numbers, email addresses and Social Security numbers — from tax forms submitted by the company’s clients on behalf of employees. Pompano Beach, Fla-based ComplyRight began mailing breach notification letters to affected consumers late last week, but the form letters are extremely vague about the scope and cause of the breach. Indeed, many readers who received these letters wrote to KrebsOnSecurity asking for more information, as the company hadn’t yet published any details about the breach on its Web site. Also, most of those folks said they’d never heard of ComplyRight and could not remember ever doing business with a company by that name.

Read More