How Zero Trust and XDR Work Together
As the Zero Trust approach gains momentum, more organizations are looking to apply it to their security strategy. Learn how XDR and Zero Trust work together to enhance your security posture.
RSS Reader for Computer Security Articles
As the Zero Trust approach gains momentum, more organizations are looking to apply it to their security strategy. Learn how XDR and Zero Trust work together to enhance your security posture.

FortiGuard Labs analyzes vulnerabilities in Microsoft Active-Directory (CVE-2021-42278 and CVE-2021-42287). Analysis shows that by combining them, it is possible for a regular user to easily impersonate a domain admin. Learn more about the exploitation of these vulnerabilities.
Credit to Author: Veronica Chierzi| Date: Thu, 09 Dec 2021 00:00:00 +0000
In our study, we relied on the tactics, techniques, and procedures of MITRE ATT&CK to define the malware capabilities and characteristics of IoT Linux malware. We describe our findings and how IoT malware has been evolving.
Read More
FortiGuard Labs provides important updates about the Apache Log4j vulnerabilities, including details, campaigns associated with Log4j, and an alleged “wormable” Mirai malware variant. Read to learn more.
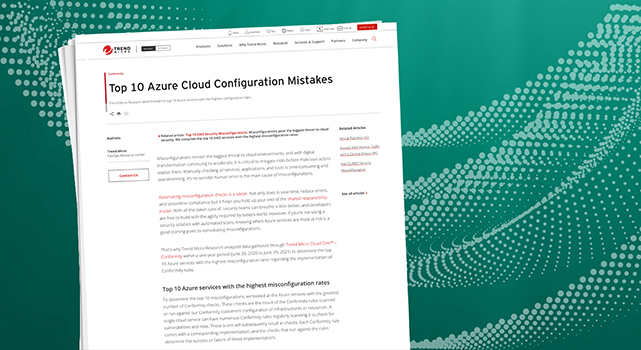
Trend Micro Research determined the top 10 Azure services with the highest configuration rates.

FortiGuard Labs recently caught a phishing campaign that delivers a malicious PowerPoint file spreading a new variant of Agent Tesla. Read to learn more about the malicious macro, payload, and how the malware maintains persistence as well as how it exfiltrates stolen data and credentials.

FortiGuard Labs encountered a malware sample that’s currently being distributed in the wild targeting TP-link wireless routers. Learn more on MANGA aka Dark Mirai-based Campaign.

FortiGuard Labs analyzes how an attacker can leverage CVE-2021-36260 to create targets for Moobot which is a DDoS botnet based on Mirai. In this blog we explain how an attacker delivers this payload along with details of the botnet.