IndependentSecuriteam

Know your community – Simone Margaritelli (@evilsocket)

Credit to Author: SSD / Maor Schwartz| Date: Tue, 16 May 2017 11:57:33 +0000

The guy that published a first hand account of how an allegedly government-sponsored firm, Dark Matter, tried to hire him to help them spy on civilian in the UAE. A former BlackHat that switch sides Bug Bounty hunter The author of the most known offensive open source software – BetterCAP, dSploit, AndroSwat and more! Please … Continue reading Know your community – Simone Margaritelli (@evilsocket)

Read More
IndependentSecuriteam

SSD Advisory – AContent Multiple Vulnerabilities

Credit to Author: SSD / Maor Schwartz| Date: Tue, 16 May 2017 05:32:18 +0000

Vulnerabilities Summary The following advisory describes two (2) vulnerabilities types found in AContent version 1.3. AContent is an open source learning content management system (LCMS) used to create interoperable, accessible, adaptive Web-based learning content. It can be used along with learning management systems to develop, share, and archive learning materials. For those familiar with ATutor, … Continue reading SSD Advisory – AContent Multiple Vulnerabilities

Read More
FortinetSecurity

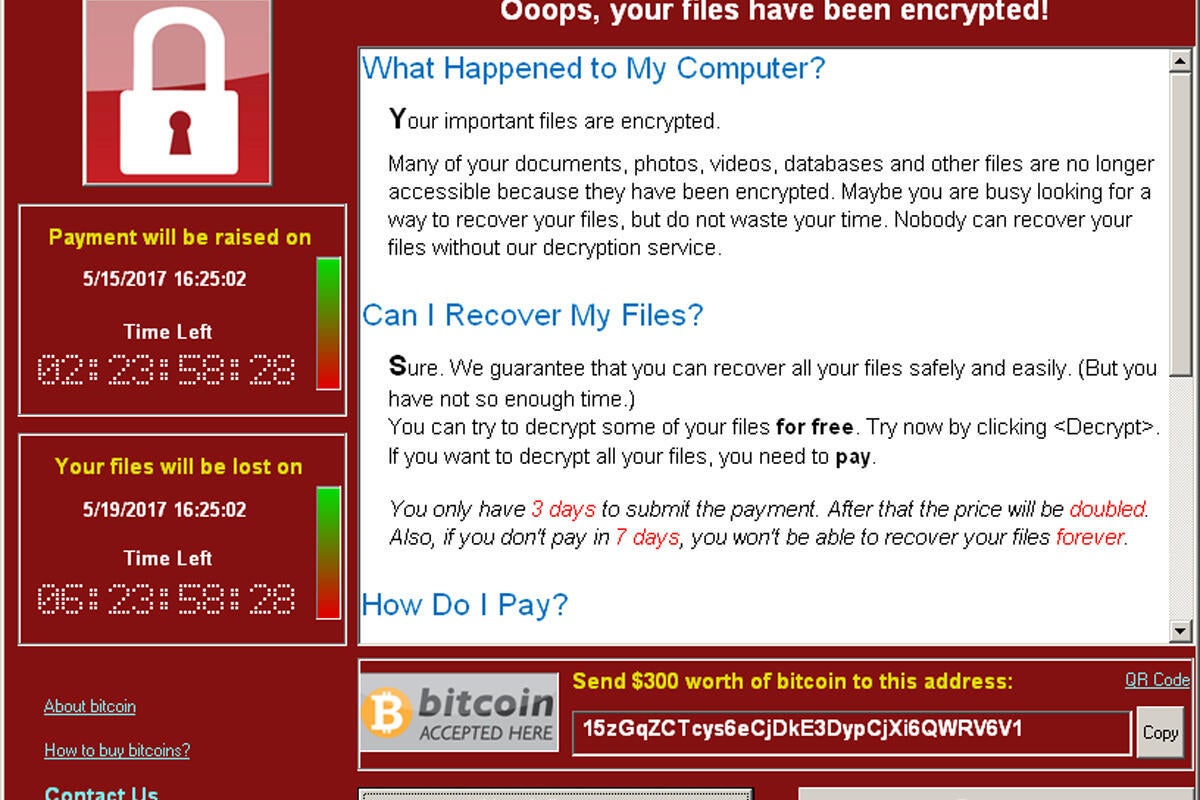
WannaCry: Evolving History from Beta to 2.0

Credit to Author: Kyle Yang| Date: Mon, 15 May 2017 07:12:56 -0700

The WannaCry malware was responsible for a massive infection beginning that affected organizations and systems around the world. FortiGuard Labs has been monitoring this malware carefully. We have provided an analysis of this attack, along with how to protect your organization here.  In this blog post I’ll briefly describe some of the distinct characteristics of each version of this malware, from beta to the latest 2.0 version, and share some interesting findings. Beta Version: We discovered this beta version around Feb 9th,…

Read More
ComputerWorldIndependent

WannaCry: Sometimes you can blame the victims

Credit to Author: Ira Winkler| Date: Tue, 16 May 2017 05:46:00 -0700

The WannaCry ransomware attack has created at least tens of millions of dollars of damage, taken down hospitals, and as of the time of this writing, another round of attacks is considered imminent as people show up to work after the weekend. Of course, the perpetrators of the malware are to blame for all the damage and suffering that has resulted. It’s not right to blame the victims of a crime, right?

Well, actually, there are cases when victims have to shoulder a portion of the blame. They may not be criminally liable as accomplices in their own victimhood, but ask any insurance adjuster whether a person or institution has a responsibility to take adequate precautions against actions that are fairly predictable. A bank that leaves bags of cash on the sidewalk overnight instead of in a vault is going to have a hard time getting indemnified if those bags go missing.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Missing protection: Corporate B2B privacy policies

Credit to Author: Evan Schuman| Date: Tue, 16 May 2017 04:00:00 -0700

Read More
IndependentKrebs

Breach at DocuSign Led to Targeted Email Malware Campaign

Credit to Author: BrianKrebs| Date: Tue, 16 May 2017 03:34:58 +0000

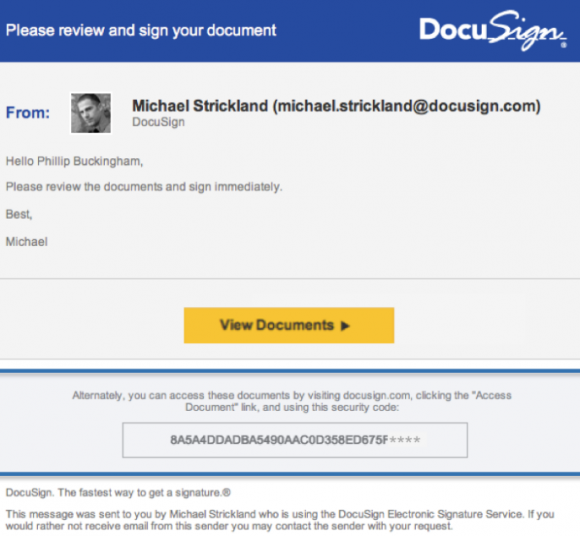
DocuSign, a major provider of electronic signature technology, acknowledged today that a series of recent malware phishing attacks targeting its customers and users was the result of a data breach at one of its computer systems. The company stresses that the data stolen was limited to customer and user email addresses, but the incident is especially dangerous because it allows attackers to target users who may already be expecting to click on links in emails from DocuSign.

Read More