FortinetSecurity

Watch Out For Fake Online Gaming Sites And Their Malicious Executables


Every year during holiday seasons, the number of phishing websites increases. This is particularly true for online gaming distribution platforms. In some cases, users not only have their login credentials stolen, but they also end up downloading and executing malicious executables. As expected, the more popular a platform is, the more targeted it will be, which is why this research blog focuses on two malware samples obtained from fake Origin and Steam websites. Figure 1. Fake Origin phishing website Origin Malware Sample In addition…

Read More
FortinetSecurity

The Analysis of ISC BIND Response Authority Section RRSIG Missing DoS (CVE-2016-9444)


Domain Name System Security Extensions (DNSSEC) secures the Domain Name System (DNS), right? Yes, but that’s not the whole story. DNSSEC can also introduce troubles into your DNS server. Recently, a BIND bug caused by a missing RRSIG record, which is a part of DNSSEC, was fixed by a patch from the Internet Systems Consortium (ISC). This bug affects all versions of BIND recursive servers, and can cause a denial of service (DoS.) This potential DoS vulnerability is caused by a RUNTIME CHECK error in Resolver.c when handling the DNS…

Read More
ComputerWorldIndependent

TV maker Vizio pays $2.2M to settle complaint that it spied on users

Popular smart TV maker Vizio will pay $2.2 million to settle complaints that it violated customers’ privacy by continuously monitoring their viewing habits without their knowledge.

Beginning in February 2014, the Irvine, California-based TV maker tracked what TV shows customers were watching on 11 million TV sets sold in the U.S., the Federal Trade Commission and the Office of the New Jersey Attorney General said in a complaint, released Monday.

Vizio smart TVs captured “second-by-second” information about video displayed, including video from consumer cable services, broadband, set-top boxes, DVDs, over-the-air broadcasts and streaming devices, according to the complaint.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Malware distributors switch to less suspicious file types

After aggressively using JavaScript email attachments to distribute malware for the past year, attackers are now switching to less suspicious file types to trick users.

Last week, researchers from the Microsoft Malware Protection Center warned about a new wave of spam emails that carried malicious .LNK files inside ZIP archives. Those files had malicious PowerShell scripts attached to them.

PowerShell is a scripting language for automating Windows system administration tasks. It has been abused to download malware in the past and there are even malware programs written entirely in PowerShell.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Researchers’ quantum hacking machine may help protect against quantum computing hacks

There seems to be no form of computing which is safe from hacking, but some, such as the Chinese, have pinned their hopes on quantum computing having uncrackable communications. Yet University of Ottawa researchers have managed to build “the first high-dimensional quantum cloning machine capable of performing quantum hacking to intercept a secure quantum message.”

Last year, China launched the world’s first known quantum communications satellite; the Chinese believed its Quantum Experiments at Space Scale (QUESS) satellite was a step toward “creating an unhackable communications system.” While it may seem like the Canadian researchers have poked holes in the dream of secure quantum communications, the opposite may actually be true.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Hacker hijacks thousands of publicly exposed printers to warn owners

Following recent research that showed many printer models are vulnerable to attacks, a hacker decided to prove the point and forced thousands of publicly exposed printers to spew out rogue messages.

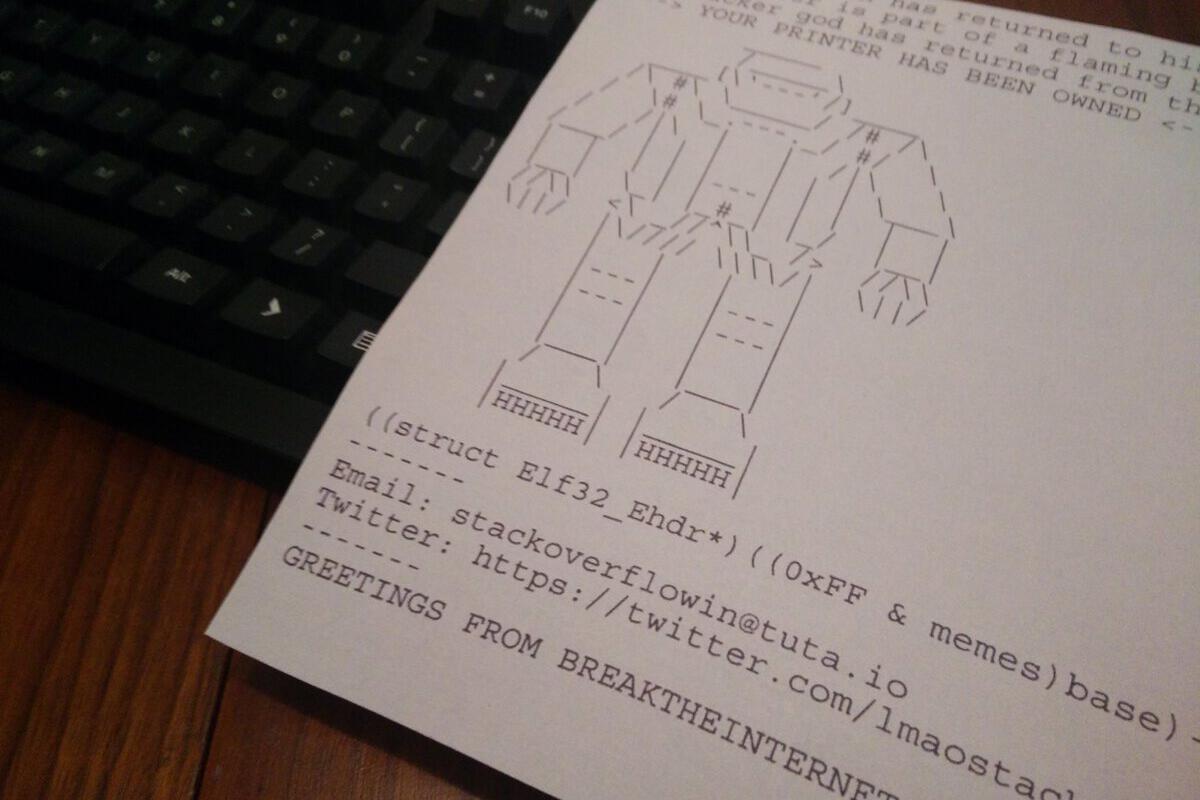
The messages included ASCII art depicting robots and warned that the printers had been compromised and they were part of a botnet. The hacker, who uses the online alias Stackoverflowin, later said that the botnet claim was not true and that his efforts served only to raise awareness about the risks of leaving printers exposed to the internet.

Stackoverflowin claims to be a high school student from the U.K. who is interested in security research. He said that for the most part he simply sent print jobs using the Line Printer Daemon (LPD), the Internet Printing Protocol (IPP) and the RAW protocol on communications port 9100 to printers that didn’t require authentication.

To read this article in full or to leave a comment, please click here

Read More