Tip of the week: Extend your license for less
If you already have a Kaspersky security solution, you can extend the license at a discount!
Read MoreRSS Reader for Computer Security Articles
If you already have a Kaspersky security solution, you can extend the license at a discount!
Read More
A new voting system promises to avoid unnecessary recounts—and prove when they’re necessary, too. The post For the Next Election, Don’t Recount the Vote. Encrypt It appeared first on WIRED.
Read More
Can the nascent consumer quantum computing industry help cybersecurity firms with optimization problems like threat detection? The post Quantum Computers Versus Hackers, Round One. Fight! appeared first on WIRED.
Read More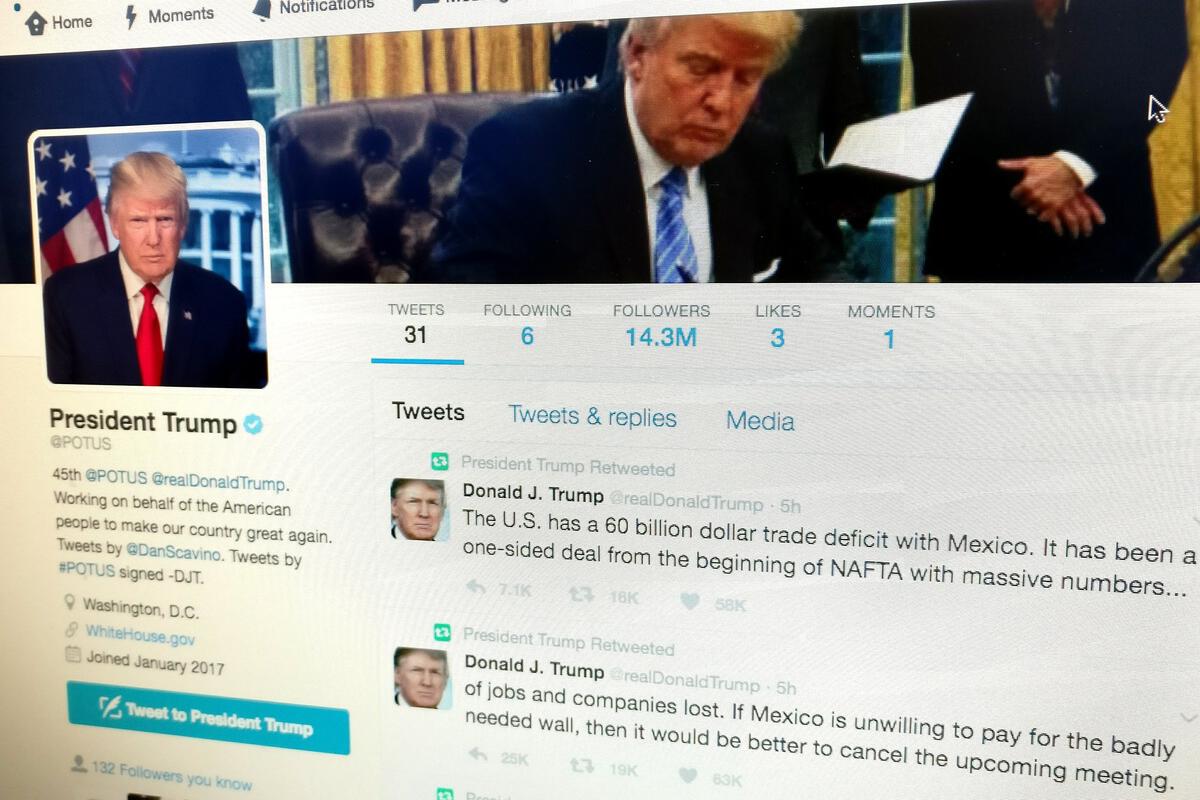
Several recent incidents involving U.S. President Donald Trump’s administration can teach users something about IT security — particularly about Twitter and what not to do with it.
It turns out that several White House-related Twitter accounts — including the president’s official account, @POTUS — until recently were revealing sensitive information that hackers might be able to exploit.
The problem revolves around the service’s password reset function. If the account holder doesn’t take certain steps to secure it, Twitter exposes information that anyone with the right skills can use to uncover what email address — in redacted form — was used to secure a Twitter account.
To read this article in full or to leave a comment, please click here
This credit union updates its online banking website, so a pilot fish with accounts there updates all her family’s accounts.
“The new feature was security questions,” says fish. “I didn’t like the three that were given, so I did the drop-down to see more questions. I chose my three new questions and wrote down the answers so the spouse knew what they were.”
But the first time he tries it, he blows the password. Fish has to go through the whole process of recreating the account setup.
Next time he tries, fish has to go through the entire process again — but this time she prints out screen captures of the questions she chose, and writes the answers on them.
To read this article in full or to leave a comment, please click here
The Gmail phishing attack is reportedly so effective that it tricks even technical users, but it may be just the tip of the iceberg. We’re seeing similarly simple but clever social engineering tactics using PDF attachments. These deceitful PDF attachments are being used in email phishing attacks that attempt to steal your email credentials. Apparently, the…
Read More
Starting Feb. 13, Google will no longer allow JavaScript attachments on its Gmail service, killing one of the main methods of malware distribution over the past two years.
Users will no longer be able to attach .JS files to emails in Gmail, regardless of whether they attach them directly or they include them in archives like .gz, .bz2, .zip or .tgz. For those rare cases when such files need to be shared via email, users can upload them to a storage service like Google Drive and then share the link.
The .JS file extension will be added an existing list of other banned file attachments that includes: .ADE, .ADP, .BAT, .CHM, .CMD, .COM, .CPL, .EXE, .HTA, .INS, .ISP, .JAR, .JSE, .LIB, .LNK, .MDE, .MSC, .MSP, .MST, .PIF, .SCR, .SCT, .SHB, .SYS, .VB, .VBE, .VBS, .VXD, .WSC, .WSF and .WSH. Most of these file types have long been abused by cybercriminals to send malware via email.
To read this article in full or to leave a comment, please click here