Credit to Author: Malwarebytes Labs| Date: Mon, 12 Feb 2018 17:00:10 +0000
We bring you an overview of what happened in cybersecurity during the last week, including new developments in drive-by cryptomining, including Mac and Android miners, and yet another abusing the fact that Deepfakes content was banned from most major networks.
Credit to Author: Microsoft Secure Blog Staff| Date: Mon, 12 Feb 2018 17:00:14 +0000
Many organizations are undergoing a digital transformation that leverages a mix of cloud and on-premises assets to increase business efficiency and growth. While increased dependence on technology is necessary for this transformation, and to position the business for success, it does pose risks from security threats. An organization cannot afford to wait until after users
Credit to Author: Michael Xie| Date: Mon, 12 Feb 2018 13:45:59 +0000
In the intensifying rush to develop and deploy network security strategies that can handle the drastic increase of today’s cyberthreats, I fear that many organizations are falling into a trap that is already having far-ranging consequences. Rather than approaching the admittedly intense challenges of security with the methodical approach and longview perspective of managers of complex data centers, they are behaving like harried consumers—reactively buying a specific, standalone solution to tamp down a challenge or crisis as it emerges.
Credit to Author: Ronen Shpirer| Date: Mon, 12 Feb 2018 09:00:59 +0000
Fortinet’s booth presence and education efforts at Mobile World Congress reinforce that commitment by exploring three themes: Agile Security for Mobile Cloud Services Delivery, Advanced Security for Industrial Operation Technology (OT) and the Internet of Things (IoT), and Mobile Security/Managed Security Services.
Credit to Author: Woody Leonhard| Date: Mon, 12 Feb 2018 06:44:00 -0800
January 2018 will go down in history as one of the worst patching months in Microsoft’s very checkered history. That isn’t an isolated muck-up. It’s a harbinger. We had a couple of really bad months in 2017 — February and November come immediately to mind — but an unconscionable number of patches left bricked machines and busted programs in their wake.
Credit to Author: Matthew Phillion| Date: Mon, 12 Feb 2018 15:16:19 +0000
It’s a huge honor to be named on the annual CRN Channel Chiefs list.<img src=”http://feeds.feedburner.com/~r/sophos/dgdY/~4/IbzN7jDg33c” height=”1″ width=”1″ alt=””/>
Credit to Author: BrianKrebs| Date: Mon, 12 Feb 2018 13:41:53 +0000
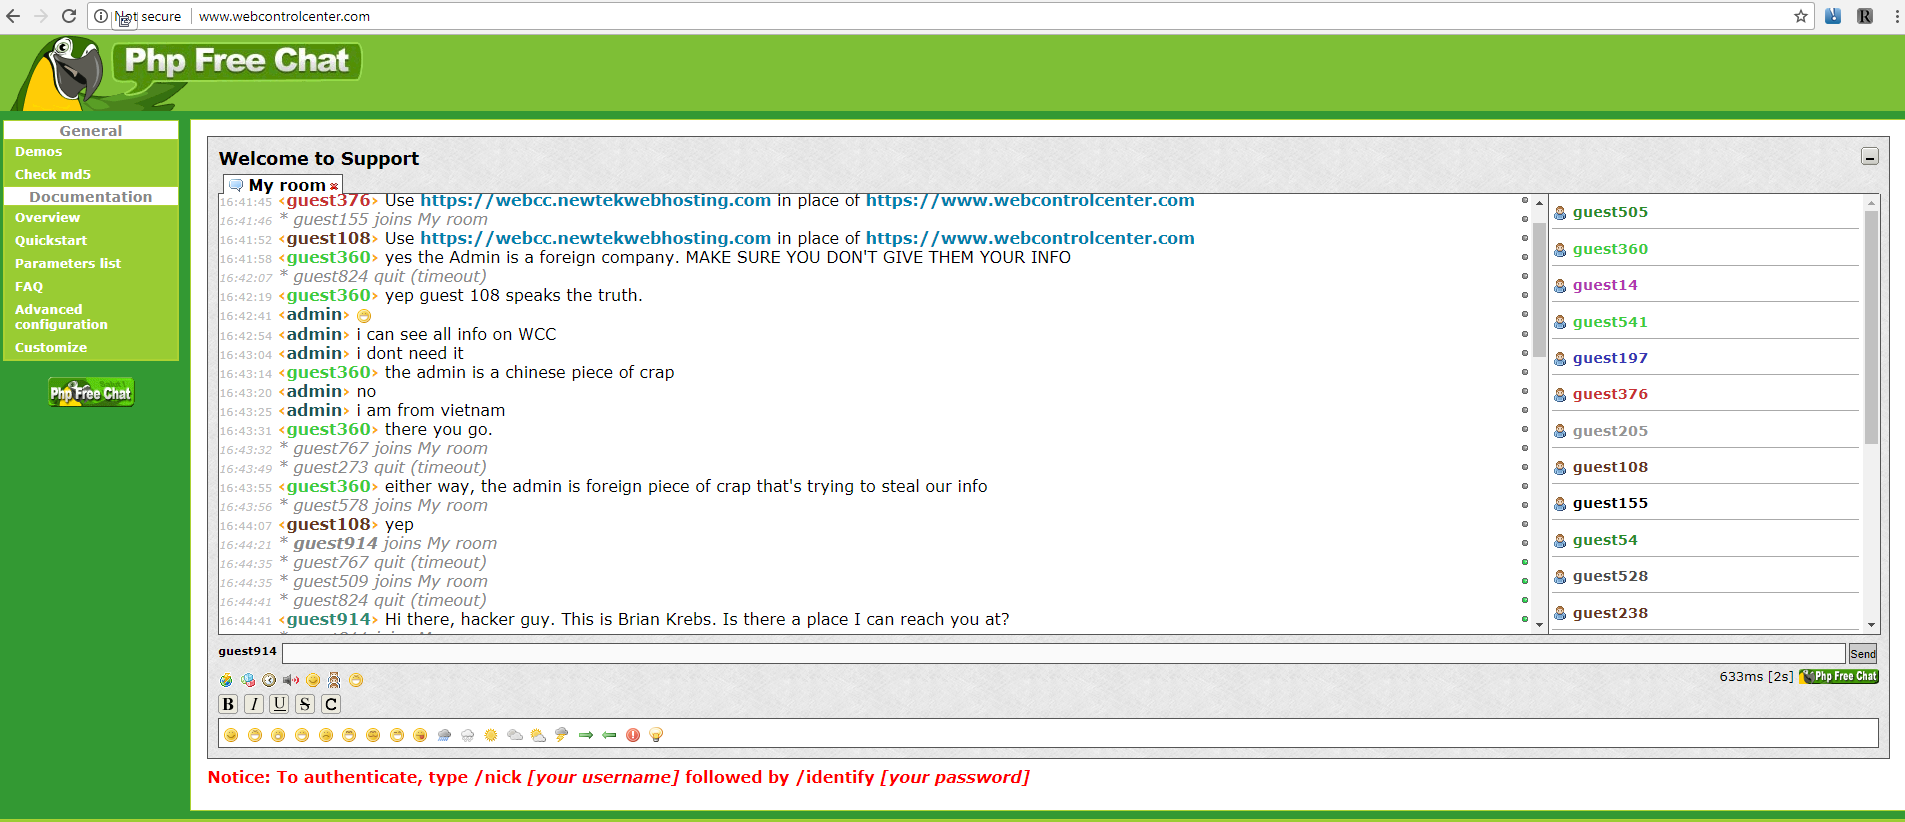
Newtek Business Services Corp. [NASDAQ:NEWT], a Web services conglomerate that operates more than 100,000 business Web sites and some 40,000 managed technology accounts, had several of its core domain names stolen over the weekend. The theft shut off email and stranded Web sites for many of Newtek’s customers. An email blast Newtek sent to customers late Saturday evening made no mention of a breach or incident, saying only that the company was changing domains due to “increased” security. A copy of that message can be read here (PDF). In reality, three of their core domains were hijacked by a Vietnamese hacker, who replaced the login page many Newtek customers used to remotely manage their Web sites (webcontrolcenter[dot]com) with a live Web chat service. As a result, Newtek customers seeking answers to why their Web sites no longer resolved correctly ended up chatting with the hijacker instead.