Author: admin

ComputerWorldIndependent

Trump’s unsecure Android phone highlights common security dilemma
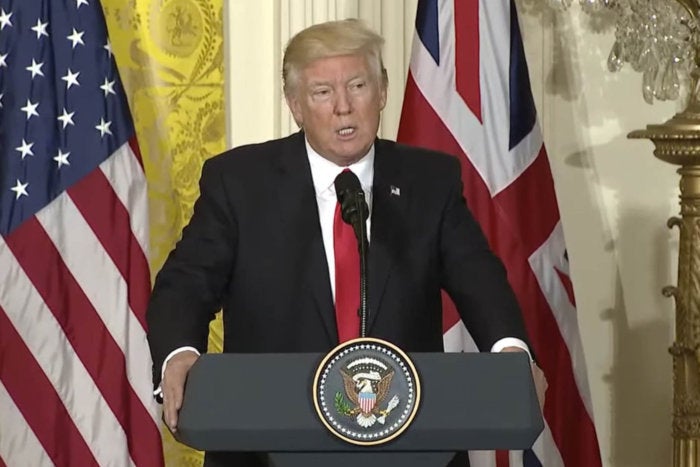
If President Donald Trump is still using his personal, unsecured Android smartphone, as reported, he is surely creating bucketsful of worry for White House communications security staff.

As CIOs and Chief Information Security Officers already know, any organization can install strong security technology into a network or a smartphone, only to be defeated if end users don’t use it or follow safe cyber practices.

“The most vulnerable parts of communications are the people, and if they aren’t taking precautions, problems exist,” said Chris Perry, chief operating officer for Secured Communications, a provider of encrypted VPNs for mobile devices used by governments and companies.

To read this article in full or to leave a comment, please click here

Read More
FortinetSecurity

CISO Customer Panel – Accelerate 2017


I recently wrote about the general sessions held on the first day of Fortinet's Accelerate 2017. There was so much great information presented that I couldn’t do justice to it in the general overview I posted of the morning’s events. So I wanted to take a few minutes and provide some deeper information around one of the best sessions of the day – the customer panel.

Read More
ComputerWorldIndependent

Five arrested for hacking into ATMs and stealing $3.2 million

Law enforcement authorities from Europe and Asia have arrested five members of an international cybercriminal group that specialized in hacking into automated teller machine (ATMs).

The investigation began in early 2016, according to Europol. Three suspects were arrested in Taiwan, one in Romania, and one in Belarus. Most of them had multiple citizenships and could travel easily between countries, the agency said Friday.

Hacking into ATMs to steal money is nothing new, and there are malware programs built specifically for such machines that allow criminals to withdraw money using hidden commands.

To infect ATMs with such malware most attackers either receive help from bank insiders or buy service keys that can be used to open the front panels of ATMs and access their communications ports.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Trump, May agree to take on ISIS in cyberspace

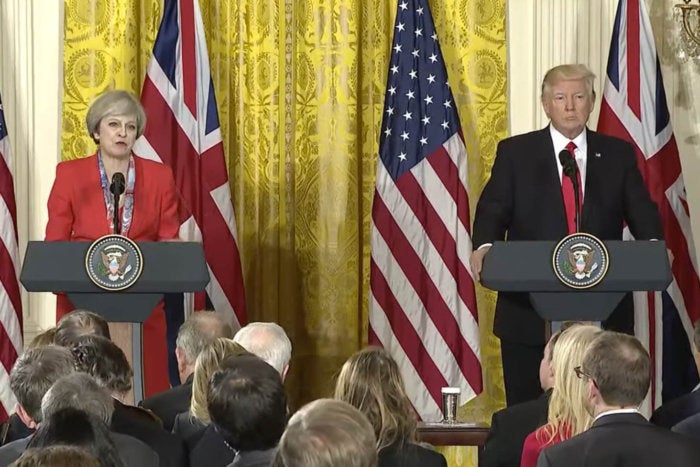
The U.K. and U.S. are planning to work more closely to combat the spread of extreme Islamist ideology in cyberspace, British Prime Minister Theresa May said on Friday.

May was speaking at a White House news conference, alongside U.S. President Donald Trump, held to outline the results of talks between the two leaders. May is in Washington as the first foreign head of state to meet Trump.

She noted the conventional military fight against ISIS is working and the group is losing territory but noted the two countries “need to redouble our efforts.”

“Today we’re discussing how we can do this by deepening intelligence and security cooperation and critically, by stepping up our efforts to counter Daesh in cyberspace,” she said, using an alternate name for the terrorist group.

To read this article in full or to leave a comment, please click here
Read More
FortinetSecurity

Multiple XSS Vulnerabilities Discovered In IBM Infosphere BigInsights


Summary Last year, I discovered and reported two Cross-Site Scripting (XSS) vulnerabilities in IBM’s Infosphere BigInsights. This week, IBM released a security bulletin which contains the fix for these vulnerabilities. CVE numbers CVE-2016-2924 and CVE-2016-2992 are assigned to them respectively. InfoSphere BigInsights is an analytics platform for analyzing massive volumes of unconventional data in its native format. The software enables advanced analysis and modeling of diverse data, and supports structured, semi-structured, and unstructured…

Read More
ComputerWorldIndependent

Cisco starts patching critical flaw in WebEx browser extension

Cisco Systems has started to patch a critical vulnerability in its WebEx collaboration and conferencing browser extension that could allow attackers to remotely execute malicious code on computers.

The company released a patched version of the extension — 1.0.7 — for Google Chrome on Thursday and is working on similar patches for the Internet Explorer and Mozilla Firefox versions.

The vulnerability was found by Google security researcher Tavis Ormandy and stemmed from the fact that the WebEx extension exposed functionality to any website that had “cwcsf-nativemsg-iframe-43c85c0d-d633-af5e-c056-32dc7efc570b.html” in its URL or inside an iframe. Some of that WebEx functionality allowed for the execution of arbitrary code on computers.

To read this article in full or to leave a comment, please click here

Read More