Independent

ComputerWorldIndependent

Get TotalAV Essential AntiVirus for $19.99 (80% off)

Credit to Author: DealPost Team| Date: Thu, 07 Feb 2019 11:11:00 -0800

The term “computer virus” calls to mind imagery of pathogenic creepy-crawlies bringing down a device’s operating system, their flagella wriggling as they multiply into hordes that infiltrate its chips and wires. And while it’s true that our computers can be infected with literal biological bacteria like staphylococci, per Science Illustrated, the threat of malicious codes and programs intent on corrupting data and files looms far larger: According to a recent study from the University of Maryland’s Clark School of Engineering, attacks on computers with internet access is virtually ceaseless, with an incident occurring every 39 seconds on average, affecting a third of Americans every year.
To read this article in full, please click here

Read More
ComputerWorldIndependent

Why Apple is disabling Safari’s Do Not Track feature

Credit to Author: Jonny Evans| Date: Thu, 07 Feb 2019 03:34:00 -0800

Apple takes privacy very seriously. It takes its leadership in that care seriously, and getting rid of the voluntary ‘Do Not Track’ setting in its Safari browser is the right decision.

Why disabling Safari’s Do Not Track feature is the right thing to do

Apple introduced support for Do Not Track (DNT) in iOS 7, but removed the feature in Safari 12.1.

The problem with DNT is that the signal it sends to websites, analytics firms, plug-in makers and ad networks is a voluntary request, and can be ignored.

To read this article in full, please click here

Read More
ComputerWorldIndependent

Throwback Thursday: Pick a card, any card …

Credit to Author: Sharky| Date: Thu, 07 Feb 2019 03:00:00 -0800

This conglomerate is structured as several smaller companies, with a big central IT organization plus individual IT groups in some of the companies, reports an IT pilot fish there.

“An IT staffer from one of the companies loaded a password cracker and proceeded to crack the Windows NT servers,” fish says. “He sent out emails bragging about how insecure NT was and giving the NT team a hard time.”

Fish isn’t on the NT team, but he and his security co-workers decide to strike back on behalf of their colleagues — and they do it through the central IT audit group, to make sure it’s all above board.

First, they supply the audit people with a list of more than 100 Unix servers, and get them to pick a server at random. Amazingly, the audit group picks the only server on the list that belongs to the company where the NT attack originated.

To read this article in full, please click here

Read More
IndependentKrebs

More Alleged SIM Swappers Face Justice

Credit to Author: BrianKrebs| Date: Wed, 06 Feb 2019 05:50:07 +0000

Prosecutors in Northern California have charged two men with using unauthorized SIM swaps to steal and extort money from victims. One of the individuals charged allegedly used a hacker nickname belonging to a key figure in the underground who’s built a solid reputation hijacking mobile phone numbers for profit. According to indictments unsealed this week, Tucson, Ariz. resident Ahmad Wagaafe Hared and Matthew Gene Ditman of Las Vegas were part of a group that specialized in tricking or bribing representatives at the major wireless providers into giving them control over phone numbers belonging to people they later targeted for extortion and theft.

Read More
IndependentKrebs

Crooks Continue to Exploit GoDaddy Hole

Credit to Author: BrianKrebs| Date: Mon, 04 Feb 2019 19:12:25 +0000

Godaddy.com, the world’s largest domain name registrar, recently addressed an authentication weakness that cybercriminals were using to blast out spam through legitimate, dormant domains. But several more recent malware spam campaigns suggest GoDaddy’s fix hasn’t gone far enough, and that scammers likely still have a sizable arsenal of hijacked GoDaddy domains at their disposal.

Read More
ComputerWorldIndependent

The January Windows and Office patches are good to go

Credit to Author: Woody Leonhard| Date: Fri, 01 Feb 2019 09:15:00 -0800

Compared to some months last year, January has been a Microsoft patching cakewalk. We had several rounds of close calls and missed calls, as I posted earlier this week, but almost everything is cleared up.

We’ve seen a few more problems raise their ugly heads in the past few days:

  • Microsoft has confirmed that the latest version of Office Click-to-Run (which you’re likely using if you have Office 365) makes the conversation window disappear in Skype for Business 2016.
  • The Windows 8.1 Monthly Rollup, KB 4480963, breaks the Live Migration feature on older AMD Opteron machines. We’re still waiting for confirmation on that one.
  • Citrix confirms (but Microsoft hasn’t acknowledged) that the latest Win10 1803 cumulative update, KB 4480976, causes page file problems when the page file isn’t sitting on C:. More details on Tenforums.

Those are typical Microsoft edge-use bugs: They don’t affect many people, but if you’re one of the stuckees, you’re up the ol’ creek.

To read this article in full, please click here

Read More
IndependentKrebs

250 Webstresser Users to Face Legal Action

Credit to Author: BrianKrebs| Date: Fri, 01 Feb 2019 13:43:59 +0000

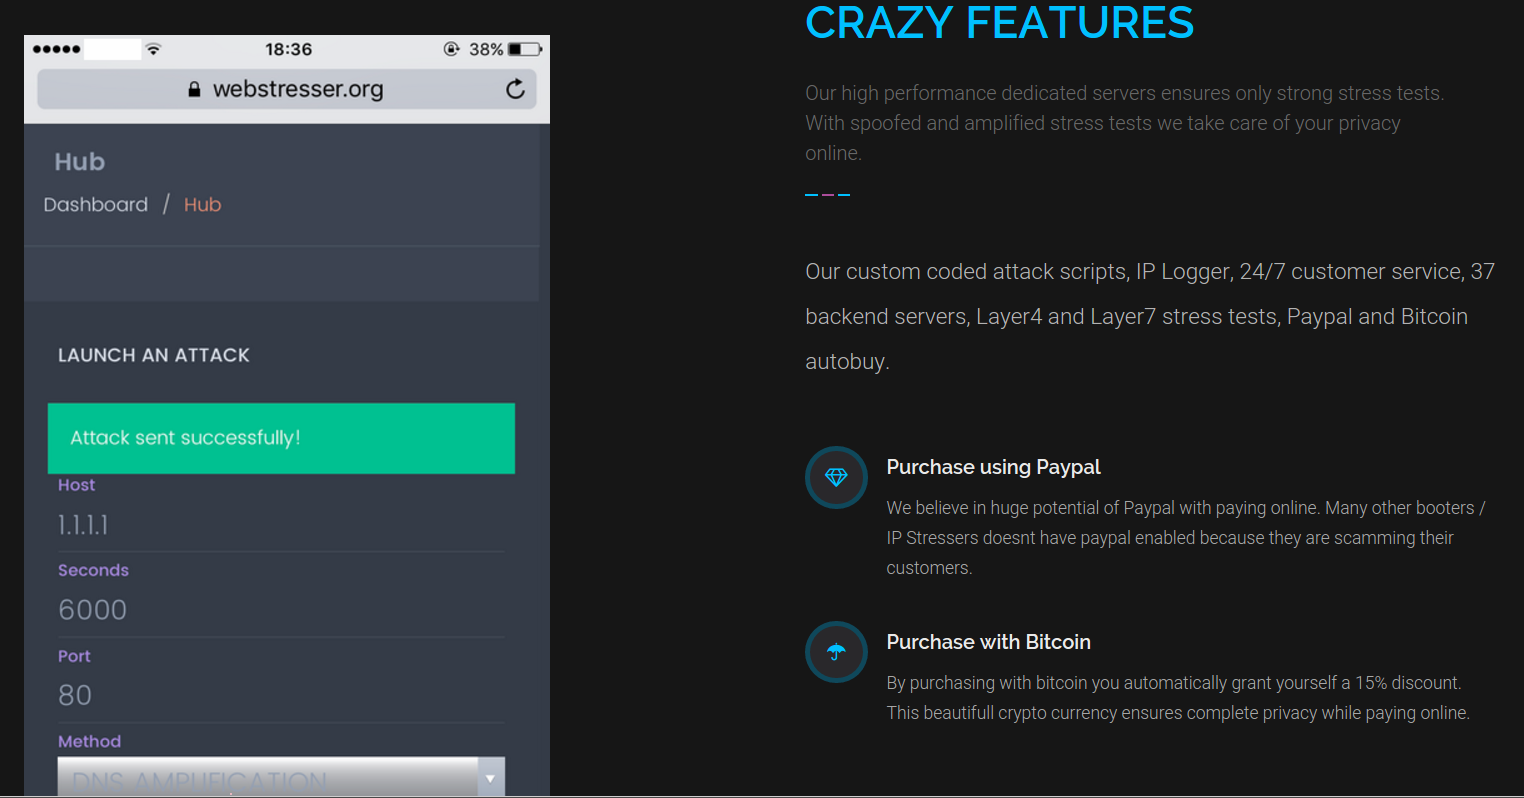
More than 250 customers of a popular and powerful online attack-for-hire service that was dismantled by authorities in 2018 are expected to face legal action for the damage they caused, according to Europol, the European Union’s law enforcement agency. In April 2018, investigators in the U.S., U.K. and the Netherlands took down attack-for-hire service WebStresser[.]org and arrested its alleged administrators. Prior to the takedown, the service had more than 151,000 registered users and was responsible for launching some four million attacks over three years. Now, those same authorities are targeting people who paid the service to conduct attacks.

Read More