Tech luminaries we lost in 2018
Credit to Author: Ken Gagne| Date: Thu, 27 Dec 2018 03:00:00 -0800

The top 10 stories of 2018: Blockchain rises, open source reigns, trust wanes
Credit to Author: Marc Ferranti| Date: Wed, 26 Dec 2018 03:00:00 -0800
Serial Swatter and Stalker Mir Islam Arrested for Allegedly Dumping Body in River
Credit to Author: BrianKrebs| Date: Sun, 23 Dec 2018 20:24:29 +0000
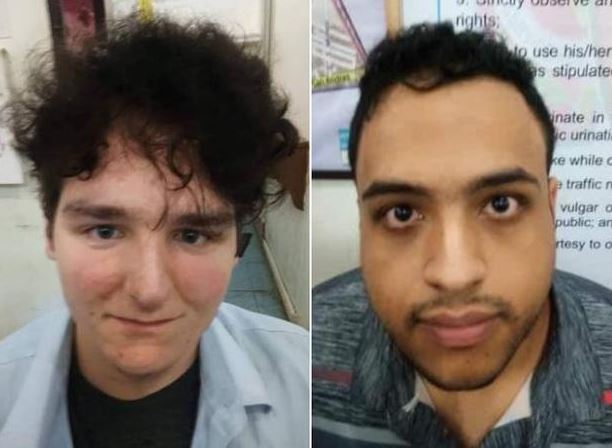
A 22-year-old man convicted of cyberstalking and carrying out numerous bomb threats and swatting attacks — including a 2013 swatting incident at my home — was arrested Sunday morning in the Philippines after allegedly helping a friend dump the body of a housemate into a local river.
Read MoreMicrosoft Patch Alert: Mystery patches for IE and Outlook 2013 leave many questions, few answers
Credit to Author: Woody Leonhard| Date: Fri, 21 Dec 2018 08:21:00 -0800
Just when you’re ready to settle in for some egg and nog and whatever may accompany, Windows starts throwing poison frog darts. This month, a fairly boring patching regiment has turned topsy turvey with an unexplained emergency patch for Internet Explorer (you know, the browser nobody uses), combined with an Outlook 2013 patch that doesn’t pass the smell test.
Mysterious bug fix for IE
Microsoft set off the shower of firecrackers on Dec. 19 when it released a bevy of patches for Internet Explorer:
Win10 1809– KB 4483235 – build 17763.195
Microsoft delivers emergency patch for under-attack IE
Credit to Author: Gregg Keizer| Date: Wed, 19 Dec 2018 17:26:00 -0800
Microsoft rarely mentions Internet Explorer (IE) anymore, but when it does, it usually means bad news.
So it was Wednesday, when Microsoft issued a rare emergency security update to plug a critical vulnerability in the still-supported IE9, IE10 and IE11. The flaw was reported to Microsoft by Google security engineer Clement Lecigne.
According to Microsoft, attackers are already exploiting the vulnerability, making it a classic “zero-day” bug. Because of that, the company released a fix before the next round of security updates scheduled for Jan. 8.
Feds Charge Three in Mass Seizure of Attack-for-hire Services
Credit to Author: BrianKrebs| Date: Thu, 20 Dec 2018 19:11:43 +0000
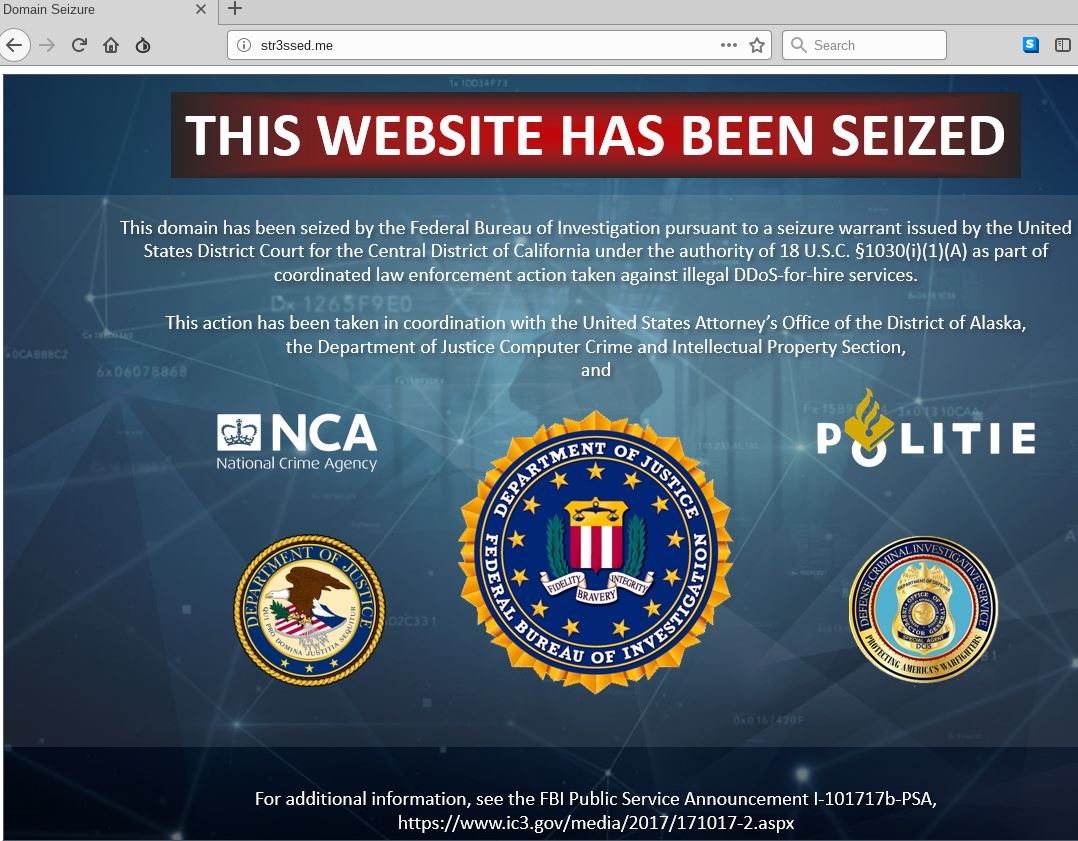
Authorities in the United States this week brought criminal hacking charges against three men as part of an unprecedented, international takedown targeting 15 different “booter” or “stresser” sites — attack-for-hire services that helped paying customers launch tens of thousands of digital sieges capable of knocking Web sites and entire network providers offline.
Read MoreMicrosoft Issues Emergency Fix for IE Zero Day
Credit to Author: BrianKrebs| Date: Wed, 19 Dec 2018 21:01:27 +0000
Microsoft today released an emergency software patch to plug a critical security hole in its Internet Explorer (IE) Web browser that attackers are already using to break into Windows computers.
Read MoreA Chief Security Concern for Executive Teams
Credit to Author: BrianKrebs| Date: Tue, 18 Dec 2018 21:23:10 +0000
Virtually all companies like to say they take their customers’ privacy and security seriously, make it a top priority, blah blah. But you’d be forgiven if you couldn’t tell this by studying the executive leadership page of each company’s Web site. That’s because very few of the world’s biggest companies list any security executives in their highest ranks. Even among top tech firms, less than half list a chief technology officer (CTO). This post explores some reasons why this is the case, and why it can’t change fast enough. KrebsOnSecurity reviewed the Web sites for the global top 100 companies by market value, and found just five percent of top 100 firms listed a chief information security officer (CISO) or chief security officer (CSO). Only a little more than a third even listed a CTO in their executive leadership pages.
Read More