Nathan Freitas, who heads The Guardian Project, talks with host Steve Ragan and senior writer J.M. Porup about the group's easy-to-use secure apps, open-source software libraries, and customized mobile devices being used around the world.
Credit to Author: Lucas Mearian| Date: Mon, 12 Feb 2018 03:08:00 -0800
The need to manage applications on unmanaged devices owned by employees or contractors is driving adoption of stand-alone mobile app management (MAM) software and services, according to a new Gartner report.
By 2021, 60% of mobile apps being used in the enterprise will rely on at least one app-level management control, whether on managed or unmanaged devices, Gartner’s Market Guide for Mobile Application Management said.
Unlike MAM tools that are part of a larger enterprise mobility management (EMM) suite, the use of stand-alone MAM licensing offers lower per-user cost and can be attractive for companies only requiring app management, Gartner said. For other firms, EMM provides the advantage of a single console and policy set.
Credit to Author: SSD / Noam Rathaus| Date: Sun, 11 Feb 2018 07:06:24 +0000
The following advisory describes one (1) vulnerability found in CloudMe. CloudMe is “a file storage service operated by CloudMe AB that offers cloud storage, file synchronization and client software. It features a blue folder that appears on all devices with the same content, all files are synchronized between devices.” The vulnerability found is a buffer … Continue reading SSD Advisory – CloudMe Unauthenticated Remote Buffer Overflow
Credit to Author: SSD / Maor Schwartz| Date: Sun, 11 Feb 2018 06:10:03 +0000
Vulnerabilities Summary The following advisory describes two (2) vulnerabilities found in Cisco RV132W Wireless N VPN version 1.0.1.8 The Cisco RV132W Wireless-N ADSL2+ VPN Router is “easy to use, set up, and deploy. This flexible router offers great performance and is suited for small or home offices (SOHO) and smaller deployments.” The vulnerabilities found are: … Continue reading SSD Advisory – Hack2Win – Cisco RV132W Multiple Vulnerabilities
Credit to Author: Lucas Mearian| Date: Fri, 09 Feb 2018 03:11:00 -0800
Last year’s blockchain pilot projects are rapidly becoming this year’s live implementations in a variety of industries, and even sectors that have until now been vexed by the distributed ledger technology are following suit.
Case in point: Governments, which are moving to regulate blockchain technology and the cryptocurrencies it underpins.
Cryptocurrencies such as bitcoin that live in open networks, have so far inhabited a regulatory gray area, because there’s no way for a central authority to track users. The distributed ledgers, however, are useful because they can enable cross-border transactions over peer-to-peer networks in real time, anywhere in the world – without a central governing authority such as a bank or credit card company.
Credit to Author: SSD / Maor Schwartz| Date: Thu, 08 Feb 2018 08:02:43 +0000
Vulnerabilities summary The following advisory describes three (3) vulnerabilities found in the following vendors: Lorex StarVedia Eminent Kraun The vulnerabilities found: Hard-coded credentials Remote command injection (2) It is possible to chain the vulnerabilities and to achieve unauthenticated remote command execution. Credit An independent security researcher, Robert Kugler (https://www.s3cur3.it), has reported this vulnerabilities to Beyond … Continue reading SSD Advisory – Multiple IoT Vendors – Multiple Vulnerabilities
Credit to Author: BrianKrebs| Date: Thu, 08 Feb 2018 18:04:22 +0000
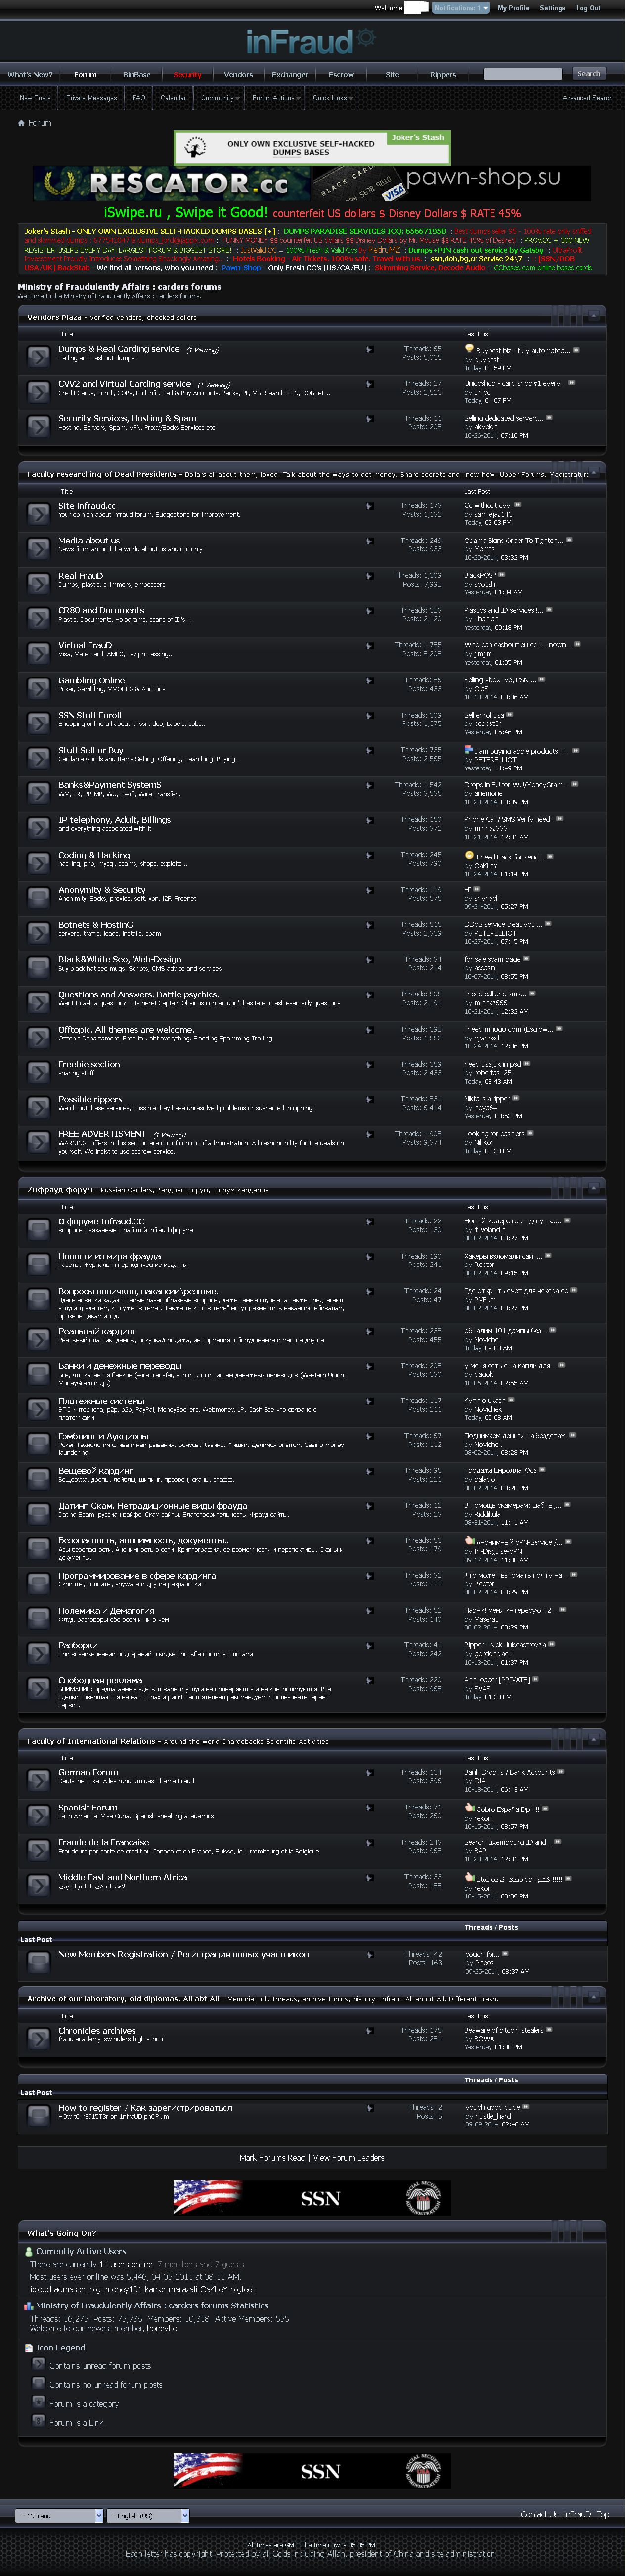
The U.S. Justice Department announced charges on Wednesday against three dozen individuals thought to be key members of ‘Infraud,” a long-running cybercrime forum that federal prosecutors say cost consumers more than a half billion dollars. In conjunction with the forum takedown, 13 alleged Infraud members from the United States and six other countries were arrested. Started in October 2010, Infraud was short for “In Fraud We Trust,” and collectively the forum referred to itself as the “Ministry of Fraudulently [sic] Affairs.” As a mostly English-language fraud forum, Infraud attracted nearly 11,000 members from around the globe who sold, traded and bought everything from stolen identities and credit card accounts to ATM skimmers, botnet hosting and malicious software.