Independent

IndependentSecuriteam

SSD Advisory – Xiaomi Air Purifier 2 Firmware Update Process Vulnerability

Credit to Author: SSD / Maor Schwartz| Date: Sun, 14 May 2017 13:06:52 +0000

Vulnerability Summary The following advisory describes an Firmware Update Process Vulnerability found in Xiaomi Air Purifier 2. Mi Air Purifier is a High performance smart air purifier (IoT) that can be controlled remotely. According to the manufacture (Xiaomi) “Monitor your home air quality in real time from absolutely anywhere when you sync with the Mi … Continue reading SSD Advisory – Xiaomi Air Purifier 2 Firmware Update Process Vulnerability

Read More
ComputerWorldIndependent

Patching Windows XP against WannaCry ransomware

Credit to Author: Michael Horowitz| Date: Sun, 14 May 2017 12:56:00 -0700

Microsoft just released a patch for Windows XP that fixes a file sharing flaw being exploited by the WannaCry ransomware. Here’s how to install it. 

You can download some versions of the patch using links at the bottom of this May 12th  Microsoft article: Customer Guidance for WannaCrypt attacks. The full list of patch variants, including languages other than English, is in the Windows Catalog, just search for KB4012598. Windows Update does not work on XP.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Microsoft issues first Windows XP patch in 3 years to stymie 'WannaCrypt'

Credit to Author: Gregg Keizer| Date: Sun, 14 May 2017 11:00:00 -0700

Microsoft on Friday took the unprecedented step of issuing patches for long-demoted versions of Windows, including Windows XP, to immunize PCs from fast-spreading ransomware that has crippled machines worldwide.

To stymie “WannaCrypt” attacks — which encrypted files on thousands of PCs used by the U.K.’s National Health Service (NHS), causing chaos in many hospitals — Microsoft published patches for Windows XP, Windows 8 and Windows Server 2003. All had been retired from support: Windows XP in April 2014, Windows 8 in June 2016, Windows Server in July 2015.

“We are taking the highly unusual step of providing a security update for all customers to protect Windows platforms that are in custom support only, including Windows XP, Windows 8, and Windows Server 2003,” said Phillip Misner, a principal security group manager at the Microsoft Security Response Center (MSRM), in a post to a company blog late Friday.

To read this article in full or to leave a comment, please click here

Read More
IndependentKrebs

Global ‘Wana’ Ransomware Outbreak Earned Perpetrators $26,000 So Far

Credit to Author: BrianKrebs| Date: Sat, 13 May 2017 20:10:43 +0000

As thousands of organizations work to contain and clean up the mess from this week’s devastating Wana ransomware attack, the fraudsters responsible for releasing the digital contagion are no doubt counting their earnings and congratulating themselves on a job well done. But according to a review of the Bitcoin addresses hard-coded into Wana, it appears the perpetrators of what’s being called the worst ransomware outbreak ever have made little more than USD $26,000 so far from the scam.

Read More
ComputerWorldIndependent

'Kill switch' helps slow the spread of WannaCry ransomware

Credit to Author: Michael Kan| Date: Fri, 12 May 2017 18:24:00 -0700

Friday’s unprecedented ransomware attack may have stopped spreading to new machines — at least briefly — thanks to a “kill switch” that a security researcher has activated.

The ransomware, called Wana Decryptor or WannaCry, has been found infecting machines across the globe. It works by exploiting a Windows vulnerability that the U.S. National Security Agency may have used for spying.

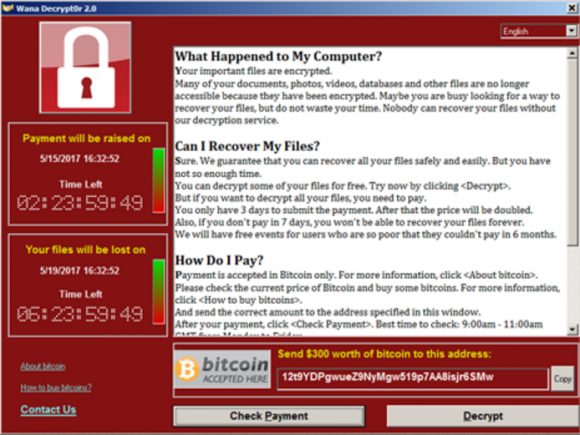
The malware encrypts data on a PC and shows users a note demanding $300 in bitcoin to have their data decrypted. Images of the ransom note have been circulating on Twitter. Security experts have detected tens of thousands of attacks, apparently spreading over LANs and the internet like a computer worm.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Microsoft posts PowerShell script that spawns pseudo security bulletins

Credit to Author: Gregg Keizer| Date: Fri, 12 May 2017 11:48:00 -0700

A Microsoft manager this week offered IT administrators a way to replicate — in a fashion — the security bulletins the company discarded last month.

“If you want a report summarizing today’s #MSRC security bulletins, here’s a script that uses the MSRC Portal API,” John Lambert, general manager of the Microsoft Threat Intelligence Center, said in a Tuesday message on Twitter.

Lambert’s tweet linked to code depository GitHub, where he posted a PowerShell script that polled data using a new API (application programming interface). Microsoft made the API available in November when it first announced that it planned to axe the security bulletins it had issued since at least 1998.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Ransomware attack spreads worldwide using alleged NSA exploit

Credit to Author: Michael Kan| Date: Fri, 12 May 2017 10:27:00 -0700

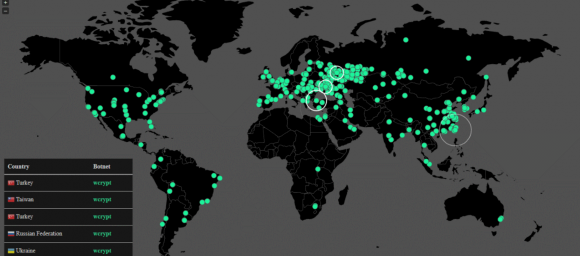
A ransomware attack appears to be spreading around the world, leveraging a hacking tool that may have come from the U.S. National Security Agency.

The ransomware, called Wanna Decryptor, struck hospitals at the U.K.’s National Health Service on Friday, taking down some of its network.

Spain’s computer response team, CCN-CERT, has also warned of  a “massive attack” from the ransomware strain, amid reports that local telecommunications firm Telefonica was hit.

To read this article in full or to leave a comment, please click here

Read More