Krebs

IndependentKrebs

Microsoft Patch Tuesday, February 2018 Edition
Credit to Author: BrianKrebs| Date: Tue, 13 Feb 2018 21:13:27 +0000

Microsoft today released a bevy of security updates to tackle more than 50 serious weaknesses in Windows, Internet Explorer/Edge, Microsoft Office and Adobe Flash Player, among other products. A good number of the patches issued today ship with Microsoft’s “critical” rating, meaning the problems they fix could be exploited remotely by miscreants or malware to seize complete control over vulnerable systems — with little or no help from users.

Read More
IndependentKrebs

Domain Theft Strands Thousands of Web Sites

Credit to Author: BrianKrebs| Date: Mon, 12 Feb 2018 13:41:53 +0000

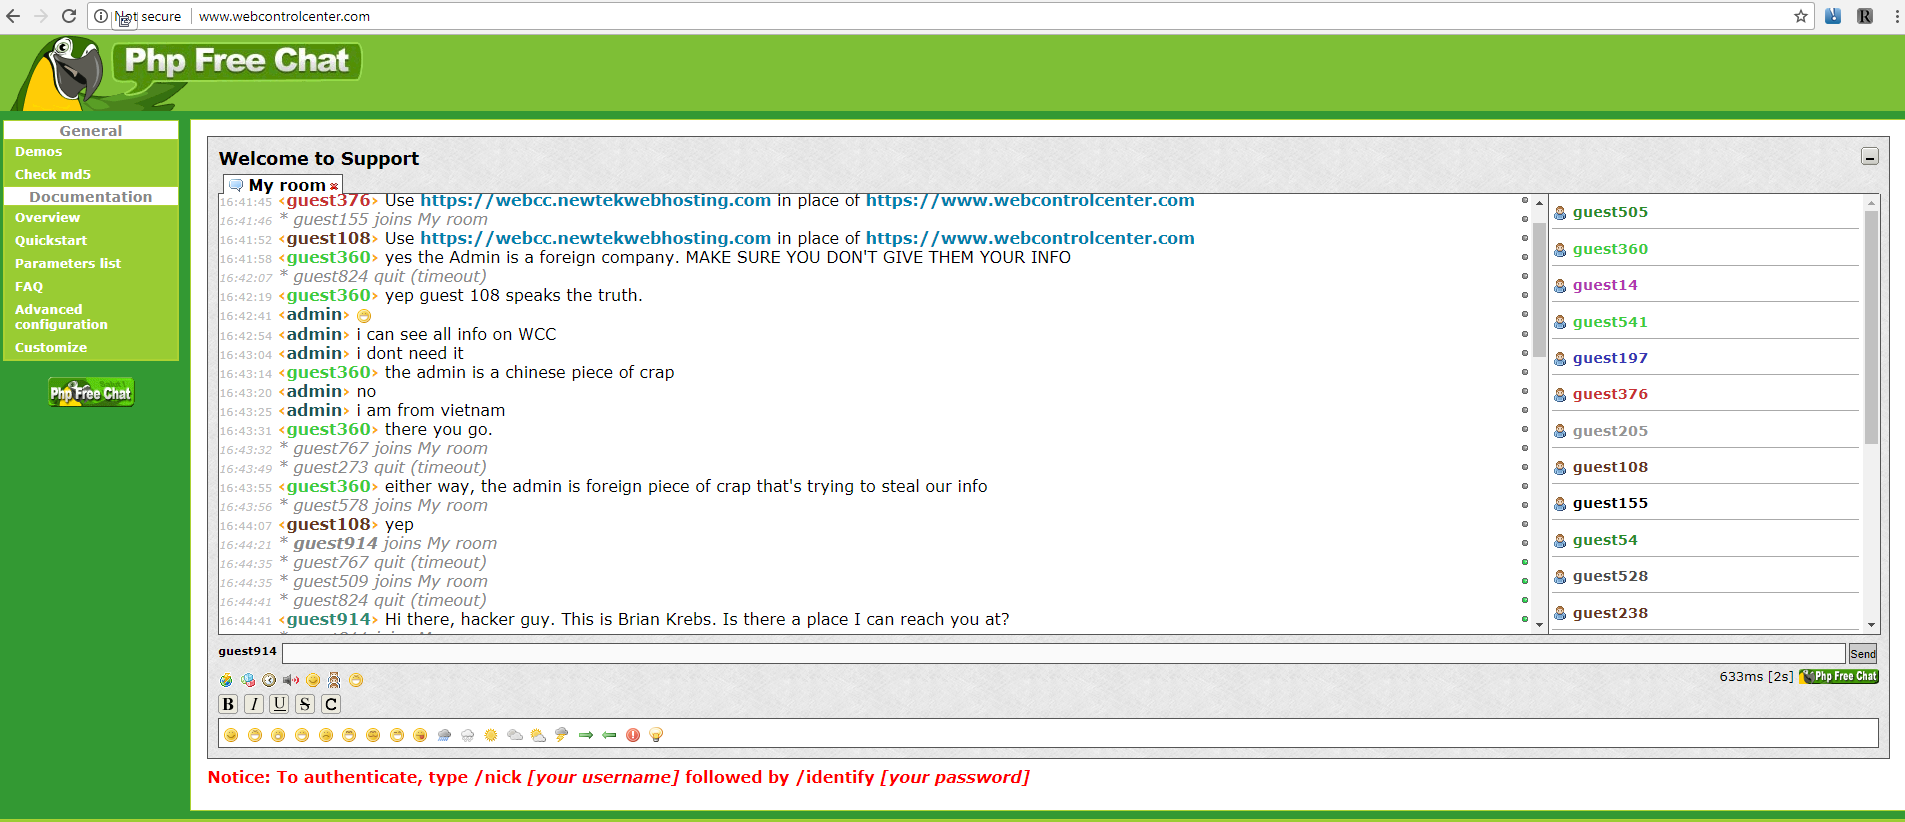
Newtek Business Services Corp. [NASDAQ:NEWT], a Web services conglomerate that operates more than 100,000 business Web sites and some 40,000 managed technology accounts, had several of its core domain names stolen over the weekend. The theft shut off email and stranded Web sites for many of Newtek’s customers. An email blast Newtek sent to customers late Saturday evening made no mention of a breach or incident, saying only that the company was changing domains due to “increased” security. A copy of that message can be read here (PDF). In reality, three of their core domains were hijacked by a Vietnamese hacker, who replaced the login page many Newtek customers used to remotely manage their Web sites (webcontrolcenter[dot]com) with a live Web chat service. As a result, Newtek customers seeking answers to why their Web sites no longer resolved correctly ended up chatting with the hijacker instead.

Read More
IndependentKrebs

U.S. Arrests 13, Charges 36 in ‘Infraud’ Cybercrime Forum Bust

Credit to Author: BrianKrebs| Date: Thu, 08 Feb 2018 18:04:22 +0000

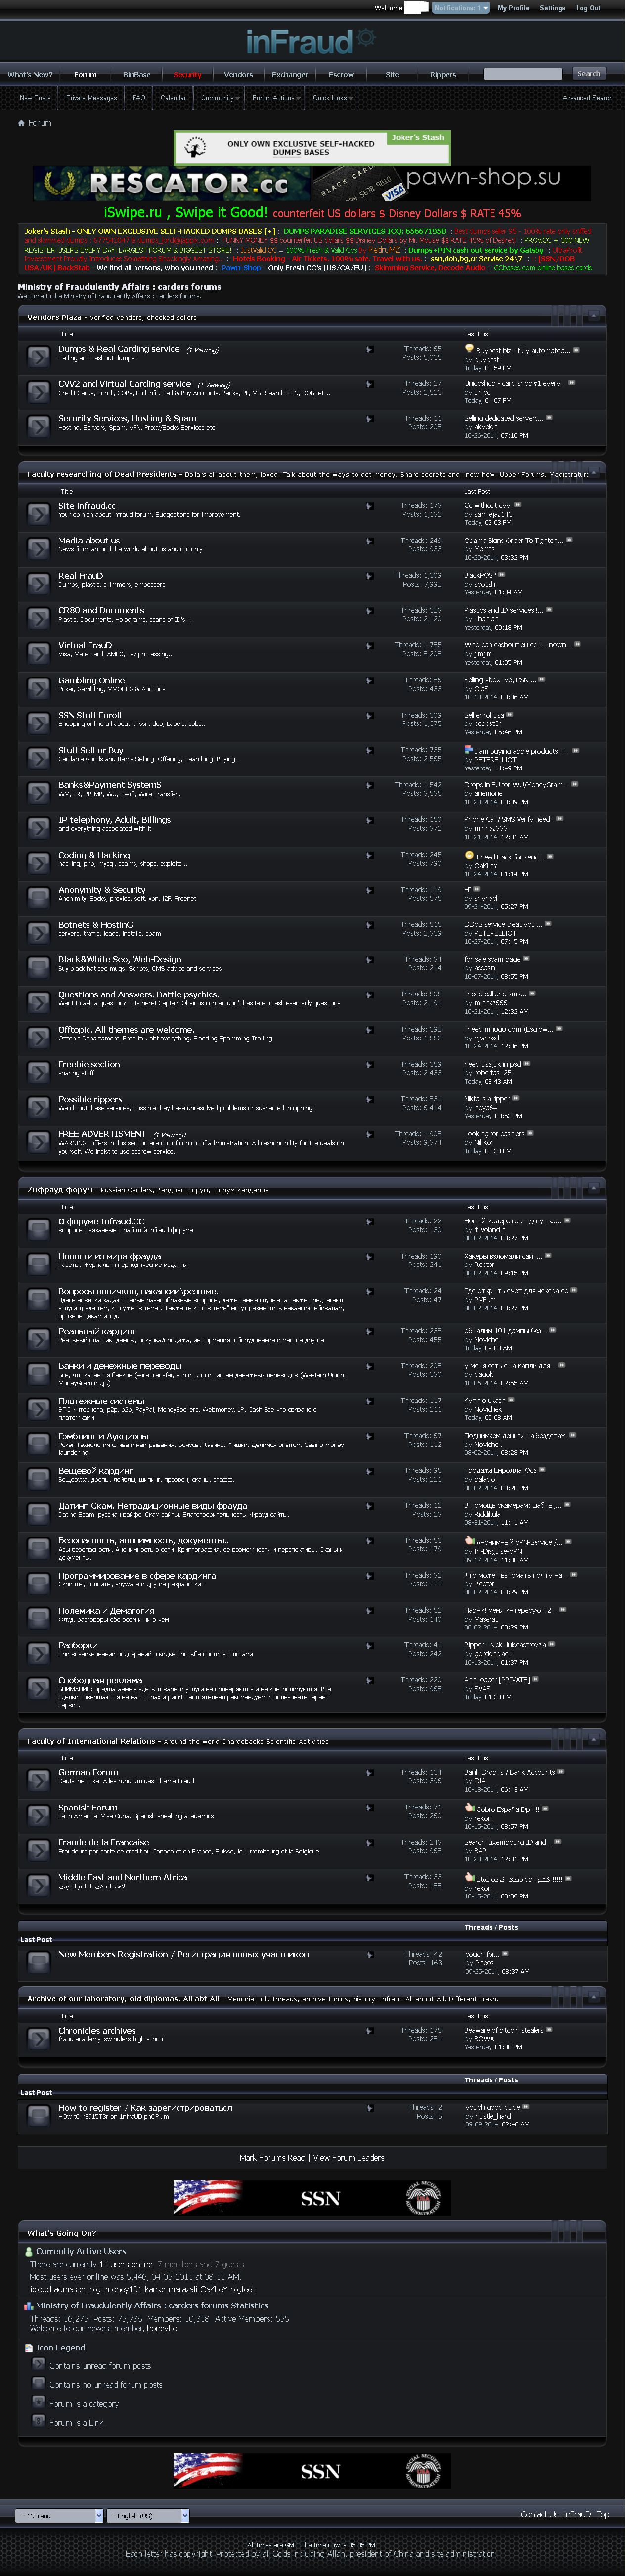
The U.S. Justice Department announced charges on Wednesday against three dozen individuals thought to be key members of ‘Infraud,” a long-running cybercrime forum that federal prosecutors say cost consumers more than a half billion dollars. In conjunction with the forum takedown, 13 alleged Infraud members from the United States and six other countries were arrested. Started in October 2010, Infraud was short for “In Fraud We Trust,” and collectively the forum referred to itself as the “Ministry of Fraudulently [sic] Affairs.” As a mostly English-language fraud forum, Infraud attracted nearly 11,000 members from around the globe who sold, traded and bought everything from stolen identities and credit card accounts to ATM skimmers, botnet hosting and malicious software.

Read More
IndependentKrebs

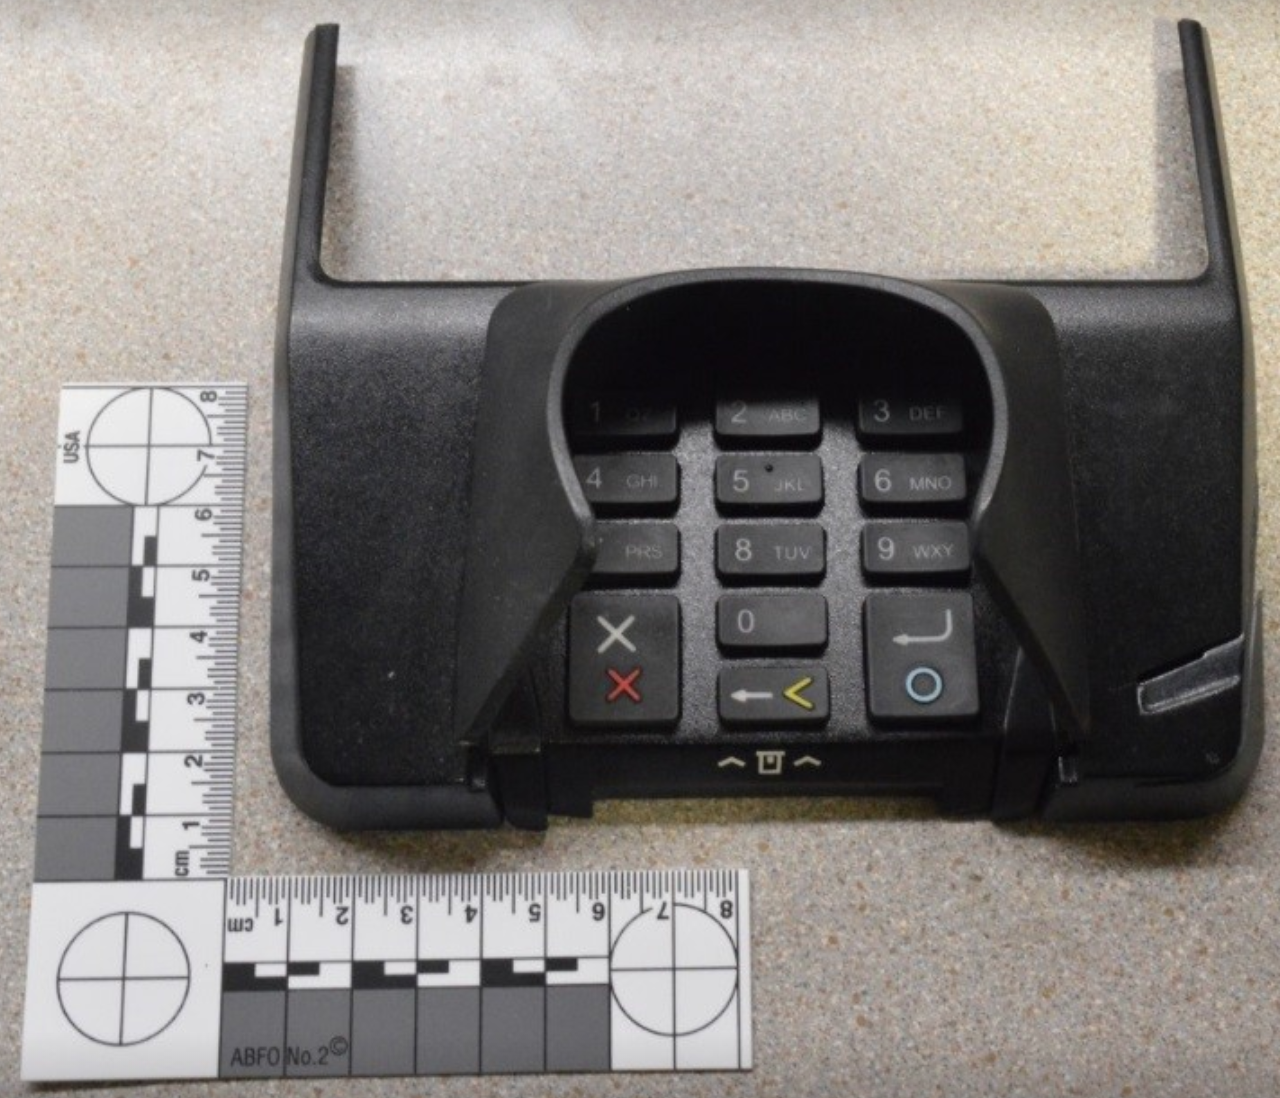
Would You Have Spotted This Skimmer?

Credit to Author: BrianKrebs| Date: Tue, 06 Feb 2018 14:53:42 +0000

When you realize how easy it is for thieves to compromise an ATM or credit card terminal with skimming devices, it’s difficult not to inspect or even pull on these machines when you’re forced to use them personally — half expecting something will come detached. For those unfamiliar with the stealth of these skimming devices and the thieves who install them, read on.

Read More
IndependentKrebs

Alleged Spam Kingpin ‘Severa’ Extradited to US

Credit to Author: BrianKrebs| Date: Mon, 05 Feb 2018 18:28:30 +0000

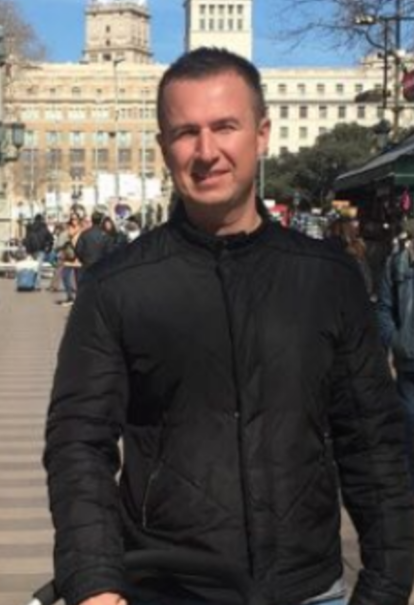
Peter Yuryevich Levashov, a 37-year-old Russian computer programmer thought to be one of the world’s most notorious spam kingpins, has been extradited to the United States to face federal hacking and spamming charges. Levashov, who allegedly went by the hacker name “Peter Severa,” or “Peter of the North,” hails from St. Petersburg in northern Russia, but he was arrested last year while in Barcelona, Spain with his family. Authorities have long suspected he is the cybercriminal behind the once powerful spam botnet known as Waledac (a.k.a. “Kelihos”), a now-defunct malware strain responsible for sending more than 1.5 billion spam, phishing and malware attacks each day.

Read More
IndependentKrebs

Attackers Exploiting Unpatched Flaw in Flash

Credit to Author: BrianKrebs| Date: Fri, 02 Feb 2018 14:21:06 +0000

Adobe warned on Thursday that attackers are exploiting a previously unknown security hole in its Flash Player software to break into Microsoft Windows computers. Adobe said it plans to issue a fix for the flaw in the next few days, but now might be a good time to check your exposure to this still-ubiquitous program and harden your defenses. Adobe said a critical vulnerability (CVE-2018-4878) exists in Adobe Flash Player 28.0.0.137 and earlier versions. Successful exploitation could potentially allow an attacker to take control of the affected system.

Read More
IndependentKrebs

Drugs Tripped Up Suspects In First Known ATM “Jackpotting” Attacks in the US

Credit to Author: BrianKrebs| Date: Tue, 30 Jan 2018 17:26:06 +0000

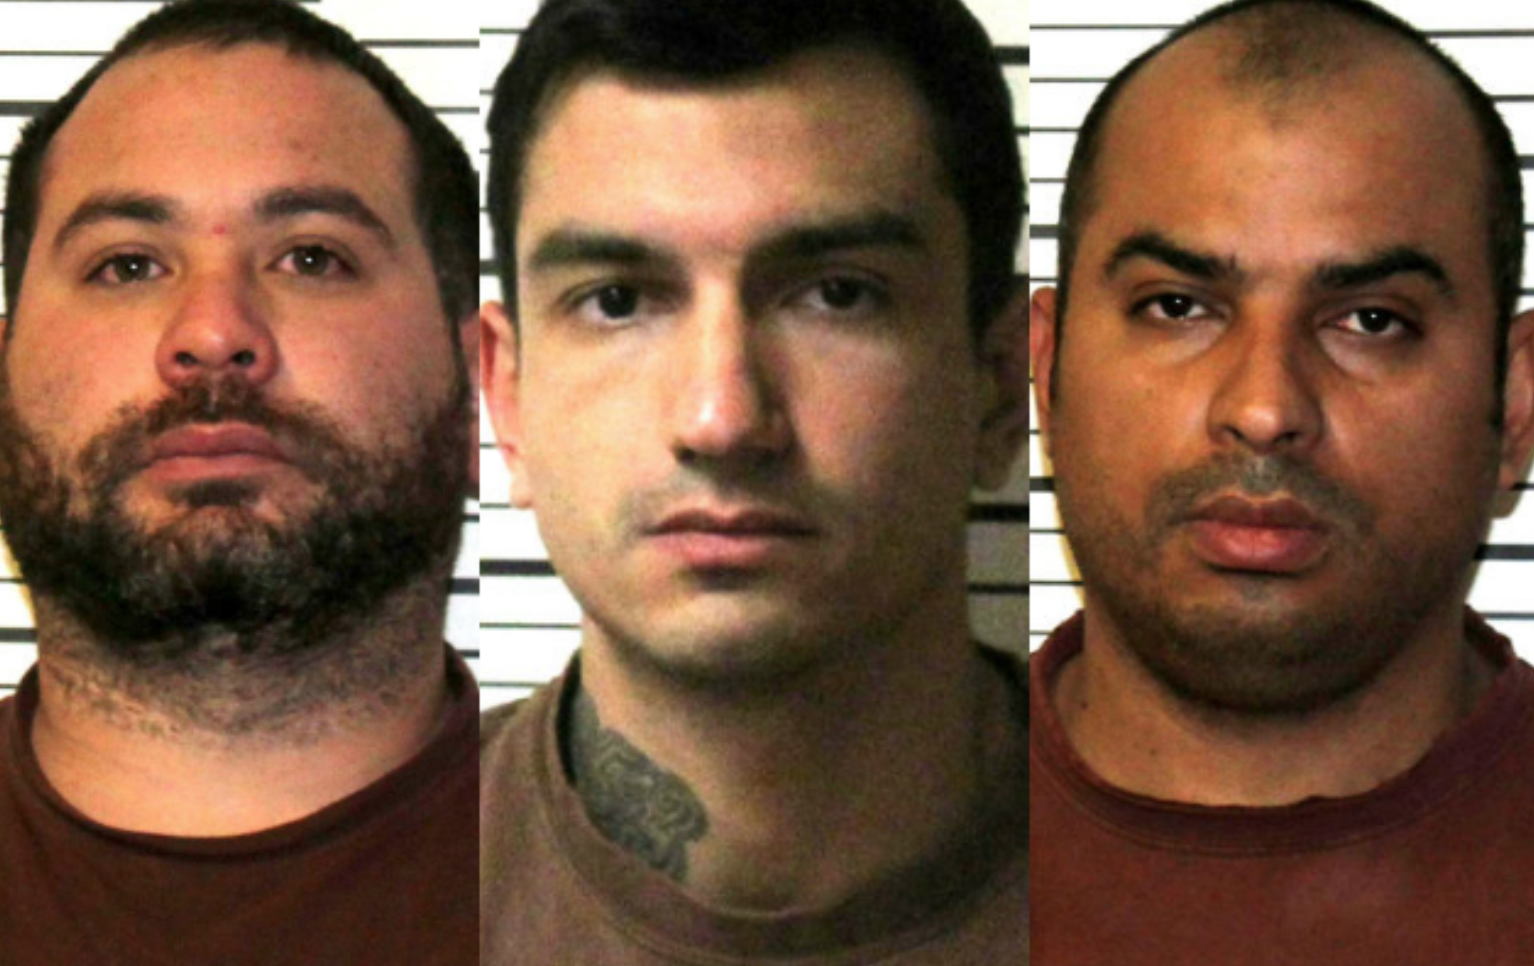
On Jan. 27, 2018, KrebsOnSecurity published what this author thought a scoop about the first known incidence of U.S. ATMs being hit with “jackpotting” attacks, a crime in which thieves deploy malware that forces cash machines to spit out money like a loose Las Vegas slot machine. As it happens, the first known jackpotting attacks in the United States were reported in November 2017 by local media on the west coast, although the reporters in those cases seem to have completely buried the lede.

Read More
IndependentKrebs

Drug Charges Tripped Up Suspects In First Known ATM “Jackpotting” Attacks in the US

Credit to Author: BrianKrebs| Date: Tue, 30 Jan 2018 17:26:06 +0000

On Jan. 27, 2018, KrebsOnSecurity published what this author thought a scoop about the first known incidence of U.S. ATMs being hit with “jackpotting” attacks, a crime in which thieves deploy malware that forces cash machines to spit out money like a loose Las Vegas slot machine. As it happens, the first known jackpotting attacks in the United States were reported in November 2017 by local media on the west coast, although the reporters in those cases seem to have completely buried the lede.

Read More