IndependentKrebs

Global ‘Wana’ Ransomware Outbreak Earned Perpetrators $26,000 So Far
Credit to Author: BrianKrebs| Date: Sat, 13 May 2017 20:10:43 +0000

As thousands of organizations work to contain and clean up the mess from this week’s devastating Wana ransomware attack, the fraudsters responsible for releasing the digital contagion are no doubt counting their earnings and congratulating themselves on a job well done. But according to a review of the Bitcoin addresses hard-coded into Wana, it appears the perpetrators of what’s being called the worst ransomware outbreak ever have made little more than USD $26,000 so far from the scam.

Read More
QuickHealSecurity

MS17-010 – Windows SMB server exploitation leads to ransomware outbreak

Credit to Author: Pradeep Kulkarni| Date: Sat, 13 May 2017 15:08:03 +0000

The Microsoft Windows SMB (Server Message Block) is being actively exploited in the wild, post the Shadow Brokers (TSB) leak in April 2017. According to Microsoft’s blog, the exploits were already covered in previously released security bulletins. The Shadow Broker exploits named ‘EternalBlue’ and ‘EternalRomance’ and ‘EternalSynergy’ are addressed by…

The post MS17-010 – Windows SMB server exploitation leads to ransomware outbreak appeared first on Quick Heal Technologies Security Blog | Latest computer security news, tips, and advice.

Read More
QuickHealSecurity

WannaCry Ransomware Creating Havoc Worldwide by Exploiting Patched Windows Exploit!

Credit to Author: Rajib Singha| Date: Sat, 13 May 2017 14:13:01 +0000

Ransomware are causing major disruptions in recent years. Recently leaked dump of NSA EternalBlue exploit is used by cybercriminals to spread WannaCry ransomware worldwide. Dump of MS-17-010 Windows OS Vulnerability was made public by the notorious Shadow Broker group on 14th April, 2017. This vulnerability affects most of the desktop…

The post WannaCry Ransomware Creating Havoc Worldwide by Exploiting Patched Windows Exploit! appeared first on Quick Heal Technologies Security Blog | Latest computer security news, tips, and advice.

Read More
ComputerWorldIndependent

'Kill switch' helps slow the spread of WannaCry ransomware

Credit to Author: Michael Kan| Date: Fri, 12 May 2017 18:24:00 -0700

Friday’s unprecedented ransomware attack may have stopped spreading to new machines — at least briefly — thanks to a “kill switch” that a security researcher has activated.

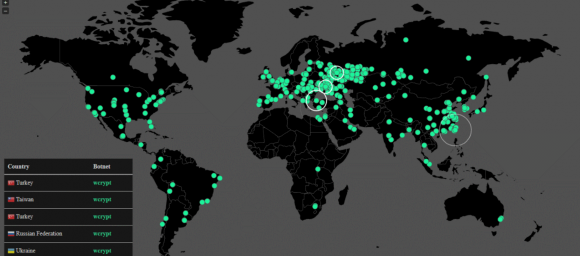
The ransomware, called Wana Decryptor or WannaCry, has been found infecting machines across the globe. It works by exploiting a Windows vulnerability that the U.S. National Security Agency may have used for spying.

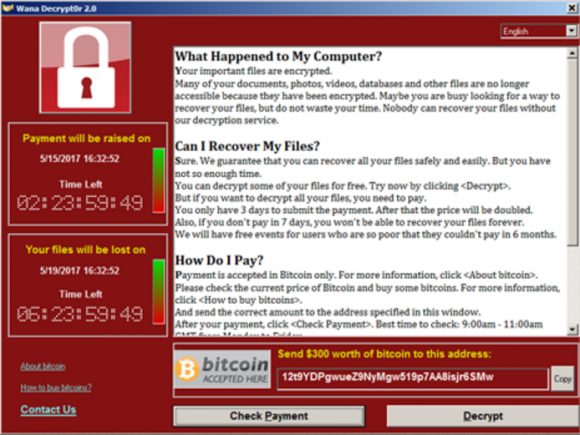
The malware encrypts data on a PC and shows users a note demanding $300 in bitcoin to have their data decrypted. Images of the ransom note have been circulating on Twitter. Security experts have detected tens of thousands of attacks, apparently spreading over LANs and the internet like a computer worm.

To read this article in full or to leave a comment, please click here

Read More
MalwareBytesSecurity

The worm that spreads WanaCrypt0r

Credit to Author: Zammis Clark| Date: Fri, 12 May 2017 22:02:24 +0000

WanaCrypt0r is a ransomware infection that has spread through many corporate networks. Read a technical analysis of the worm that allowed it to do this.

Categories:

Tags:

(Read more…)

The post The worm that spreads WanaCrypt0r appeared first on Malwarebytes Labs.

Read More