Author: admin

SecuritySophos

¡Qué década! Las peores historias y las lecciones más importantes, año tras año

Credit to Author: Naked Security| Date: Thu, 26 Dec 2019 13:09:39 +0000

Aquí están: las peores historias y las lecciones más importantes desde 2010 a 2019. Desde un engaño totalmente inventado que conmocionó al mundo, a través de una app de una red social que prometía lo que no podía ofrecer, hasta la ciber-celebridad más grande que fue arrestada en una operación tipo militar, esta es nuestra [&#8230;]<img src=”http://feeds.feedburner.com/~r/sophos/dgdY/~4/YwpCTcEGkhA” height=”1″ width=”1″ alt=””/>

Read More
SecuritySophos

Nueva campaña de phishing suplantando a Correos

Credit to Author: Sophos Iberia| Date: Tue, 24 Dec 2019 09:50:43 +0000

La Oficina de Seguridad del Internauta (OS) alerta sobre la detección de una campaña de envío de correos electrónicos falsos que suplantan la identidad de Correos. El objetivo es conseguir los datos financieros de las víctimas, engañándolos para que los introduzcan en un página web falsa que simula ser de correos. Detalles El email fraudulento [&#8230;]<img src=”http://feeds.feedburner.com/~r/sophos/dgdY/~4/d61szjq6u1A” height=”1″ width=”1″ alt=””/>

Read More
SecuritySophos

La política de seguimiento de ubicación de Facebook todavía preocupa a los senadores estadounidenses

Credit to Author: Naked Security| Date: Mon, 23 Dec 2019 12:36:33 +0000

En noviembre, los senadores estadounidenses Josh Hawley y Chris Coons realizaron a Mark Zuckerberg, una importante pregunta sobre la privacidad: ¿Facebook sigue rastreando las ubicaciones de sus usuarios incluso cuando le han pedido que no lo haga? Esta semana, en una respuesta filtrada a The Hill, obtuvieron la respuesta: sí. El alboroto comenzó en septiembre [&#8230;]<img src=”http://feeds.feedburner.com/~r/sophos/dgdY/~4/a-h8nWwLj0U” height=”1″ width=”1″ alt=””/>

Read More
SecurityTrendMicro

This Week in Security News: INTERPOL Collaboration Reduces Cryptojacking by 78% and Three Malicious Apps Found on Google Play May be Linked to SideWinder APT Group

Credit to Author: Jon Clay (Global Threat Communications)| Date: Fri, 10 Jan 2020 13:37:59 +0000

Welcome to our weekly roundup, where we share what you need to know about the cybersecurity news and events that happened over the past few days. This week, learn about how Trend Micro’s collaboration with INTERPOL’s Global Complex for Innovation helped reduce cryptojacking by 78% in Southeast Asia. Also, read about three malicious apps in…

The post This Week in Security News: INTERPOL Collaboration Reduces Cryptojacking by 78% and Three Malicious Apps Found on Google Play May be Linked to SideWinder APT Group appeared first on .

Read More
IndependentKrebs

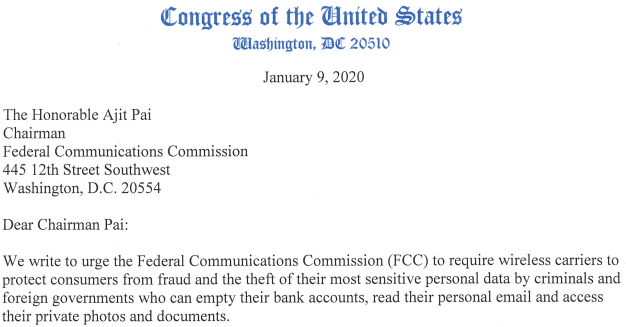
Lawmakers Prod FCC to Act on SIM Swapping

Credit to Author: BrianKrebs| Date: Thu, 09 Jan 2020 19:44:55 +0000

Crooks have stolen tens of millions of dollars and other valuable commodities from thousands of consumers via “SIM swapping,” a particularly invasive form of fraud that involves tricking a target’s mobile carrier into transferring someone’s wireless service to a device they control. But the U.S. Federal Communications Commission (FCC), the entity responsible for overseeing wireless industry practices, has so far remained largely silent on the matter. Now, a cadre of Senate lawmakers is demanding to know what, if anything, the agency might be doing to track and combat SIM swapping.

Read More
ComputerWorldIndependent

Mozilla patches Firefox zero-day as attackers exploit flaw

Credit to Author: Gregg Keizer| Date: Thu, 09 Jan 2020 11:46:00 -0800

Just one day after releasing Firefox 72, Mozilla updated the browser with a fix to shut down active attacks, the company acknowledged.

On Wednesday, Mozilla issued Firefox 72.0.1, which included one change: A patch for the vulnerability identified as CVE-2019-17026. “We are aware of targeted attacks in the wild abusing this flaw,” Mozilla said in the short description of the flaw, signaling that criminals were already leveraging the zero-day vulnerability, the term applied because there no time elapses between patching and exploitation.

To read this article in full, please click here

Read More
ScadaICSSchneider

As Digital Transformations Continue in 2020, Industrial Edge Plays a Starring Role

Credit to Author: Vincenzo Salmeri| Date: Thu, 09 Jan 2020 17:20:00 +0000

As we turn our sights to a new decade in 2020, it’s a good time to take stock of trends and opportunities facing commercial and industrial businesses and assess what… Read more »

The post As Digital Transformations Continue in 2020, Industrial Edge Plays a Starring Role appeared first on Schneider Electric Blog.

Read More