Author: admin

IndependentKrebs

Microsoft: Two New 0-Day Flaws in Exchange Server

Credit to Author: BrianKrebs| Date: Fri, 30 Sep 2022 16:51:57 +0000

Microsoft Corp. is investigating reports that attackers are exploiting two previously unknown vulnerabilities in Exchange Server, a technology many organizations rely on to send and receive email. Microsoft says it is expediting work on software patches to plug the security holes. In the meantime, it is urging a subset of Exchange customers to enable a setting that could help mitigate ongoing attacks.

Read More
IndependentKrebs

Fake CISO Profiles on LinkedIn Target Fortune 500s

Credit to Author: BrianKrebs| Date: Thu, 29 Sep 2022 20:52:43 +0000

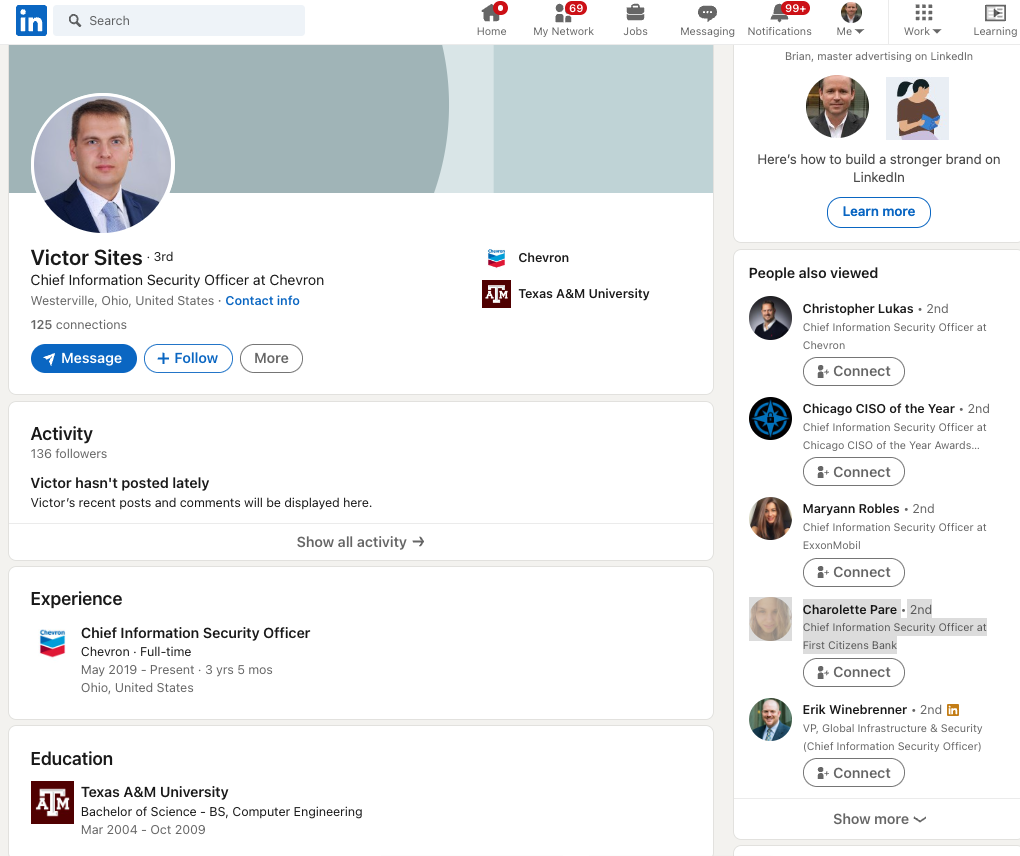
Someone has recently created a large number of fake LinkedIn profiles for Chief Information Security Officer (CISO) roles at some of the world’s largest corporations. It’s not clear who’s behind this network of fake CISOs or what their intentions may be. But the fabricated LinkedIn identities are confusing search engine results for CISO roles at major companies, and they are being indexed as gospel by various downstream data-scraping sources.

Read More
MalwareBytesSecurity

Optus data breach “attacker” says sorry, it was a mistake

Categories: News

Tags: Optus

Tags: breach

Tags: optusdata

Tags: text messages

Tags: drivers’ licenses

Tags: Medicare

Tags: identity protection

A hacker stole the personal information of 10 million Optus customers, threatened to publish them in lots of 10,000 a day unless the ransom was paid, and then suddenly did a 180 degree turn.

(Read more…)

The post Optus data breach “attacker” says sorry, it was a mistake appeared first on Malwarebytes Labs.

Read More