MicrosoftSecurity

Microsoft AI Red Team building future of safer AI

Credit to Author: Ram Shankar Siva Kumar| Date: Mon, 07 Aug 2023 15:00:00 +0000

We’re sharing best practices from our team so others can benefit from Microsoft’s learnings. These best practices can help security teams proactively hunt for failures in AI systems, define a defense-in-depth approach, and create a plan to evolve and grow your security posture as generative AI systems evolve.

The post Microsoft AI Red Team building future of safer AI appeared first on Microsoft Security Blog.

Read More
ScadaICSSchneider

Focus on Hydrogen Safety Aligns with Growing Economy

Credit to Author: Constantine Lau| Date: Tue, 08 Aug 2023 14:00:00 +0000

Hydrogen is projected to be a major source of clean energy that would be an integral part of energies and chemicals companies’ net-zero strategy, increasing the need for hydrogen safety processes, systems, and best practices. Hydrogen is a transportable energy carrier and has high energy…

The post Focus on Hydrogen Safety Aligns with Growing Economy appeared first on Schneider Electric Blog.

Read More
ScadaICSSchneider

Are we right about DCIM 3.0? 1 year later, signs point to yes.

Credit to Author: Kevin Brown| Date: Tue, 08 Aug 2023 12:00:00 +0000

A year ago we coined the term DCIM 3.0 to describe the evolution we were seeing in the Data Center Infrastructure Management software marketplace. Namely that new challenges would drive a trend to a ‘next generation DCIM’. DCIM 3.0 identifies 3 waves of this software…

The post Are we right about DCIM 3.0? 1 year later, signs point to yes. appeared first on Schneider Electric Blog.

Read More
ComputerWorldIndependent

Researchers build a scary Mac attack using AI and sound

A UK research team based at Durham University has identified an exploit that could allow attackers to figure out what you type on your MacBook Pro — based on the sound each keyboard tap makes.

These kinds of attacks aren’t particularly new. The researchers found research dating back to the 1950s into using acoustics to identify what people write. They also note that the first paper detailing use of such an attack surface was written for the US National Security Agency (NSA) in 1972, prompting speculation such attacks may already be in place.

“(The) governmental origin of AS- CAs creates speculation that such an attack may already be possible on modern devices, but remains classified,” the researchers wrote.

To read this article in full, please click here

Read More
IndependentKrebs

Meet the Brains Behind the Malware-Friendly AI Chat Service ‘WormGPT’

Credit to Author: BrianKrebs| Date: Tue, 08 Aug 2023 17:37:23 +0000

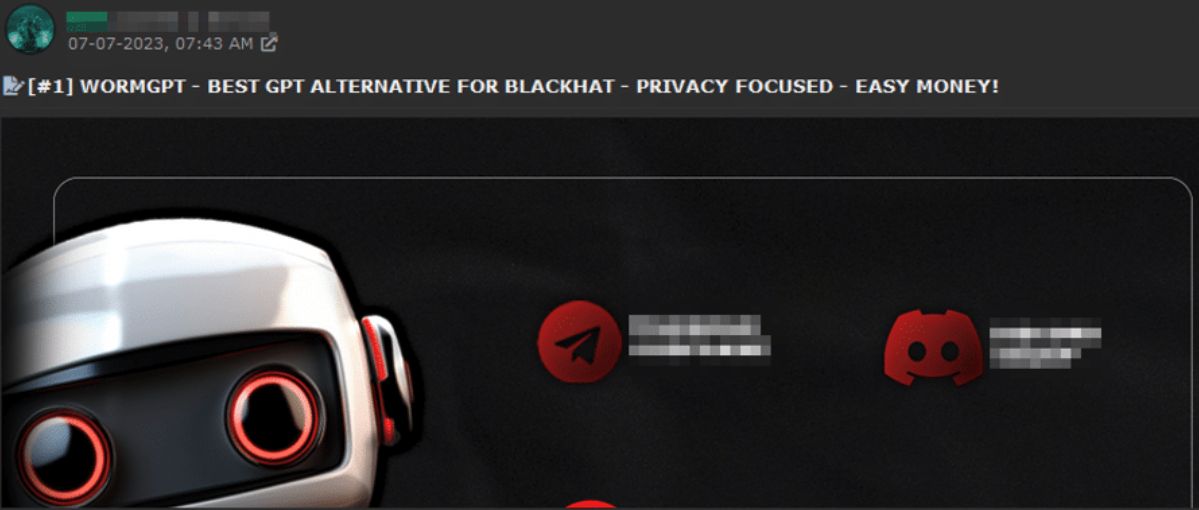
WormGPT, a private new chatbot service advertised as a way to use Artificial Intelligence (AI) to help write malicious software without all the pesky prohibitions on such activity enforced by ChatGPT and Google Bard, has started adding restrictions on how the service can be used. Faced with customers trying to use WormGPT to create ransomware and phishing scams, the 23-year-old Portuguese programmer who created the project now says his service is slowly morphing into “a more controlled environment.” The large language models (LLMs) made by ChatGPT parent OpenAI or Google or Microsoft all have various safety measures designed to prevent people from abusing them for nefarious purposes — such as creating malware or hate speech. In contrast, WormGPT has promoted itself as a new LLM that was created specifically for cybercrime activities.

Read More