Credit to Author: Microsoft Threat Intelligence| Date: Fri, 14 Jul 2023 17:00:00 +0000
Analysis of the techniques used by the threat actor tracked as Storm-0558 for obtaining unauthorized access to email data, tools, and unique infrastructure characteristics.
With this month’s Patch Tuesday update, Microsoft addressed 130 security vulnerabilities, published two advisories, and included four major CVE revisions. We also have four zero-days to manage for Windows (CVE-2023-32046, CVE-2023-32049, CVE-2023-36874 and CVE-2023-36884), bringing the Windows platform into a “patch now” schedule.
The FBI has collected sensitive data on millions of Americans without warrants, drawing intense scrutiny from Congress and turning the agency into a punching bag across the political divide.
Credit to Author: Daniel Lunghi| Date: Fri, 14 Jul 2023 00:00:00 +0000
We recently found that an MSI installer built by the National Information Technology Board (NITB), a Pakistani government entity, delivered a Shadowpad sample, suggesting a possible supply-chain attack.
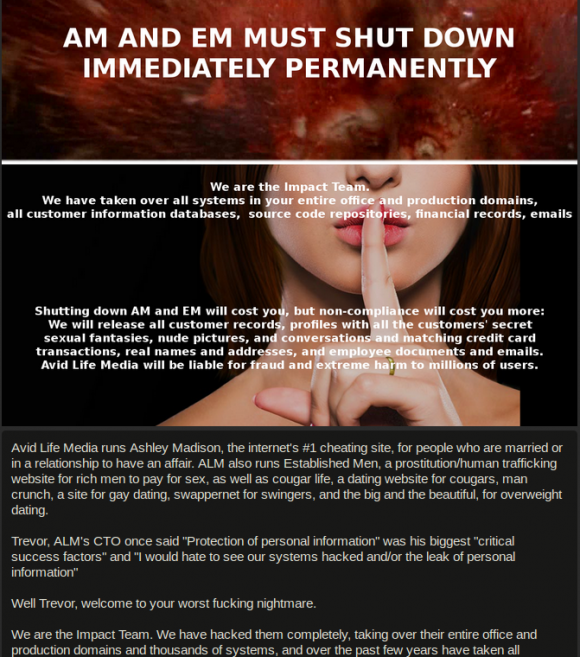
[This is Part II of a story published here last week on reporting that went into a new Hulu documentary series on the 2015 Ashley Madison hack.] It was around 9 p.m. on Sunday, July 19, when I received a message through the contact form on KrebsOnSecurity.com that the marital infidelity website AshleyMadison.com had been hacked. The message contained links to confidential Ashley Madison documents, and included a manifesto that said a hacker group calling itself the Impact Team was prepared to leak data on all 37 million users unless Ashley Madison and a sister property voluntarily closed down within 30 days.