Security

ComputerWorldIndependent

IDG Contributor Network: 94% of Microsoft vulnerabilities can be easily mitigated
Credit to Author: Andy Patrizio| Date: Sat, 25 Feb 2017 21:18:00 -0800

If you want to shut out the overwhelming majority of vulnerabilities in Microsoft products, turn off admin rights on the PC.

That’s the conclusion from global endpoint security firm Avecto, which has issued its annual Microsoft Vulnerabilities report. It found that there were 530 Microsoft vulnerabilities reported in 2016, and of these critical vulnerabilities, 94% were found to be mitigated by removing admin rights, up from 85% reported last year.

This is especially true with the browser, for those who still use Microsoft’s browsers. 100% of vulnerabilities impacting both Internet Explorer and Edge could be mitigated by removing admin rights, Avecto reported. One bit of progress is that 109 vulnerabilities impacting IE 6 through 11 were reported in 2016, way down from 238 in the previous year.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Google discloses unpatched IE flaw after Patch Tuesday delay

Credit to Author: Lucian Constantin| Date: Fri, 24 Feb 2017 10:44:00 -0800

Google’s Project Zero team has disclosed a potential arbitrary code execution vulnerability in Internet Explorer because Microsoft has not acted within Google’s 90-day disclosure deadline.

This is the second flaw in Microsoft products made public by Google Project Zero since the Redmond giant decided to skip this month’s Patch Tuesday and postpone its previously planned security fixes until March.

Microsoft blamed the unprecedented decision to push back scheduled security updates by a month on a “last minute issue” that could have had an impact on customers, but the company hasn’t clarified the nature of the problem.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

FCC puts the brakes on ISP privacy rules it passed in October

Credit to Author: Grant Gross| Date: Fri, 24 Feb 2017 10:43:00 -0800

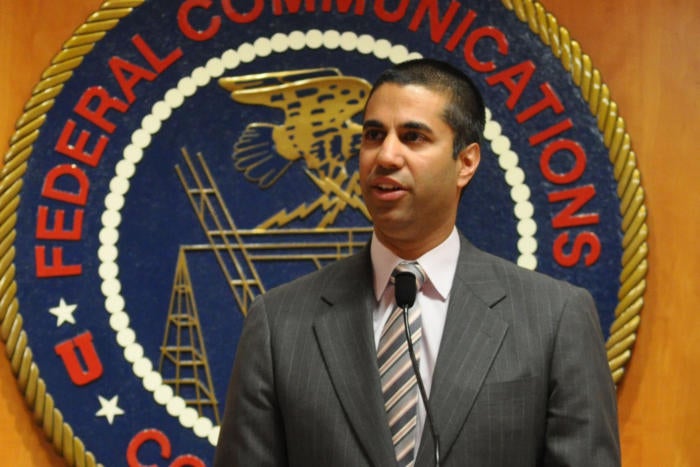
The new chairman of the U.S. Federal Communications Commission will seek a stay on privacy rules for broadband providers that the agency just passed in October.

FCC Chairman Ajit Pai will ask for either a full commission vote on the stay before parts of the rules take effect next Thursday or he will instruct FCC staff to delay part of the rules pending a commission vote, a spokesman said Friday.

The rules, passed when the FCC had a Democratic majority, require broadband providers to receive opt-in customer permission to share sensitive personal information, including web-browsing history, geolocation, and financial details, with third parties. Without the stay, the opt-in requirements were scheduled to take effect next week.

To read this article in full or to leave a comment, please click here

Read More
SecurityTrendMicro

TippingPoint Threat Intelligence and Zero-Day Coverage – Week of February 20, 2017

Credit to Author: Elisa Lippincott (TippingPoint Global Product Marketing)| Date: Fri, 24 Feb 2017 18:45:55 +0000

I’ve been fascinated with the rise and fall of exploit kits, especially the ones that are really popular that disappear seemingly overnight. Angler was one that at one point, contributed 59.5% in the total exploit kit activity for 2015. But now it’s presumed dead as of June 2016 after the arrest of a hacker gang….

Read More