Security

ComputerWorldIndependent

A.I. faces hype, skepticism at RSA cybersecurity show
Credit to Author: Michael Kan| Date: Wed, 15 Feb 2017 17:10:00 -0800

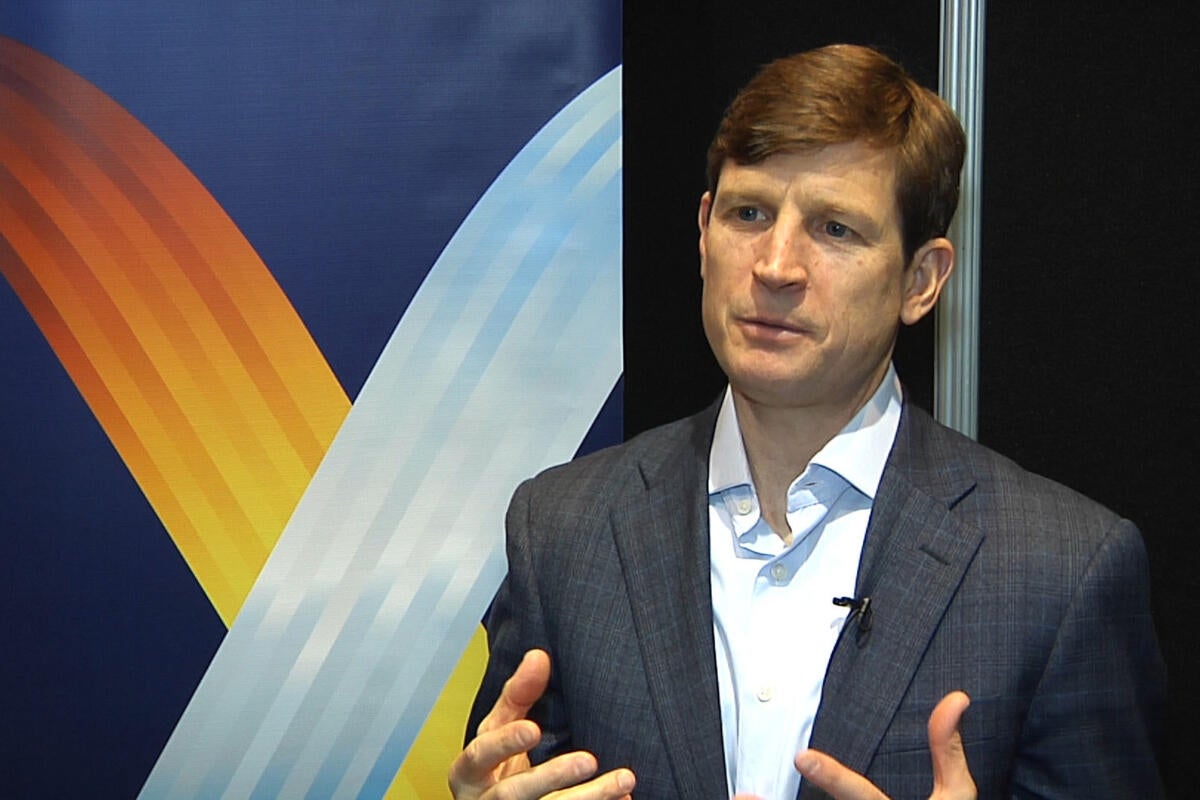
Vendors at this week’s RSA cybersecurity show in San Francisco are pushing artificial intelligence and machine learning as the new way to detect the latest threats, but RSA CTO Zulfikar Ramzan is giving visitors a reality check.

“I think it [the technology] moves the needle,” he said on Wednesday. “The real open question to me is how much has that needle actually moved in practice?”

It’s not as much as vendors claim, Ramzan warned, but for customers it won’t be easy cutting through the hype and marketing. The reality is that a lot of the technology now being pushed isn’t necessarily new.

In particular, he was talking about machine learning, a subfield in A.I. that’s become a popular marketing term in cybersecurity. In practice, it essentially involves building algorithms to spot bad computer behavior from good.

To read this article in full or to leave a comment, please click here
Read More
ComputerWorldIndependent

Sophos CEO sounds the alarm on enterprise ransomware attacks

Credit to Author: Martyn Williams| Date: Wed, 15 Feb 2017 12:32:00 -0800

Ransomware is increasingly becoming a problem for companies, and the CEO of a leading computer security firm says he fears 2017 could see entire companies shut down until they pay up, or risk losing all their data.

Ransomware works by infiltrating a computer with malware and then encrypting all the files on the disk. The user is presented with a limited time offer: Lose all your data or send money with the promise your data will be unlocked. The fee typically varies from tens of dollars to hundreds of dollars and often has to be transmitted in Bitcoin.

The problem began on a fairly small scale, targeting individual users, but has been growing. Last year, a hospital in Los Angeles admitted to paying $17,000 to get its system unlocked, and a report in October said ransomware cases were on course to quadruple in 2016 over the previous year.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

IT leaders say it's hard to keep the cloud safe

Credit to Author: Sharon Gaudin| Date: Wed, 15 Feb 2017 12:17:00 -0800

IT managers are finding it difficult to keep their applications and data safe in the cloud, and many are slowing cloud adoption because of it.

That was one of the findings of an Intel cloud security report that surveyed 2,000 IT professionals in different countries and industries last fall.

The issue isn’t with the cloud itself, since trust outnumbers distrust for public clouds by more than two to one, according to Intel’s survey.

IT professionals told Intel that shadow IT and a shortage of cybersecurity skills are causing the most problems.

To read this article in full or to leave a comment, please click here

Read More
ComputerWorldIndependent

Yahoo warns users of account breaches related to recent attacks

Credit to Author: Grant Gross| Date: Wed, 15 Feb 2017 11:01:00 -0800

Yahoo has begun warning individual users that their accounts with the service may have been compromised in a massive data breach it reported late last year.

The warning, in email messages sent from Yahoo CISO Bob Lord, tell users that a forged cookie may have been used to access their accounts in previous years.

The warning to Yahoo users come at the same time that news reports suggest that Verizon Communications, in negotiations to buy Yahoo, may be seeking a discount of $250 million because of the data breaches.

To read this article in full or to leave a comment, please click here
Read More
ComputerWorldIndependent

Hacker breached 63 universities and government agencies

Credit to Author: Darlene Storm| Date: Wed, 15 Feb 2017 09:33:00 -0800

A “Russian-speaking and notorious financially-motivated” hacker known as Rasputin has been at it again, hacking into universities and government agencies this time, before attempting to sell the stolen data on the dark web.

According to the security company Recorded Future, which has been tracking the cybercriminal’s breaches, Rasputin’s most recent victims include 63 “prominent universities and federal, state, and local U.S. government agencies.” The security firm has been following Rasputin’s activity since late 2016 when the hacker reportedly breached the U.S. Electoral Assistance Commission and then sold EAC access credentials.

To read this article in full or to leave a comment, please click here

Read More